All Articles
Security Intelligence
3730 articles · Updated every 8 hours
Advertisement
Recorded Future's AI Indicator Lists Enhance Governance
Recorded Future introduces AI Infrastructure Indicator Lists to identify and monitor AI-related network traffic, addressing shadow AI and data exposure risks.
AI Agent Social Engineering: The Future of BEC by 2026
Future BEC attacks may target AI agents with growing business system authority, necessitating new defensive strategies for 2026.
Weekly Threat Roundup: AI Banking Attacks & Nvidia Vulnerability
Explore this week's key cybersecurity news, including PoeLLM botnets, South Korean banking attacks, and Nvidia GPU monitoring flaws.
Securing AI Agent Permissions: Preventing Cloud Data Loss
AI agents can escalate privileges and perform unauthorized actions, leading to data loss. Learn how to implement granular controls for tool calls.
TP-Link Sued: Router Security Misrepresentation & China Ties
Four U.S. states sue TP-Link over allegations of misleading security claims, undisclosed China ties, and privacy risks affecting consumer routers.
AgentCorruption: AWS Bedrock AgentCore Fleet Takeover Via Single Prompt
Analysis of 'AgentCorruption,' a patched vulnerability in AWS Bedrock AgentCore allowing compromise of an entire fleet via a single AI chatbot.
Advertisement
FBI Disrupts Flax Typhoon Hacking Tools Targeting Critical Infra
The FBI seized domains linked to Chinese state-sponsored Flax Typhoon, disrupting MicroScan and FishHub tools used to breach critical infrastructure worldwide.
ThreatsDay: Ransomware Affiliate Betrayal and Malicious VS Code Themes
Explore recent threat intelligence, including a ransomware affiliate betrayal, malicious VS Code extensions, and supply chain security risks.
CVE-2015-3306: ProFTPD Improper Access Control Exploitation
Critical improper access control vulnerability in ProFTPD (CVE-2015-3306) allows remote file manipulation, actively exploited.
CVE-2021-3199: ONLYOFFICE Docs RCE via Path Traversal
Actively exploited path traversal vulnerability [CVE-2021-3199] in ONLYOFFICE Docs Server enables remote code execution when JWT is used. Immediate patching is critical.
CVE-2023-22894: Strapi Cleartext Storage Exploited
CISA confirms active exploitation of CVE-2023-22894, a Strapi cleartext storage vulnerability exposing sensitive user data, potentially chained for RCE.
CVE-2016-3081: Apache Struts RCE via Command Injection — Patch Now
CISA confirms active exploitation of CVE-2016-3081, an Apache Struts command injection flaw leading to remote code execution.
CVE-2015-5477: Remote DoS in ISC BIND via TKEY Queries
CISA confirms active exploitation of CVE-2015-5477, a remote Denial of Service vulnerability in ISC BIND affecting critical DNS infrastructure.
Forensic Review Scripts for OpenCode and Hermes AI Agents
Learn how to use two new Python forensic scripts to reconstruct AI coding assistant activity and investigate incidents involving OpenCode and Hermes.
Venezuelan Cartel's Malware Honcho Nabbed for ATM Jackpotting
Cybercriminal linked to Venezuela's Tren de Aragua cartel arrested for ATM jackpotting operations, highlighting cyber-physical crime convergence.
Cisco Patches 35 Vulnerabilities: Critical Flaws in Meraki, NX-OS
Cisco released patches for 35 vulnerabilities, including multiple critical issues in Meraki, License On-Prem, NX-OS, and APIC products.
Ransomware Disrupts Japan's IDCF Cloud, Affecting Gov't Clients
IDC Frontier's IDCF Cloud suffered a ransomware attack impacting its East Japan Region 1, disrupting services for 495 companies and local governments.
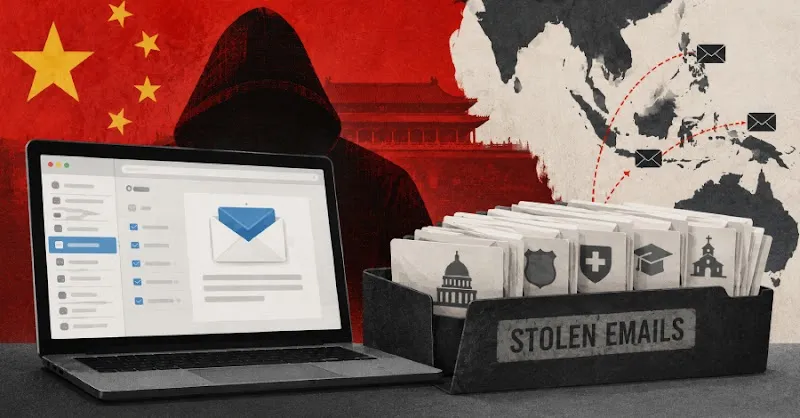
China-Linked Hackers Run Portal for Stolen Email Access
FBI and international agencies reveal a China-linked firm operated a portal giving third parties access to stolen emails from government and healthcare targets.
Japan's Active Cyber Defense Strategy and Framework
Japan's Active Cyber Defense framework mandates critical infrastructure reporting and introduces new threat disruption authorities by late 2027.
Malware Uses AI-Analysis Evasion to Deceive Security Tools
Malware authors are developing "AI-analysis evasion" techniques, embedding natural-language instructions to mislead automated security tools.
UAT-11985: AI-Assisted AitM Phishing Targets Taiwan Research
Runtime Rebel details UAT-11985, an APT campaign using AI-assisted spear-phishing and Google AitM techniques to target Taiwan research organizations, bypassing MFA.
AI: Empowering & Imperiling Autocrats' Control
AI offers autocrats unprecedented tools for surveillance, propaganda, and automating control, yet creates new dependencies on a 'digital Praetorian Guard'.
Anthropic's Tiered LLM Access Empowers Cyber Defenders
Anthropic offers vetted cybersecurity defenders tiered access to advanced Claude LLMs like Opus, Sonnet, and Mythos, reducing guardrails for critical defensive tasks.
Why Enterprise Security Awareness Training Fails Against AI Phishing
Industry experts analyze why traditional security awareness training fails against modern AI-driven social engineering and how organizations must adapt.