Coverage
Data Breaches
478 articles on breaches and ransomware
Advertisement
Ransomware Groups Exploit Insiders: A Shifting Threat Landscape
Ransomware groups are increasingly recruiting insiders to bypass advanced security, posing a significant threat to organizational data and operations.
39 Methods Compromise Passkey Authentication: Threat Analysis
Discover 39 published methods compromising passkey authentication, focusing on ecosystem flaws, UI manipulation, and enrollment abuse.
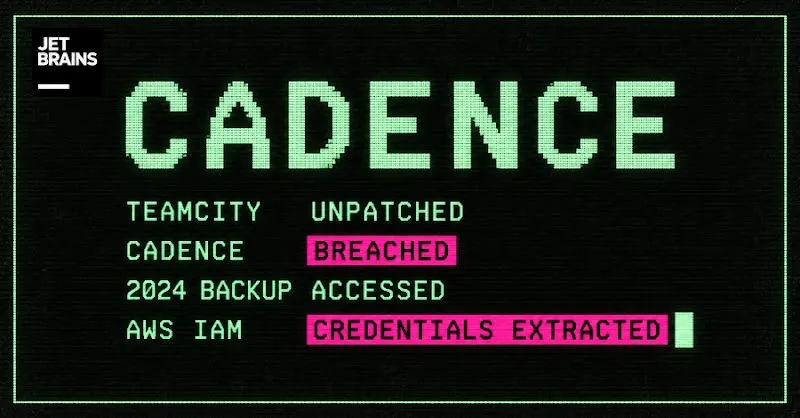
CVE-2026-63077: JetBrains Cadence Breach Exposes Credentials
JetBrains Cadence suffered a data breach via unpatched TeamCity (CVE-2026-63077), exposing AWS credentials, source code, and user data. Immediate action required.
IDScan Sued Over Alleged Breach Impacting 153 Million Drivers
IDScan faces lawsuits after a dark-web service allegedly offered to sell 153 million driver's licenses and millions of other identity documents.
ShinyHunters: Dark Reading on Potential ReliaQuest Breach
Dark Reading editors discuss the latest activities of the ShinyHunters threat group, including inquiries into a potential breach affecting ReliaQuest.
French Hospital Fined €500K for GDPR Data Breach
France's CNIL fined Hôpital privé de la Loire €500,000 after a data breach exposed sensitive medical data of 727,000 patients.
Microsoft Teams Abuse, The Gentlemen Ransomware, and PhaaS Trends
Analysis of social engineering campaigns via Microsoft Teams, The Gentlemen ransomware operations, and emerging phishing-as-a-service kits.
Manchester Airports Group Data Leak Exposed by FulcrumSec Extortion
FulcrumSec leaks 550GB of data on 8.8 million individuals after Manchester Airports Group refused to pay a ransom demand following a breach.
Silver Fox Malware Campaign Impersonates Software Vendors
An active Silver Fox malware campaign uses fake software download sites to disable Windows Update and weaken Microsoft Defender defenses.
AI-Assisted Cyber Attacks Accelerate Enterprise Breaches
Unit 42 reveals how AI agents dramatically accelerate enterprise network breaches, compressing weeks of attack activity into hours for ransomware operations.
CVE-2026-84115: Cleo Harmony Auth Bypass Exploit Published
An exploit is published for CVE-2026-84115, an authentication bypass in Cleo Harmony allowing remote privilege escalation. Immediate patching to v5.8.1.11 is urged.
Philippines Nuclear Agency Breached via Unpatched ownCloud Flaws
Threat actors exploit unpatched ownCloud vulnerabilities to breach the Philippines nuclear agency, stealing sensitive databases and credentials.
Dark Web Service Nexus Sells 153M+ Driver Licenses
A new dark web service, Nexus, is selling over 153 million drivers' licenses from North America, likely sourced from an identity verification company.
Threat Actors Prefer Repeatable Playbooks Over Novel Exploits
Analysis of modern cyberattacks reveals threat actors increasingly favour scalable, repeatable playbooks over novel exploit development.
Rogue LLM Endpoints: Data Exposure & RCE Risk for AI Agents
Unverified LLM endpoints pose significant risks, enabling data leakage and potential remote code execution via compromised AI agent sessions.
Infostealers Target Anthropic Claude Users via Session Theft
Threat actors are employing various infostealers to compromise Anthropic Claude user accounts via session theft, posing significant risks.
Cronos Blockchain Halted After $6M Tectonic DeFi Exploit
A price manipulation attack on Tectonic’s TONIC token led to a $6M Ethereum theft from the Cronos blockchain, forcing an emergency network restart.
Nutex Health Suffers Data Breach, Sensitive Data Exfiltrated
Nutex Health experienced a data breach exposing patient, employee, and operational data. The company is assessing the full impact.
Mexico’s Cybersecurity Plan 2025-2030: Addressing Rising Threats
Mexico's National Cybersecurity Plan 2025-2030 aims to strengthen defenses against ransomware, state-sponsored espionage, and cybercrime.
State of AI-Enabled Malware: Real-World Impact and Defenses
Unit 42 reports AI-enabled malware is primarily proof-of-concept, with minimal operational activity. Existing defenses effectively detect current threats.
Cybersecurity Affordability Crisis: Impact on Small Businesses
Rising breach costs and defense spending strain budgets, leaving small businesses dangerously exposed and elevating supply chain risks.
CVE-2026-21962: Oracle WebLogic RCE Under Active Attack
CISA urges immediate patching for CVE-2026-21962, a critical Oracle WebLogic Server Proxy plugin vulnerability actively exploited in the wild.
SynkLoader Multitool Malware Employs Screen Hijacking
SynkLoader multitool malware leverages screen hijacking techniques and novel features for password theft, signaling potential ransomware threats.
ReliaQuest Thwarts ShinyHunters Social Engineering Attack on Okta SSO
ReliaQuest confirms a social engineering attack by ShinyHunters targeting an employee's Okta SSO, blocked from accessing applications or customer data.