Australia Focus
Australia Threat Intelligence
Coverage affecting Australian organisations, government and critical infrastructure — selected from the full archive by title, description and tags. For national alerts and advisories, see the Australian Cyber Security Centre.
Severity snapshot
Last 30 days (2 articles)
- Critical 0
- High 0
- Medium 1
- Low 0
- Info 1
All time (15 articles)
- Critical 1
- High 8
- Medium 2
- Low 0
- Info 4
Latest Australian coverage
TeamPCP Hackers Arrested in Australia Over Supply Chain Attacks
Australian Federal Police arrest two men linked to TeamPCP, a cybercrime syndicate behind major software supply chain attacks and data extortion.
Australia Pilot: Smart Device Security Labelling Scheme
Australia launches a pilot program for smart device security labelling, aiming to empower consumers with clear information on IoT product security.
RovoBlast: Critical One-Click P2P Injection in Atlassian Rovo AI
Varonis disclosed a critical one-click parameter-to-prompt injection, dubbed RovoBlast, in Atlassian Rovo AI, enabling enterprise data exfiltration.
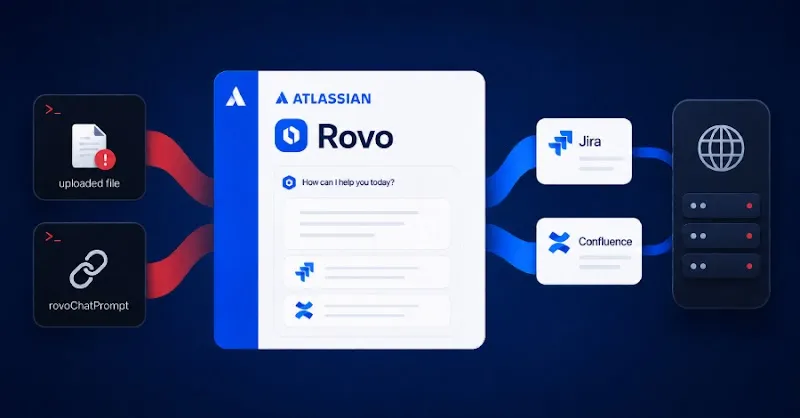
Atlassian Rovo Indirect Prompt Injection Exfiltrates Jira Data
Atlassian Rovo is vulnerable to indirect prompt injection and URL parameter manipulation, leaking Jira and Confluence data to external servers.
CISA & ACSC Advise Isolating OT Systems During Cyberattacks
CISA and ACSC urge critical infrastructure to prepare isolating operational technology systems during cyberattacks to maintain essential services and limit impact.
Origin Energy Data Breach: 900,000 Australians Affected
An unauthorized breach of Origin Energy systems has exposed personal data for approximately 900,000 Australian customers. Understand the impact and recommended actions.
Origin Energy Data Breach: 2 Million Customers' Data Compromised
Australian energy giant Origin Energy confirms a data breach impacting 2 million customers. A hacker claims to have stolen information and threatens public disclosure.
Origin Energy Data Breach Exposes Client PII
Australian energy provider Origin Energy confirms a data breach exposed sensitive Personally Identifiable Information of its clients, heightening fraud risks.
ACSC Warns of Global Campaign Targeting Vulnerable CMS Platforms
The ACSC warns of a global campaign targeting WordPress, Joomla, and Drupal. Learn how to identify web shells and secure your CMS against automated attacks.
Cybercrime Risk Shift: Australian SMBs Under Increased Pressure
Analysis of shifting cybercrime landscape in Australia, detailing how institutional safeguards impact SMBs and necessitate updated defense strategies for small…
The Gentlemen Ransomware Halts Mackay Sugar Operations
Mackay Sugar, Australia's second-largest sugar producer, suffered a ransomware attack by 'The Gentlemen' group, halting mill operations and impacting critical…
ClickFix Attacks Distribute Vidar Stealer: ACSC Warning & Mitigation
The ACSC warns Australian organizations of active ClickFix social engineering attacks deploying Vidar Stealer malware, risking data theft. Learn detection and mitigation.