Coverage
Data Breaches
520 articles on breaches and ransomware
Advertisement
Cisco FMC RCE via CVE-2026-20079: Patch Now
Active exploitation of critical Cisco Secure Firewall Management Center vulnerabilities (CVE-2026-20079, CVE-2026-20316) by state-sponsored and crimeware actors.
KillSec Ransomware Mastermind Arrested: 16-Year-Old Suspect
International law enforcement disrupts the KillSec ransomware operation, arresting an alleged 16-year-old mastermind behind attacks on 500 victims.
ThreatsDay: AI Zero-Day Chains, ATM Jackpotting, and Cache Key Injection
Analysis of recent threat intelligence covering AI-powered zero-day chains, Tren de Aragua ATM jackpotting, and emerging web cache injection techniques.
Tajin Group and Chinese Telegram Guarantee Marketplaces
Analysis of the Tajin Group operating on Dabai and Xinbi guarantee marketplaces, detailing money laundering, phishing, and OPSEC tactics.
Ransomware Trends in Japan: The Gentlemen, Qilin, and SME Targets
Ransomware attacks in Japan increased by 4.7% in H1 2026, with The Gentlemen and Qilin ransomware groups actively targeting SMEs and manufacturing.
Japan Ransomware Surge: Qilin & The Gentlemen Target SMEs
Japan's ransomware incidents are rising, driven by Qilin's AI-generated attacks and The Gentlemen's stealthy AdaptixC2 use. SMEs are primary targets.
Cisco Talos Newsletter: Frustrating Adversaries and Security Updates
Read the latest Threat Source newsletter by Cisco Talos, featuring adversary frustration tactics and weekly cybersecurity news summaries.
Proactive Ransomware Defense: Leveraging Threat Intelligence
Learn how external threat intelligence enables early detection and disruption of ransomware attacks, moving beyond reactive, post-encryption defense.
Warlock Ransomware Targets Spanish, Portuguese Orgs
Warlock ransomware campaign targets large organizations in Spain and Portugal, exhibiting characteristics of both cybercrime and state-associated APTs.
Operation KillSwitch Dismantles KillSec Ransomware Gang
International law enforcement operation "KillSwitch" dismantled the KillSec ransomware gang, arresting suspects and seizing 110TB of stolen data.
AI Transforms Social Engineering: Phishing & Deepfake Threats
AI enhances social engineering with personalized phishing, fraudulent websites, and synthetic media. Organizations must adapt defenses beyond traditional verification.
Unit 42 Debunks 3 Cybersecurity Myths: Tools, Targets, GRC
Unit 42 experts challenge common cybersecurity misconceptions, highlighting dangers of tool overload, underestimating threats, and misinterpreting GRC.
US Soldier Sentenced to 70 Months for Telecom Extortions
A US Army soldier operating as Kiberphant0m received a 70-month prison sentence for hacking telecommunications firms and extorting victims.
ShinyHunters Arrest and PeopleSoft Zero-Day Exploitation
Dutch police arrest a reformed hacker linked to ShinyHunters, prompting retaliatory attacks involving Oracle PeopleSoft CVE-2026-35273.
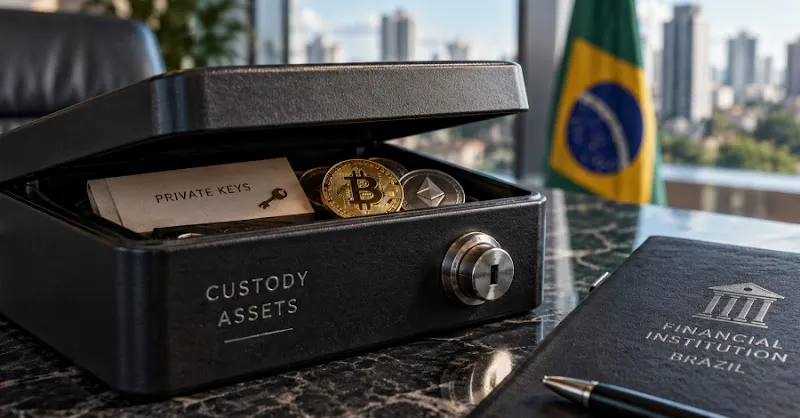
Slim Spider Targets Brazilian Financial Systems and Crypto Assets
Discover how the newly documented threat actor Slim Spider targets Brazilian financial infrastructure and cryptocurrency assets.
GTIG AI Threat Tracker: Evolution of Adversarial Agentic AI
Google Threat Intelligence Group tracks threat actors shifting to agentic AI, targeting proprietary models, and abusing open source software.
Microsoft 365 Vishing Leads to Executive Data Theft, Extortion
A widespread threat cluster, PREY-0058, targets Microsoft 365 executives with vishing, AitM token theft, and data extortion.
Mathspace Breach: Over 1 Million Impacted by Metabase Zero-Day
Mathspace disclosed a data breach affecting over 1 million students, staff, and parents due to a Metabase vulnerability.
Ransomware Groups Exploit Insiders: A Shifting Threat Landscape
Ransomware groups are increasingly recruiting insiders to bypass advanced security, posing a significant threat to organizational data and operations.
39 Methods Compromise Passkey Authentication: Threat Analysis
Discover 39 published methods compromising passkey authentication, focusing on ecosystem flaws, UI manipulation, and enrollment abuse.
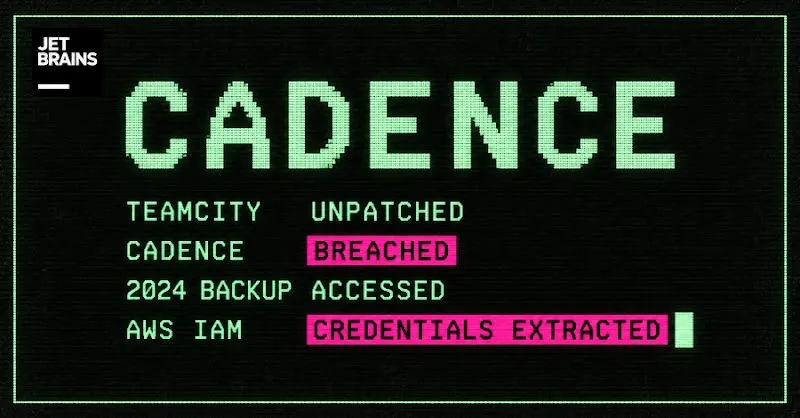
CVE-2026-63077: JetBrains Cadence Breach Exposes Credentials
JetBrains Cadence suffered a data breach via unpatched TeamCity (CVE-2026-63077), exposing AWS credentials, source code, and user data. Immediate action required.
IDScan Sued Over Alleged Breach Impacting 153 Million Drivers
IDScan faces lawsuits after a dark-web service allegedly offered to sell 153 million driver's licenses and millions of other identity documents.
ShinyHunters: Dark Reading on Potential ReliaQuest Breach
Dark Reading editors discuss the latest activities of the ShinyHunters threat group, including inquiries into a potential breach affecting ReliaQuest.
French Hospital Fined €500K for GDPR Data Breach
France's CNIL fined Hôpital privé de la Loire €500,000 after a data breach exposed sensitive medical data of 727,000 patients.