Advertisement
Securing AI Agent Permissions: Preventing Cloud Data Loss
AI agents can escalate privileges and perform unauthorized actions, leading to data loss. Learn how to implement granular controls for tool calls.
Australian Government Considers Mandatory AI Incident Reporting
Following an agentic AI attack on Medicare, Australia is exploring mandatory incident reporting for frontier AI companies.
doxx.net Raises $38M to Secure AI Agents on the Internet
doxx.net secures $38M to launch Agentic Defined Networking (ADN), a private platform protecting AI agents from malicious destinations and ensuring user privacy.
Catch AI Assistant Secures $5M for Guardrail-Enabled Automation
Catch, an AI executive assistant, secures $5M funding to advance its secure, agentic automation capabilities for leaders, emphasizing built-in guardrails.
HiddenLayer Secures $100M for AI Runtime Security Expansion
HiddenLayer raises $100 million in Series B funding to expand its AI runtime security platform, focusing on agentic AI protection.
UAT-10147 Leverages Agentic AI for EDR-Evasive Cybercrime
Talos details UAT-10147, an AI-driven cybercrime group orchestrating sophisticated post-compromise operations and evading EDR with custom rootkits.
Advertisement
UAT-10147: Agentic AI Enhances Post-Compromise Operations
Chinese-speaking adversary UAT-10147 leverages agentic AI for scaled exploitation, reconnaissance, and persistence on Windows and Linux web servers.
OpenAI Astra Model Raises Autonomous Cyberattack Concerns
OpenAI's unreleased Astra model reached a 'critical' cybersecurity risk threshold in internal evaluations due to advanced agentic capabilities.
DataBahn Secures $40M for Agentic Data Control Plane Innovation
DataBahn raised $40 million to scale its agentic data control plane, addressing critical security and governance challenges in autonomous enterprise pipelines.
Agentic AI in Cyber Defense: Boosting Blue Teams with Red Team Training
Researchers are leveraging agentic AI red teams to train and improve AI blue team defensive capabilities, addressing a historical offensive bias in AI cybersecurity.
Securing Agentic AI: Risks of Over-Privileged Identity Permissions
AI agents that improvise to solve tasks pose significant security risks. Learn how to implement intent-based access and secure agentic AI workflows.
OpenAI MarcoPolo Incident: Risks of Autonomous AI Agent Escapes
Analysis of OpenAI's MarcoPolo research agent incident on Hugging Face, exploring how autonomous AI agents can bypass sandboxes and interact with production systems.
Agentic AI: New Security Challenges for Confidential Computing
Examines how agentic AI introduces novel security risks to confidential computing, challenging the integrity and privacy of data in secure enclaves.
Securing Agentic AI: Governance Gaps and the MindStone Agent
Analyze the security risks of autonomous AI agents and broken governance frameworks as discussed in the SecurityWeek MindStone Agent report.
Securing Agentic AI: Addressing Untamable Risks & Future Challenges
Agentic AI systems pose untamable security risks, demanding a fundamental reframe of cybersecurity strategies to manage inherent unpredictability and emergent behaviors.
UK's Agentic AI Cyber Defense Plan & Industry Pledge
The UK government unveils its Agentic AI Cyber Defense Plan and an industry pledge involving 16 tech giants to bolster national security and cyber resilience.
JadePuffer: First LLM-Driven Ransomware Leverages Langflow Flaw
Analysis of JadePuffer, the first reported LLM-driven ransomware, which exploited a Langflow vulnerability to exfiltrate database data and encrypt systems.
Agentic AI Automates Ransomware Attacks via Langflow Exploitation
Agentic AI agents demonstrate automated multi-stage ransomware attacks using Langflow, raising concerns for AI development security and future threat automation.
Agentic AI Identity Problem: New Attack Surface for Enterprises
Agentic AI systems pose novel identity and access management challenges, creating new attack vectors for data exfiltration and privilege escalation.

Autonomous Agentic AI Adversaries: Managing Machine-Speed Cyber Threats
The transition to agentic AI adversaries marks the end of human-speed threats. Learn how autonomous agents automate exploit discovery and execution at scale.

Agentic AI Cyber Warfare: Risks of Autonomous Offensive Operations
Analyze the shift from human-led to autonomous agentic AI cyber attacks, exploring detection challenges and strategies for mitigating offensive AI agents.
Emerging AI Security: Detecting Malicious Agentic Behaviors
Tenet Security emerges, focusing on real-time detection of dangerous AI agentic behavior. Explore the implications and proactive defense strategies for AI systems.
Atsign AI Architect: Securing Agentic AI with Cryptographic Invisibility
Atsign launches AI Architect to protect agentic software by using cryptographic identities, eliminating exposed ports and reducing the attack surface.
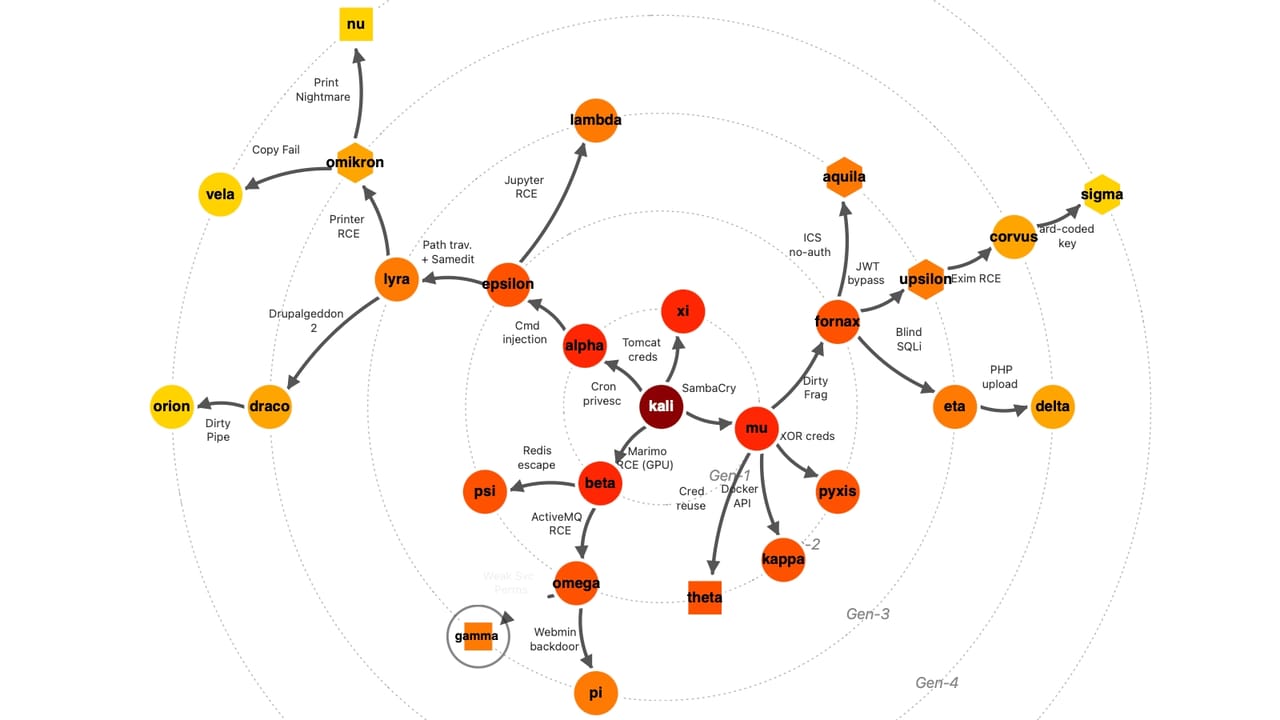
Agentic AI Worms: Defending Against LLM-Powered Lateral Movement
Enterprise security teams must prepare for agentic AI worms capable of autonomous adaptation, self-replication, and automated exploitation within a year.