Advertisement
Linux Backdoors Target Telecom Networks with Regional Spoofing
Linux backdoors targeting South Korea and Taiwan disguise traffic as email security products to evade detection in enterprise environments.
ClingSTUN Backdoor Exploits 24 IoT Flaws for Proxy Network
The ClingSTUN Linux backdoor exploits 24 known vulnerabilities in IoT devices, turning them into proxy nodes and using STUN servers to obscure communications.
ClingSTUN Linux Backdoor Exploits Dozens of Flaws via STUN Protocol
FortiGuard Labs identifies ClingSTUN, a Linux backdoor that abuses the STUN protocol and exploits dozens of flaws for self-propagation.
New Linux Backdoors Mimic Asian Mail Security Products
A trio of newly discovered Linux backdoors are mimicking legitimate Asian mail security products, making detection challenging for defenders.
CloudSyncD Backdoor Targets macOS Users via Fake Zoom Installer
macOS users are targeted by CloudSyncD, a persistent backdoor delivered via fake Zoom installers, gaining root access through social engineering.
SC Self-Healing WordPress Backdoor and wpForo SQLi Exploitation
A sophisticated 'self-healing' WordPress backdoor (SC) utilizes multiple persistence mechanisms, including shared memory.
Advertisement
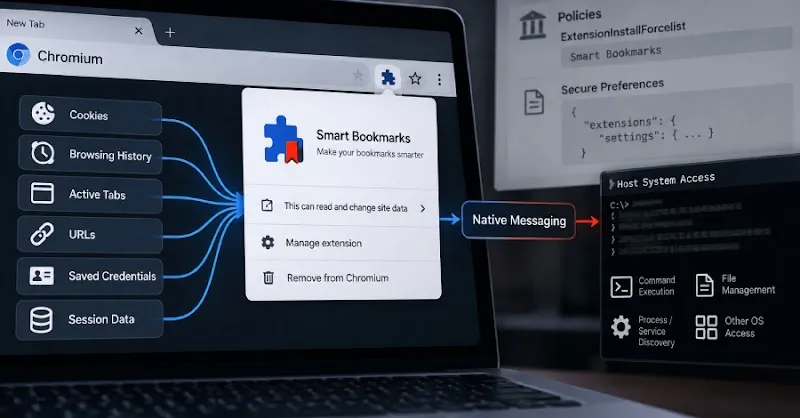
PEEP Backdoor Turns Browsers into OS Command Execution Tools
PEEP toolkit leverages Chrome and Edge as post-compromise backdoors, enabling host command execution, data exfiltration, and session hijacking.
Head Mare Breaches TrueConf, Trojanizes Client Installers
The Head Mare hacktivist group breached TrueConf video conferencing servers to distribute backdoored client installers, compromising user systems.
Critical Backdoors & Supply Chain Attacks: Zbtlink Routers & QuickFox VPN Compromised
Urgent warning: Zbtlink routers ship with unauthenticated root backdoors, while QuickFox VPN delivers FDMTP implant via supply chain compromise.

Suspected Chinese-Speaking Hackers Deploy OctLurk, SilkLurk Backdoors
Ongoing cyberattacks by a suspected Chinese-speaking threat actor target Central Asian governments with OctLurk and SilkLurk backdoors for espionage and data theft.
GigaWiper: Modular Implant Combines Backdoor & Wiper Functions
Analysis of GigaWiper, a modular implant allowing threat actors to combine backdoor and wiper functionality for customizable destructive attacks and maximum impact.
Roundcube Flaw Exploited by China-Linked Group Against Academics
A China-linked threat cluster is actively exploiting a Roundcube webmail vulnerability to steal credentials and deploy backdoors at U.S./Canadian universities.
New 'Leash' Backdoors Target SOHO Routers: China-Linked APT Update
A China-linked APT group has expanded its toolkit with new 'Leash' backdoors (LongLeash, DogLeash, JarLeash), targeting SOHO routers for persistent access and command…

CVE-2026-11405: Tenda Router Firmware Admin Backdoor Exposed
CERT/CC warns of an undocumented admin backdoor, CVE-2026-11405, in Tenda router firmware, enabling full administrative access bypass. Immediate action advised.
China-Linked APT Targets Southeast Asia Critical Systems with New Backdoor
A China-linked APT group has compromised ten organizations, including state-owned entities in Southeast Asia, deploying a new backdoor.

ShapedPlugin Supply Chain Attack: WordPress Pro Plugins Backdoored
Attackers compromised ShapedPlugin's distribution pipeline to inject backdoors into Pro WordPress plugins. Learn how to detect and remediate this supply chain threat.
CryptoBandits Malware: Tor-Abusing Backdoor & Data Theft
CryptoBandits malware functions as a backdoor, leveraging Tor and a SOCKS5 proxy for stealthy data theft and remote code execution capabilities.
Outdated REDCap Servers Targeted by China-linked UNC6508
A majority of internet-accessible REDCap servers remain unpatched, making them prime targets for initial access and backdoor deployment by China-linked UNC6508.
SHub Reaper Stealer Backdoors macOS via Spoofed Apps
SHub Reaper stealer targets macOS, using fake Google, Microsoft, Apple, WeChat, and Miro installers for Apple script-based execution and backdooring.
SHub macOS Infostealer Spoofs Apple Security Updates, Installs Backdoor
A new SHub macOS infostealer variant employs fake Apple security update prompts via AppleScript to install a backdoor, threatening user data and system integrity.

Malicious node-ipc Versions Compromise Developer Secrets via Supply Chain
Three versions of the node-ipc npm package (9.1.6, 9.2.3, 12.0.1) contain stealer/backdoor functionality targeting developer secrets. Urgent update advised.
Stealthy Quasar Linux (QLNX) Malware Targets Developers
New Quasar Linux (QLNX) malware is infecting developers' Linux systems, utilizing rootkit, backdoor, and credential-stealing techniques. Learn to detect and mitigate.
Silver Fox APT: Tax-Themed Phishing Delivers ABCDoor to India, Russia
China-backed Silver Fox APT targets organizations in India and Russia with over 1,600 tax-themed phishing messages to deploy ABCDoor backdoor and ValleyRAT.
WordPress Quick Page/Post Redirect Backdoor: Arbitrary Code Injection
A dormant backdoor in the Quick Page/Post Redirect WordPress plugin allowed arbitrary code injection for five years on over 70,000 sites. Learn mitigation.