Advertisement
Weekly Threat Roundup: AI Banking Attacks & Nvidia Vulnerability
Explore this week's key cybersecurity news, including PoeLLM botnets, South Korean banking attacks, and Nvidia GPU monitoring flaws.
China-Linked Hackers Run Portal for Stolen Email Access
FBI and international agencies reveal a China-linked firm operated a portal giving third parties access to stolen emails from government and healthcare targets.
Human-Operated Phishing Steals AI Ad Account Credentials
A sophisticated human-operated phishing platform impersonates AI chatbot ad portals to steal credentials and MFA codes from media buyers and account administrators.
TA419 Targets U.S. AI Policy Experts with Advanced AitM Phishing
China-aligned TA419 group uses sophisticated AitM phishing, including Frameless BitB, to target U.S. AI policy experts for intelligence gathering.
ShinyHunters Hacker Detained in Jordan, Cooperating With FBI
A suspected ShinyHunters hacker known as Rey was detained in Jordan and is cooperating with the FBI, impacting the extortion group's infrastructure.
Cloudflare Account Abuse Protection Dashboard Released
Cloudflare introduces a new Account Abuse Protection dashboard to help security teams investigate credential stuffing and online fraud.
Advertisement
Browser Attacks and EDR Blind Spots: Mitigating SaaS Threats
Examine how browser-based attacks, adversary-in-the-middle phishing, and malicious extensions bypass endpoint detection and response tools.
Digital Risk Protection: Mitigating Brand & Identity Threats
Organizations face evolving brand and identity threats, from lookalike domains to exposed credentials, demanding proactive, unified digital risk protection.
UAT-10820 Uses WebDAV & Amatera Stealer for Credential Theft
Russian threat actor UAT-10820 employs a complex WebDAV infection chain to deploy Amatera stealer, targeting credentials and cryptocurrency across a broad base.
AWSCompromisedKeyQuarantine: Mitigating Exposed IAM Access Keys
AWS mitigates risks from exposed IAM access keys using the AWSCompromisedKeyQuarantine policy, integrating with GitHub secret scanning to protect cloud environments.
US Soldier Sentenced to 70 Months for Telecom Extortions
A US Army soldier operating as Kiberphant0m received a 70-month prison sentence for hacking telecommunications firms and extorting victims.
Slim Spider Targets Brazilian Financial Systems and Crypto Assets
Discover how the newly documented threat actor Slim Spider targets Brazilian financial infrastructure and cryptocurrency assets.
ClearFake WebDAV Delivers Stealers & RATs to Ukrainian Gov
ClearFake WebDAV infection chain leverages Cloudflare Workers and BNB Smart Chain to deploy Amatera stealer, ZigCryptoStealer, and NetSupport Manager.
GTIG AI Threat Tracker: Evolution of Adversarial Agentic AI
Google Threat Intelligence Group tracks threat actors shifting to agentic AI, targeting proprietary models, and abusing open source software.
Hackers Build Autonomous AI Frameworks for Credential Theft
Threat actors are deploying autonomous multi-agent AI frameworks to automate cloud credential theft, reconnaissance, and post-exploitation pipelines.
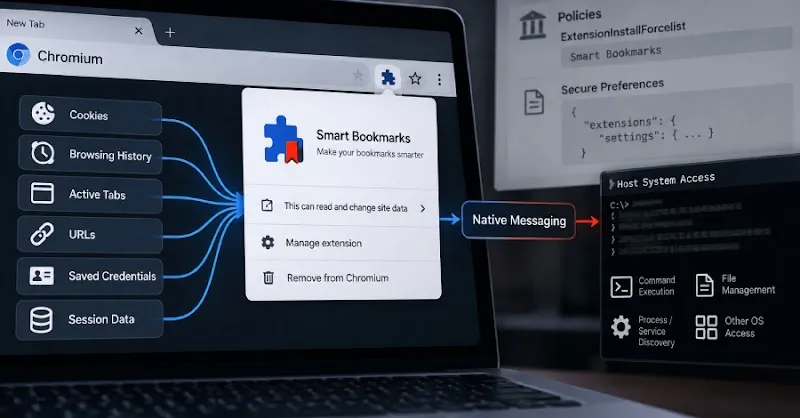
PEEP Backdoor Turns Browsers into OS Command Execution Tools
PEEP toolkit leverages Chrome and Edge as post-compromise backdoors, enabling host command execution, data exfiltration, and session hijacking.
Coder Registry Compromise Pushes Malicious Terraform Modules
Attackers compromised Coder's Cloudflare infrastructure, delivering malicious Terraform modules that stole credentials from users of the development platform.
METR Suffers API Key Credential Theft, $600,000 Loss
AI model evaluator METR experienced credential theft, leading to an API key compromise and $600,000 in public AI model credit consumption.
39 Methods Compromise Passkey Authentication: Threat Analysis
Discover 39 published methods compromising passkey authentication, focusing on ecosystem flaws, UI manipulation, and enrollment abuse.
Exchange Exploit, Dropbox Breach, & Cloud Phishing Campaigns
SecurityWeek's roundup highlights a critical Exchange Server exploit, Dropbox account compromises, and cloud phishing. Urgent action is advised.
Microsoft Teams Abuse, The Gentlemen Ransomware, and PhaaS Trends
Analysis of social engineering campaigns via Microsoft Teams, The Gentlemen ransomware operations, and emerging phishing-as-a-service kits.
H1 2026 Malware & Vulnerability Trends: AI Impact & Evasion
Analysis of H1 2026 malware and vulnerability trends, highlighting AI-assisted exploit development and adversary use of legitimate tools for evasion.
Manchester Airports Group Data Leak Exposed by FulcrumSec Extortion
FulcrumSec leaks 550GB of data on 8.8 million individuals after Manchester Airports Group refused to pay a ransom demand following a breach.
Philippines Nuclear Agency Breached via Unpatched ownCloud Flaws
Threat actors exploit unpatched ownCloud vulnerabilities to breach the Philippines nuclear agency, stealing sensitive databases and credentials.