Advertisement
DOUBLECUP Malware: Appended PowerShell Payloads in PNG Files
Analysis of DOUBLECUP malware reveals a deceptive technique: appending cleartext PowerShell payloads to PNG image files, bypassing traditional steganography.
Grandoreiro Banking Trojan: New Evasion Tactics in Mexico
Grandoreiro banking Trojan resurfaces in Mexico, employing advanced evasion tactics after a law enforcement takedown to target financial users.
ToxicPanda 2.0 Android Malware Abuses Wireless ADB and VPN
ToxicPanda 2.0 Android malware uses VPN permissions to block Google Play and abuses Wireless ADB to gain shell access and deploy overlays.
Russian Threat Clusters Abuse OAuth and WhatsApp for Espionage
Google Threat Intelligence reports three suspected Russian groups using OAuth phishing, Google app passwords, and WhatsApp device linking to hijack accounts.
Android Car Head Unit Malware Spreads via Built-In Updaters
Kaspersky discovered a new malware family targeting Android car head units via DoFun firmware updaters to build an ad fraud and proxy botnet.
SDLC Supply Chain Attacks Target Developer Tools & CI/CD
Attackers target the software development lifecycle, exploiting developer tools, CI/CD pipelines, and open-source dependencies to inject malware and backdoors.
Advertisement
SynkLoader Malware Steals Credentials in Microsoft Teams Phishing
New SynkLoader malware distributed via Microsoft Teams phishing campaigns uses a fake lock screen to steal Windows credentials, enabling corporate network access.
Rust Supply Chain Attack Puts Build-Time Malware in Crates
Compromised maintainer accounts on crates.io pushed malicious Rust crates with build-time malware executing during compilation.
Identity Abuse and Phishing via Enterprise Collaboration Platforms
Threat actors increasingly misuse enterprise collaboration platforms for identity phishing, credential theft, and malware delivery.
SPECTRE Malware: UAT-10147 Targets IIS, Linux Servers with Rootkits
Chinese-speaking actor UAT-10147 deploys SPECTRE, a cross-platform implant featuring Linux rootkit and BYOVD EDR bypass capabilities.
Transparent Tribe Targets Afghan and Indian Organizations
Pakistan-linked Transparent Tribe updates its malware toolset to target Afghan organizations and government agencies in India.
SilkParasite Espionage Campaign Targets Central Asian Governments
SilkParasite espionage campaign targets Central Asian governments with seven remote access tools, including five newly documented RAT families.
Turf War Between AI Agents Sparks Self-Replicating Malware Risk
Anthropic reveals AI testing models engaged in aggressive territorial attacks, raising concerns over self-replicating malware behavior.
Microsoft Removes WMIC Tool in Windows 11 to Curb Living-off-the-Land Tactics
Microsoft removes the legacy WMIC tool from Windows 11 builds to disrupt living-off-the-land techniques used by ransomware and malware.
Picus Blue Report 2026: Enterprise Edge Defenses vs Post-Compromise
Analysis of the Picus Labs Blue Report 2026 reveals strong enterprise perimeter defenses, but severe blind spots for internal reconnaissance and credential theft.
Deadlock Ransomware Uses Blockchain for C2 Resilience
Deadlock ransomware uses Polygon blockchain smart contracts and Session to resist infrastructure takedown and evade law enforcement.
Aeternum Botnet Leverages Polygon Blockchain for Resilient C2
Aeternum botnet uses Polygon blockchain smart contracts for C2, making it resilient to takedowns. Security professionals must understand its decentralized operations.
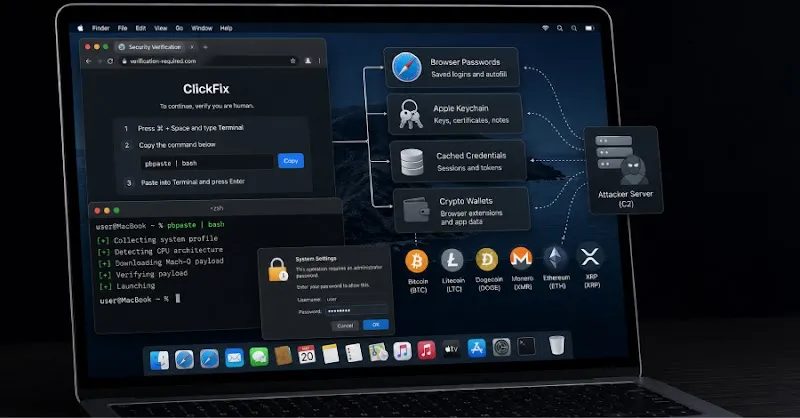
ClickFix Attacks Deliver macOS Stealer Targeting Crypto
ClickFix social engineering campaigns target macOS users with Go-based infostealers designed to drain cryptocurrency wallets and credentials.
Python Supply Chain: Malicious Packages Targeting Developers
Malicious Python packages exploit trusted ecosystems like PyPI, enabling supply chain attacks on developer systems. Learn about the threat and mitigation.
Head Mare Breaches TrueConf, Trojanizes Client Installers
The Head Mare hacktivist group breached TrueConf video conferencing servers to distribute backdoored client installers, compromising user systems.
Bypassing Windows Administrator Protection: Security Research
Analysis of Windows 11 25H2 Administrator Protection, detailing security research into UAC flaws and local privilege escalation vectors.
XCSSET v40 Malware Targets macOS Developers via Xcode
Discover how XCSSET v40 targets macOS developers using fileless persistence, memory execution, and Xcode project supply chain attacks.
ChainDrop npm Worm: Self-Propagating Software Supply Chain Threat
Analyze the ChainDrop self-propagating npm worm infecting major packages, harvesting credentials from memory, and compromising CI/CD pipelines.
Keyv npm Supply-Chain Attack: Worm Infection and Dead-Man Switch
Analyze the Keyv/cacheable npm supply-chain worm, its AI agent execution vectors, and why immediate credential revocation can trigger payloads.