Advertisement
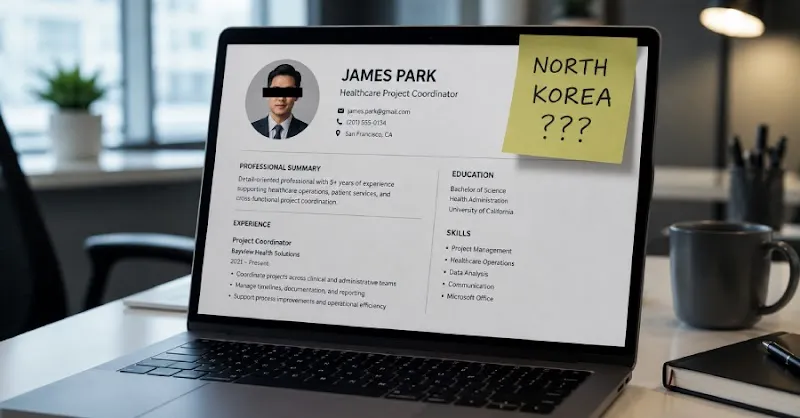
North Korean Job Fraud Expands Beyond IT: New Sectors Targeted
DPRK-linked threat actors are expanding job fraud beyond IT into healthcare, sales, and finance, leveraging AI and fake identities to fund illicit programs.
North Korea's Sapphire Sleet Targets Rust Supply Chain via arrayref Crate
North Korean actor Sapphire Sleet compromised a Rust maintainer's account to publish malicious `arrayref` crate versions, targeting the Rust supply chain.
PurpleDelta: North Korean IT Workers Exploit Remote Hiring
Recorded Future exposes PurpleDelta, North Korean IT workers using sophisticated fraudulent employment, AI, and extensive vetting evasion to fund DPRK military programs.
North Korea Attribution, Data Breaches Impact OnTrac & UK Education
AWS attributes recent hacks to North Korea. OnTrac and the UK Department for Education report significant data breaches, impacting over 600,000 records.

PolinRider: North Korean Hackers Push 108 Malicious Packages
Analysis of the PolinRider campaign where North Korean actors published 108 malicious packages and extensions across npm, Go, and Chrome ecosystems.

ScarCruft Deploys NarwhalRAT via Fake Microsoft Security Alerts
North Korean threat actor ScarCruft (APT37) is deploying NarwhalRAT via spear-phishing emails that mimic official Microsoft Account security notifications.
Advertisement

North Korean APT Targets Developers via Malicious Tooling
North Korean threat cluster Contagious Interview exploits developer recruitment and code review phishing to deliver malware via tainted dev tools.
North Korea Dominates Crypto Heists: 76% of Stolen Funds by 2026
North Korean threat actors are projected to be responsible for 76% of all cryptocurrency stolen by 2026, utilizing sophisticated methods for large-scale heists.
KelpDAO $290 Million Heist Linked to North Korea’s Lazarus Group
KelpDAO suffers a $290 million crypto-heist attributed to the North Korean Lazarus Group, highlighting ongoing threats to DeFi liquid restaking protocols.
Sapphire Sleet's ClickFix: North Korea Targets macOS Users
North Korea-backed Sapphire Sleet is deploying ClickFix malware via fake job offers and phony Zoom updates to steal macOS user credentials and data.

APT37 Social Engineering via Facebook Delivers RokRAT Malware
North Korean threat actor APT37 leverages Facebook friend requests and trust-building to deploy the RokRAT trojan against high-value targets.
North Korean Social Engineering Targets Node.js Maintainers
North Korean threat actors use social engineering and malicious npm packages to target high-profile Node.js maintainers in a sophisticated supply chain campaign.

UNC1069 Social Engineering Leads to Axios npm Supply Chain Compromise
Runtime Rebel details how North Korean threat actor UNC1069 leveraged targeted social engineering against an Axios npm package maintainer, leading to a critical supply…
Axios NPM Supply Chain Attack Bypasses GitHub Actions CI/CD
A sophisticated supply chain attack targeted the Axios NPM package, leveraging a compromised token to bypass GitHub Actions CI/CD and deploy malicious versions.

Axios npm Supply Chain Attack Attributed to North Korea's UNC1069
Google Threat Intelligence attributes a major Axios npm supply chain attack to North Korean group UNC1069, emphasizing risks to developer environments.
UNC1069 Leverages Axios NPM Supply Chain to Deploy WAVESHAPER.V2
North Korea-nexus UNC1069 compromised widely used Axios NPM package (v1.14.1, 0.30.4) by injecting plain-crypto-js to deploy WAVESHAPER.V2 backdoor across multiple OS.

WaterPlum Abuses VS Code Tasks to Deploy StoatWaffle Malware
North Korean threat actor WaterPlum leverages VS Code tasks.json to automate StoatWaffle malware deployment during fraudulent developer recruitment campaigns.
Bitrefill Attributes Cyberattack to North Korean Lazarus Group
Bitrefill identifies North Korean Lazarus Group as the perpetrator of a recent cyberattack, underscoring the persistent threat to crypto-focused businesses.

UNC4899 Exploits AirDrop for Crypto Firm Breach — Analysis
UNC4899 breached a crypto firm using AirDrop to bypass network security. This analysis explores the TTPs of North Korean threat actors in 2025.
North Korean APT Bridges Air Gaps with New Malware Suite
North Korean threat actors utilize malicious LNK files and specialized USB propagation tools to compromise air-gapped networks. Analysis and defense guide.
APT37 Deploys SHROUDEDVUE Malware to Target Air-Gapped Networks
North Korean threat actor APT37 utilizes new malware families like SHROUDEDVUE and WASHSYNC to infiltrate air-gapped systems via removable USB drives.

ScarCruft Ruby Jumper Campaign Targets Air-Gapped Networks
North Korean threat actor ScarCruft (APT37) deploys Ruby Jumper campaign using Zoho WorkDrive for C2 and USB malware to target air-gapped environments.
Fake Recruiters Deploy Malware via Malicious Coding Challenges
North Korean threat actors are targeting software developers with fake job offers and malicious coding tests to deploy malware on developer workstations.
Next.js Supply Chain Attacks: North Korean Actors Target Developers
North Korean state-sponsored actors leverage malicious Next.js repositories and fake job interviews to compromise developers' systems for persistent access and espionage.