Advertisement
Russian Threat Clusters Abuse OAuth and WhatsApp for Espionage
Google Threat Intelligence reports three suspected Russian groups using OAuth phishing, Google app passwords, and WhatsApp device linking to hijack accounts.
iAuthFlow V2 Phishing Toolkit Leverages Passkeys for Persistence
Discover how the iAuthFlow V2 phishing toolkit registers malicious passkeys to maintain persistent account access despite password resets.
SynkLoader Malware Steals Credentials in Microsoft Teams Phishing
New SynkLoader malware distributed via Microsoft Teams phishing campaigns uses a fake lock screen to steal Windows credentials, enabling corporate network access.
Identity Abuse and Phishing via Enterprise Collaboration Platforms
Threat actors increasingly misuse enterprise collaboration platforms for identity phishing, credential theft, and malware delivery.
Russian Threat Clusters Target Academia and Government via Auth Abuse
Google Threat Intelligence Group tracks three Russian cyber espionage clusters abusing legitimate authentication flows and app passwords.
Crime Script Analysis: Mapping Threat Workflows and AI Risks
Discover how crime script analysis translates complex cyber attacks into narratives, highlighting AI threats in business email compromise.
Advertisement
Mitigating Large-Scale Credential Attacks and Password Spraying
Analysis of large-scale password spraying and credential theft campaigns targeting enterprise identity perimeters, edge devices, and cloud tenants.
Threat Actor Claims 3.6 Million Azure Account Records Stolen
A threat actor named TheHatman is selling 3.6 million employee records allegedly stolen from major corporate Azure tenants using compromised credentials.
Public Wi-Fi DNS Hijacking: Credential Theft Risk
Criminals are actively manipulating public Wi-Fi DNS settings to redirect users to fake login pages, stealing sensitive credentials. Learn how to protect yourself.
SafePal Data Breach Exposes 39,798 Customer Order Details
SafePal confirms a data breach impacting 39,798 customers, exposing names, emails, and shipping info. Stolen data is for sale, increasing phishing risks.
New JWR Phishing Framework Bypasses MFA with Live Monitoring
JWR, a new real-time phishing framework, uses WebSockets to bypass MFA and steal sensitive data via SMS lures, posing a critical threat.
Ukraine Dismantles 94 Fraudulent Call Centers, Seizing Millions
Ukraine, in collaboration with German police, dismantled 94 fraudulent call centers, seizing millions in assets. This disrupts investment and bank account phishing scams.
JWR Phishing Framework: Real-time Data Theft via PhaaS
The JWR phishing framework, a variant of The Outsider PhaaS, harvests payment data, PII, and 2FA codes in real-time via operator-controlled sessions.
Webmail CSS Injection: Hidden Data Exfiltration Threats
Security researchers warn that Cascading Style Sheets can exfiltrate sensitive data from webmail inboxes if vendors fail to sanitize styles.
Zero-Click AI Browser Hacking Threatens Claude and ChatGPT Atlas
Zenity details zero-click indirect prompt injection vulnerabilities affecting OpenAI ChatGPT Atlas and Claude in Chrome via malicious web content.
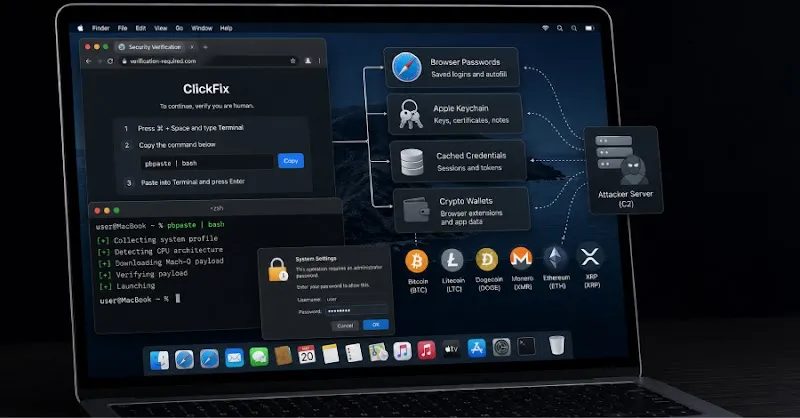
ClickFix Attacks Deliver macOS Stealer Targeting Crypto
ClickFix social engineering campaigns target macOS users with Go-based infostealers designed to drain cryptocurrency wallets and credentials.
CVE-2025-66376: APT28 Exploits Zimbra Zero-Click for Espionage
Russian state-sponsored actors exploit a zero-click Zimbra vulnerability (CVE-2025-66376) to exfiltrate sensitive webmail data from targeted organizations.
Q2 2026 IR Trends: Phishing, MFA Bypass, RMM Tool Abuse
Talos Q2 2026 incident response data shows rising phishing and MFA bypass, with new actors like UAT-11764 and Sinobi ransomware leveraging RMM tools.
UNC6671 Rebrands: Multi-Brand Vishing and Cloud Extortion
Google Threat Intelligence Group tracks UNC6671 shifting through Redact, Pink, Helix, and Falcon extortion brands while targeting cloud environments.
Talos Q2 2026 Report: Phishing and Living-off-the-Land Trends
Cisco Talos Q2 2026 report reveals spikes in MFA-bypassing phishing and malicious use of remote management tools.
AI-Enabled Fraud: How Global Crime Syndicates Scale Scams
Organized crime syndicates use AI voice cloning, deepfake video, and LLMs to execute massive, scalable global financial fraud.
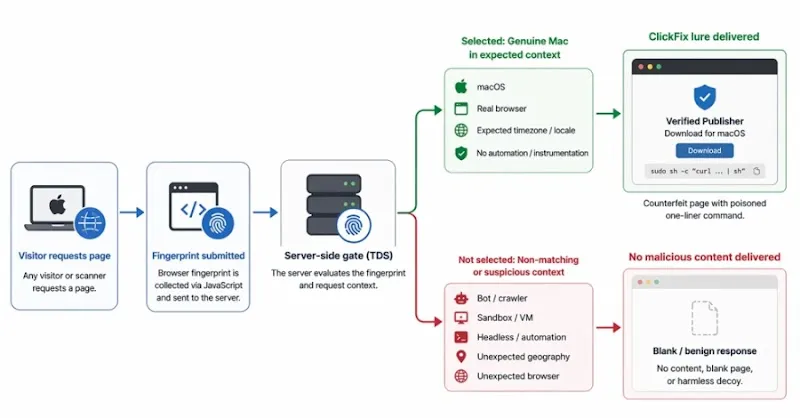
ClickFix Campaign Uses Server-Side Fingerprinting to Hide macOS Malware
Over 250 ClickFix domains utilize server-side browser fingerprinting to evade security sandboxes and distribute macOS infostealers like AMOS.
Smoke#Screen RMM Takeover Campaign Targets Enterprise Networks
Discover how the Smoke#Screen phishing campaign uses rotating payloads and ScreenConnect to achieve persistent remote network access.
Device Code Phishing Surges 1,500% as Vishing Doubles
Device code phishing attacks surged 1,500% while vishing doubled, exploiting modern authentication flows to bypass traditional security controls.