Advertisement
Multi-Vendor Patches: Adobe, Apple, Foxit, Microsoft Vulnerabilities
Cisco Talos discloses patched privilege escalation, RCE, and information disclosure vulnerabilities across Adobe, Apple, Foxit, and Microsoft products.
CVE-2026-96940: Exchange Server Auth Flaw Exposes Mailboxes
Microsoft addresses a high-severity flaw, CVE-2026-96940, in on-premises Exchange Server allowing authenticated attackers to read mailboxes.
CVE-2026-102490: Zammad Privilege Escalation Exploit in Wild
CVE-2026-102490 allows local Zammad users to escalate privileges to root. CISA confirms active exploitation; patch immediately.
Microsoft Patch Tuesday: Zero-Days & Critical RCEs Addressed
Microsoft's record-breaking Patch Tuesday fixes 974 vulnerabilities, including actively exploited zero-days and critical RCEs in Windows.
CVE-2026-76504: Cisco Catalyst SD-WAN Manager Admin Access
CISA confirms active exploitation of CVE-2026-76504, a hex encoding vulnerability allowing unauthenticated remote admin access to Cisco Catalyst SD-WAN Manager.
CVE-2026-66804: Windows Dangling COM Object Privilege Escalation
Microsoft fixed CVE-2026-66804, a privilege escalation bug in Windows, due to a dangling COM object registration.
Advertisement
CVE-2026-81963: Windows Update Stack Privilege Escalation
CISA adds CVE-2026-81963 to the KEV catalog after confirming active exploitation of a Windows Update Stack privilege escalation flaw.
Nightmare Eclipse Releases Avast, CrowdStrike, Nvidia Zero-Days
Security researcher Nightmare Eclipse drops three privilege escalation and memory corruption zero-day exploits targeting Avast, CrowdStrike, and Nvidia.
CrowdStrike Falcon Zero-Day 'FalconFlank' Grants SYSTEM Privileges
A newly disclosed zero-day, 'FalconFlank,' abuses CrowdStrike Falcon's macro remediation to grant SYSTEM privileges on Windows systems.
CVE-2026-6471: PostgreSQL Takeover via Logical Decoding Flaw
CVE-2026-6471, a 12-year-old PostgreSQL vulnerability, allows attackers with low replication privileges to achieve RCE and full database server takeover.
CVE-2026-84115: Cleo Harmony Auth Bypass Exploit Published
An exploit is published for CVE-2026-84115, an authentication bypass in Cleo Harmony allowing remote privilege escalation. Immediate patching to v5.8.1.11 is urged.
CVE-2026-53362: Linux Kernel IPv6 Privilege Escalation
CISA adds CVE-2026-53362 to KEV, confirming active exploitation of a Linux Kernel privilege escalation vulnerability via IPv6. Patch now.
Nightmare Eclipse Releases HardBreacher Kaspersky Exploit
Security researcher Nightmare Eclipse releases HardBreacher, a privilege escalation proof-of-concept targeting Kaspersky Endpoint Security.
Securing Windows Named Pipes: Mitigating Local Privilege Escalation
Unsecured Windows named pipes pose significant local privilege escalation risks. Learn to secure IPC by verifying identity and validating input.
Chrome, Firefox, Thunderbird Updates Patch Dozens of High-Severity Flaws
Google and Mozilla release urgent updates for Chrome 151, Firefox 154, and Thunderbird 154, addressing critical and high-severity vulnerabilities including RCE.
CVE-2026-71362: Adobe Commerce Account Takeover — Patch Now
Hackers are immediately exploiting CVE-2026-71362, a critical authorization flaw in Adobe Commerce, to take over customer accounts. Patch urgently.
ShieldBreak: Windows Zero-Day EoP via Microsoft Defender
Security researcher Nightmare Eclipse released 'ShieldBreak,' a Windows zero-day exploit enabling privilege escalation via Microsoft Defender.
CVE-2026-68820: Windows afd.sys Privilege Escalation Exploited
Microsoft addresses 398 vulnerabilities, including an actively exploited privilege escalation flaw in Windows' afd.sys component.
Bypassing Windows Administrator Protection: Security Research
Analysis of Windows 11 25H2 Administrator Protection, detailing security research into UAC flaws and local privilege escalation vectors.
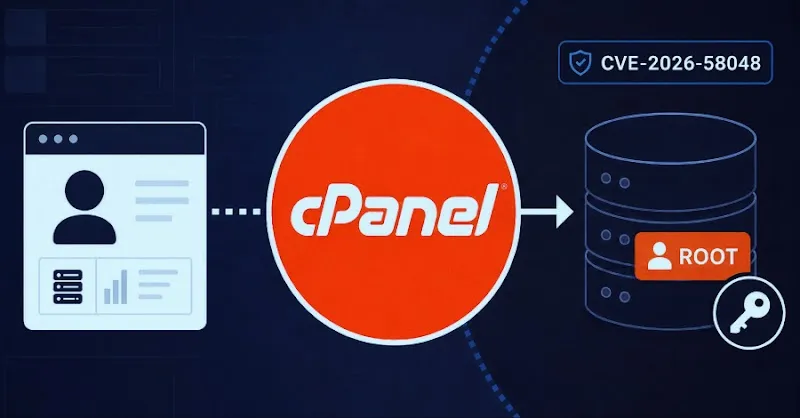
CVE-2026-58048: cPanel & WHM Critical SQL Privilege Escalation
A critical flaw in cPanel & WHM (CVE-2026-58048) allows authenticated users to execute SQL as database root, potentially leading to OS-level compromise.
CVE-2024-49019: Certighost AD CS Privilege Escalation Explained
Analysis of CVE-2024-49019, the Certighost flaw in Microsoft AD CS. Learn how misconfigured certificate templates allow full Active Directory compromise.

CVE-2026-53264: Linux Traffic-Control Bug Escalates to Root Access
A use-after-free race condition in the Linux kernel traffic-control subsystem, CVE-2026-53264, allows local privilege escalation to root on CentOS Stream 9.
Confused Deputy Flaws in Google Cloud & Azure: Admin Bypass
Analysis of 'Confused Deputy' vulnerabilities across Google Cloud and Microsoft Azure, enabling administrative privilege escalation and access control bypass.
Certighost PoC Exploit: Hijacking Windows Active Directory Domains
A new proof-of-concept exploit for Certighost, targeting Windows Active Directory Certificate Services, enables authenticated attackers to compromise Windows domains.