Advertisement
FBI Arrests Ransomware Negotiator Linked to ShinyHunters
FBI agents arrested a Canadian ransomware negotiation executive in Pennsylvania over alleged ties to the ShinyHunters hacking group.
Weekly Threat Roundup: AI Banking Attacks & Nvidia Vulnerability
Explore this week's key cybersecurity news, including PoeLLM botnets, South Korean banking attacks, and Nvidia GPU monitoring flaws.
ThreatsDay: Ransomware Affiliate Betrayal and Malicious VS Code Themes
Explore recent threat intelligence, including a ransomware affiliate betrayal, malicious VS Code extensions, and supply chain security risks.
Ransomware Disrupts Japan's IDCF Cloud, Affecting Gov't Clients
IDC Frontier's IDCF Cloud suffered a ransomware attack impacting its East Japan Region 1, disrupting services for 495 companies and local governments.
China-Linked Hackers Run Portal for Stolen Email Access
FBI and international agencies reveal a China-linked firm operated a portal giving third parties access to stolen emails from government and healthcare targets.
Qilin Ransomware Suspect Extradited, Group Exploits Check Point VPN
A Qilin ransomware group member was extradited to Germany, highlighting the prolific RaaS operation's global reach and exploitation of critical vulnerabilities.
Advertisement
MonsterCloud CEO Charged in Secret Ransomware Payment Scheme
MonsterCloud CEO Zohar Pinhasi was indicted for allegedly defrauding ransomware victims by secretly paying cybercriminals for decryptor keys.
ShinyHunters Extorted Boeing Spin-off Prior to Arrests
Details on the arrest of suspected ShinyHunters leader 'Rey' in Jordan following extortion attempts against a Boeing spin-off.
Ransomware Targets Backups: Evolving Destruction Tactics
Ransomware groups increasingly target backup infrastructure to hinder recovery. Learn about ALPHV/BlackCat and BlackMatter tactics and critical defenses.
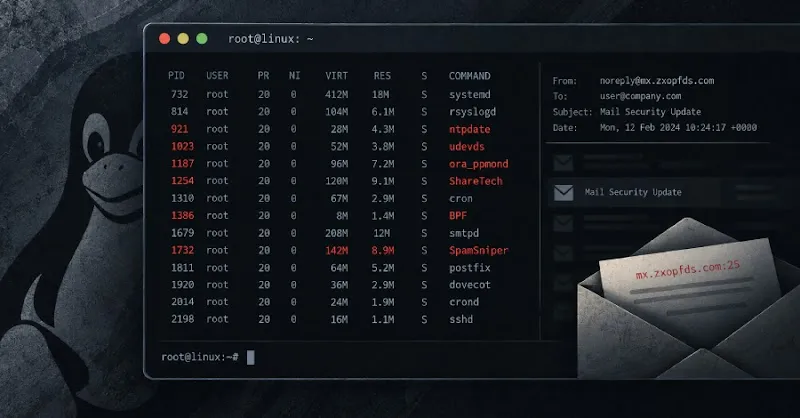
Linux Backdoors Target Telecom Networks with Regional Spoofing
Linux backdoors targeting South Korea and Taiwan disguise traffic as email security products to evade detection in enterprise environments.
Blinder Tunnel Campaign Targets Iraqi Critical Infrastructure
Iranian state-aligned threat actor CL-STA-1178 targets Iraqi critical infrastructure using ShelbyLoader V2 and GitHub API for command-and-control.
South Africa ATC Cyberattack: Ransomware Toolkit on Operational Network
South Africa's air traffic control systems have been targeted by a cyberattack, with a ransomware toolkit found on an operational network.
Dell Container Storage Modules Flaws Give Attackers Admin Privileges
Dell patches multiple maximum severity vulnerabilities in Container Storage Modules impacting enterprise storage and Kubernetes environments.
ShinyHunters Hacker Detained in Jordan, Cooperating With FBI
A suspected ShinyHunters hacker known as Rey was detained in Jordan and is cooperating with the FBI, impacting the extortion group's infrastructure.
Warlock Ransomware Exploits SharePoint in Critical Infrastructure Attacks
Warlock ransomware targets water and telecom sectors using SharePoint zero-days and BYOVD techniques to disable endpoint protection.
Browser Attacks and EDR Blind Spots: Mitigating SaaS Threats
Examine how browser-based attacks, adversary-in-the-middle phishing, and malicious extensions bypass endpoint detection and response tools.
Cisco FMC RCE via CVE-2026-20079: Patch Now
Active exploitation of critical Cisco Secure Firewall Management Center vulnerabilities (CVE-2026-20079, CVE-2026-20316) by state-sponsored and crimeware actors.
KillSec Ransomware Mastermind Arrested: 16-Year-Old Suspect
International law enforcement disrupts the KillSec ransomware operation, arresting an alleged 16-year-old mastermind behind attacks on 500 victims.
ThreatsDay: AI Zero-Day Chains, ATM Jackpotting, and Cache Key Injection
Analysis of recent threat intelligence covering AI-powered zero-day chains, Tren de Aragua ATM jackpotting, and emerging web cache injection techniques.
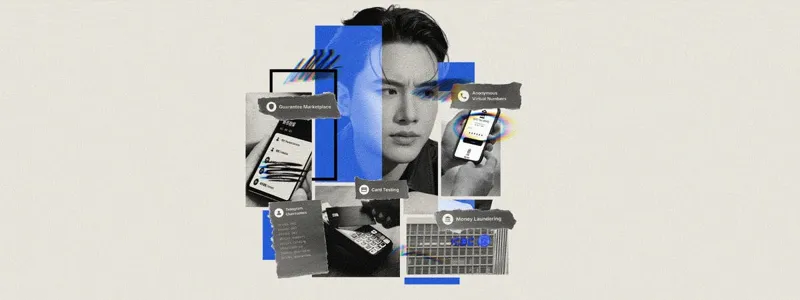
Tajin Group and Chinese Telegram Guarantee Marketplaces
Analysis of the Tajin Group operating on Dabai and Xinbi guarantee marketplaces, detailing money laundering, phishing, and OPSEC tactics.
Ransomware Trends in Japan: The Gentlemen, Qilin, and SME Targets
Ransomware attacks in Japan increased by 4.7% in H1 2026, with The Gentlemen and Qilin ransomware groups actively targeting SMEs and manufacturing.
Japan Ransomware Surge: Qilin & The Gentlemen Target SMEs
Japan's ransomware incidents are rising, driven by Qilin's AI-generated attacks and The Gentlemen's stealthy AdaptixC2 use. SMEs are primary targets.
Cisco Talos Newsletter: Frustrating Adversaries and Security Updates
Read the latest Threat Source newsletter by Cisco Talos, featuring adversary frustration tactics and weekly cybersecurity news summaries.
Proactive Ransomware Defense: Leveraging Threat Intelligence
Learn how external threat intelligence enables early detection and disruption of ransomware attacks, moving beyond reactive, post-encryption defense.