Coverage
Vulnerabilities
1245 articles on vulnerability disclosures and exploits
Advertisement
Apple iOS CVE-2023-41993: Patching Exploited Spyware Vulnerabilities
CISA warns of three Apple iOS vulnerabilities, including CVE-2023-41993, exploited in mercenary spyware and cryptocurrency theft attacks. Patch immediately.
Iranian APT Exploits Edge Vulnerabilities in US Infrastructure
Iranian state-sponsored actors breached US airports and banks by exploiting edge device vulnerabilities, likely serving as initial access brokers for ransomware.

Hikvision and Rockwell Automation CVEs: CISA KEV Mitigation Guide
CISA adds Hikvision CVE-2017-7921 and Rockwell Automation flaws to the KEV catalog. Learn how to detect and mitigate these critical CVSS 9.8 vulnerabilities.
CVE-2024-28182: Python Cryptography RSA DoS Mitigation Guide
Technical deep dive into CVE-2024-28182, a denial-of-service vulnerability in the Python cryptography library. Learn how to detect and patch RSA-based DoS.
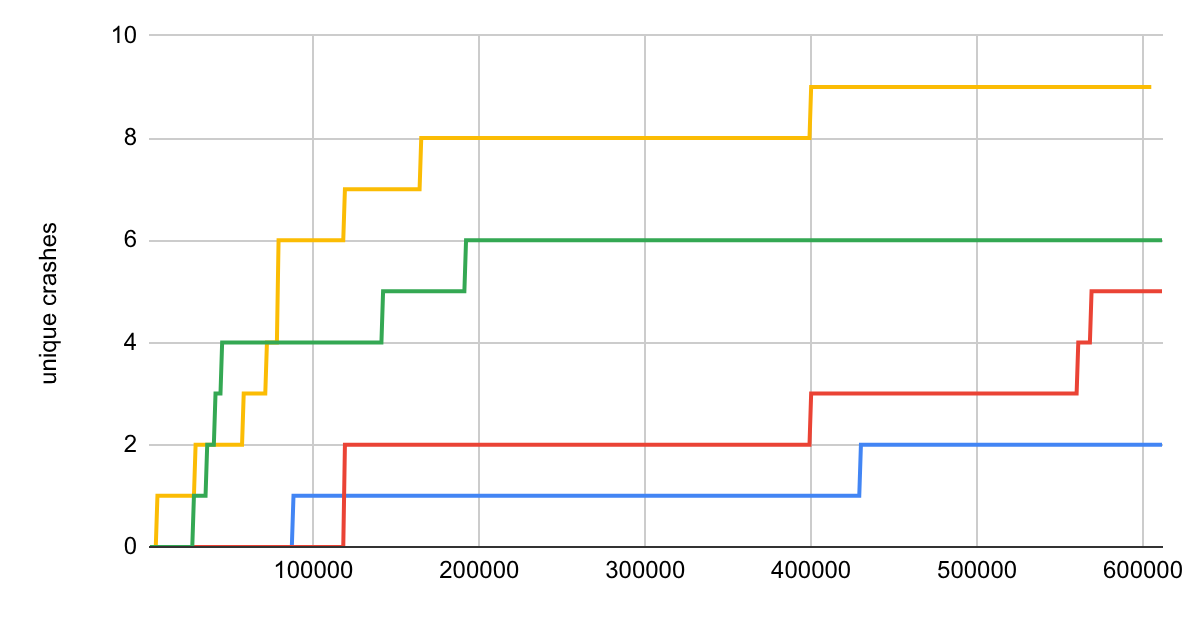
Optimizing Mutational Grammar Fuzzing for Enhanced Vulnerability Discovery
Explore the effectiveness and inherent flaws of mutational grammar fuzzing, a key technique for vulnerability discovery, and a method to improve its efficacy.
CISA KEV Update: Five Actively Exploited CVEs in Apple, Hikvision, Rockwell
CISA adds five actively exploited vulnerabilities, including Apple iOS/iPadOS use-after-free and Hikvision improper authentication, to its KEV Catalog.
CVE-2026-3094: Delta CNCSoft-G2 Out-of-bounds Write RCE
Delta Electronics CNCSoft-G2 is vulnerable to an out-of-bounds write (CVE-2026-3094) allowing remote code execution. Update to V2.1.0.39.
WordPress User Registration & Membership Plugin: Admin Account Exploit
Critical vulnerability in WordPress User Registration & Membership plugin actively exploited to create unauthorized admin accounts.

CVE-2026-20122: Cisco Catalyst SD-WAN Manager Exploited in the Wild
Cisco confirms active exploitation of CVE-2026-20122 in Catalyst SD-WAN Manager, allowing authenticated attackers to perform arbitrary file overwrites.
2025 Zero-Day Exploitation Review: Enterprise & OS Targets Dominate
GTIG's 2025 zero-day review reveals 90 in-the-wild exploits, with a record 48% targeting enterprise tech and a surge in OS vulnerabilities. Includes actor TTPs.
Google Forecasts 90 Enterprise Zero-Day Exploits in 2025
Google predicts half of the 90 exploited zero-day vulnerabilities in 2025 will target enterprises. Understand attribution and proactive defense strategies.
Google Reports 90 Zero-Day Exploits in 2025: Enterprise Focus
Google Threat Intelligence Group tracked 90 zero-day vulnerabilities actively exploited throughout 2025, with nearly half targeting enterprise software and appliances.
Microsoft Outlook CVE-2025-21418: Mitigating NTLM Relay Attacks
Analysis of CVE-2025-21418 in Microsoft Outlook. Learn how attackers bypass security features to leak NTLM hashes and the steps needed for mitigation.
Reclaim Security Secures $20M to Automate Vulnerability Remediation
Reclaim Security raises $20 million to solve the remediation gap, focusing on automating fixes and reducing mean time to remediate for enterprise SOC teams.
Cisco Catalyst SD-WAN Manager Exploitation: Patch CVE-2024-20437 Now
Cisco confirms active exploitation of two high-severity flaws in Catalyst SD-WAN Manager, involving hardcoded credentials and authentication bypass.
Cisco Catalyst SD-WAN Manager CVE-2023-20252 — Mitigation Guide
Cisco warns of active exploitation targeting Catalyst SD-WAN Manager vulnerabilities CVE-2023-20252 and CVE-2023-20253. Immediate patching is required.
VMware Aria Operations Command Injection Exploitation: Cloud Risk
A critical command injection vulnerability in VMware Aria Operations is actively exploited, granting attackers broad access to cloud environments.
Mail2Shell Zero-Click RCE Threatens FreeScout Servers
A critical Mail2Shell zero-click vulnerability in FreeScout helpdesk allows unauthenticated remote code execution, granting full server control.
Coruna iOS Exploit Kit: Spyware-Grade Threat Targets Crypto
The sophisticated Coruna iOS exploit kit, leveraging 23 undocumented vulnerabilities, is now deployed in targeted espionage and crypto theft attacks.
Cisco Secure FMC Root Access & DoS Flaws Patched: Update Now
Cisco addresses two maximum-severity vulnerabilities in Secure Firewall Management Center (FMC) allowing unauthenticated root access and denial of service.

Coruna iOS Exploit Kit Targets iOS 13-17.2.1 with 23 Exploits
Google's GTIG identified Coruna (CryptoWaters), a powerful iOS exploit kit leveraging 23 exploits across 5 chains to target iOS 13.0-17.2.1. Update immediately.
CVE-2025-22719: VMware Aria Operations RCE Exploited in the Wild
CVE-2025-22719 is a critical remote code execution vulnerability in VMware Aria Operations for Networks currently being exploited by unauthenticated attackers.

VMware Aria Operations CVE-2026-22719 Exploited - Mitigation Guide
CISA adds CVE-2026-22719, a VMware Aria Operations command injection flaw, to the KEV catalog following active exploitation. Secure your systems now.
CVE-2025-0282: Ivanti Connect Secure Heap Overflow — Mitigation Guide
Technical analysis of the Ivanti Connect Secure heap overflow (CVE-2025-0282) allowing unauthenticated RCE. Includes detection steps and patch guidance.