All Articles
Security Intelligence
3551 articles · Updated every 8 hours
Advertisement
TSN Protocols Vulnerabilities Threaten OT Security
New research reveals how unprotected Time-Sensitive Networking protocols in industrial systems could allow attackers to disrupt physical processes.
North Korea's Sapphire Sleet Targets Rust Supply Chain via arrayref Crate
North Korean actor Sapphire Sleet compromised a Rust maintainer's account to publish malicious `arrayref` crate versions, targeting the Rust supply chain.
ToxicPanda 2.0 Android Malware Abuses Wireless ADB and VPN
ToxicPanda 2.0 Android malware uses VPN permissions to block Google Play and abuses Wireless ADB to gain shell access and deploy overlays.
Russian Threat Clusters Abuse OAuth and WhatsApp for Espionage
Google Threat Intelligence reports three suspected Russian groups using OAuth phishing, Google app passwords, and WhatsApp device linking to hijack accounts.
Cybercrime Policing Roadblocks: Funding & Training Gaps
Law enforcement faces significant hurdles in combating cybercrime, primarily due to insufficient funding for training and a lack of strategic focus.
Critical Type Confusion in isolated-vm Leads to Host RCE
A critical type confusion vulnerability in the Node.js isolated-vm library allows remote code execution on the host system via V8 Isolates.
Advertisement
Microsoft Entra ID RCE Flaw CVE-2026-69836 Fully Mitigated
Microsoft has fully mitigated a critical remote code execution flaw, CVE-2026-69836, in Entra ID (formerly Azure AD). No customer action is required.
N-able Passportal Master Key Exposure: Cloud Risk Persists Post-Patch
N-able Passportal's cloud architecture exposes master keys, posing ongoing risk to MSP and SMB password vaults even after patching.
iAuthFlow V2 Phishing Toolkit Leverages Passkeys for Persistence
Discover how the iAuthFlow V2 phishing toolkit registers malicious passkeys to maintain persistent account access despite password resets.
Securing Windows Named Pipes: Mitigating Local Privilege Escalation
Unsecured Windows named pipes pose significant local privilege escalation risks. Learn to secure IPC by verifying identity and validating input.
Cisco Patches Nine Crosswork and Secure Workload Flaws
Cisco patches nine vulnerabilities in Crosswork and Secure Workload platforms, with five flaws scoring the maximum CVSS 10.0 severity rating.
Aviation Cybersecurity: Understanding Wi-Fi Disruption Risks
An analysis of aviation Wi-Fi security concerns following a reported Delta flight disruption, examining potential risks and mitigation strategies.
Banking Trojans Manic, Grandoreiro, ToxicPanda 2.0 Active
New and updated banking trojans Manic, Grandoreiro, and ToxicPanda 2.0 are actively targeting financial users globally, stealing credentials and data.
Android Car Head Units Infected by MoYu Proxy Botnet Malware
A supply-chain attack by MoYu Group uses a legitimate update app to infect Android car head units, forming a proxy botnet for ad fraud.
Android Car Head Unit Malware Spreads via Built-In Updaters
Kaspersky discovered a new malware family targeting Android car head units via DoFun firmware updaters to build an ad fraud and proxy botnet.
Encrypted Prompts Bypass AI Safety Guardrails in Grok and Gemini
Researchers discover cryptographic context injection, a novel technique bypassing AI safety filters in xAI Grok and Google Gemini using encryption.
Digital Identities: Compartmentalization for Online Privacy
Explore the systemic erosion of online privacy by surveillance capitalism and data brokers. Learn how digital identity compartmentalization can protect user data.
Weaponizing Defender's BTR.sys to Disable Security Software
Attackers can weaponize a legitimate Microsoft Defender driver to delete security software at boot, impacting Windows 7-11.
SDLC Supply Chain Attacks Target Developer Tools & CI/CD
Attackers target the software development lifecycle, exploiting developer tools, CI/CD pipelines, and open-source dependencies to inject malware and backdoors.
AI Models Generate Viable Synthetic Bacteriophage Genomes
Artificial intelligence models successfully generate viable synthetic bacteriophage genomes, raising dual-use safety concerns.
Friday Squid Blogging: Neon Flying Squid
Researchers capture the first photographs of neon flying squid gliding in formation above the Pacific Ocean using jet propulsion.
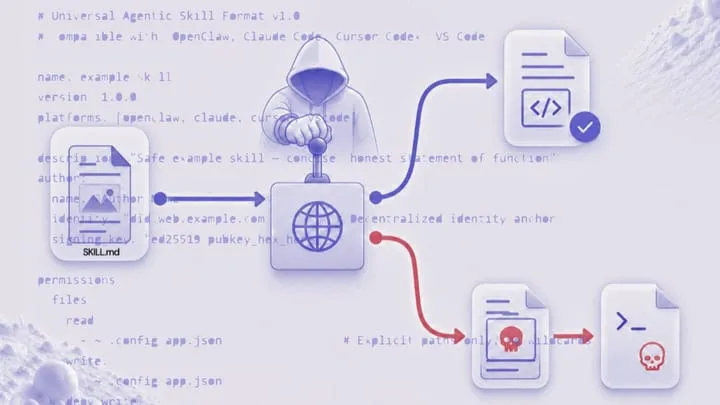
OWASP Releases Top 10 Security List and Universal Skill Format for AI
OWASP debuts a top 10 security list and Universal Skill Format to secure AI add-ons, addressing modern artificial intelligence risks.
Nakasone Group: Expert Cyber & Geopolitical Advisory Launches
Former NSA Director Paul Nakasone launches The Nakasone Group, providing elite cybersecurity, geopolitical, and personal security advisory to high-profile clients.
SynkLoader Malware Steals Credentials in Microsoft Teams Phishing
New SynkLoader malware distributed via Microsoft Teams phishing campaigns uses a fake lock screen to steal Windows credentials, enabling corporate network access.