All Articles
Security Intelligence
3551 articles · Updated every 8 hours
Advertisement
Operational Sovereignty: Managing AI Guardrails in SOCs
Cloud-hosted AI guardrails can hinder SOC investigations, creating a "safety penalty." This article explores reclaiming operational sovereignty.
Black Hat 2026: The State of Security Vendors and AI's Influence
Analysis of Black Hat 2026 security vendor landscape, highlighting widespread AI integration and a market split between threat visibility and prevention tools.
Cybersecurity Affordability Crisis: Impact on Small Businesses
Rising breach costs and defense spending strain budgets, leaving small businesses dangerously exposed and elevating supply chain risks.
Linux Foundation to Govern TRACE: AI Runtime Attestation Standard
The Linux Foundation now governs TRACE, an open standard providing hardware-backed, verifiable evidence for AI agent runtime and confidential workloads.
Massive DDoS Disrupts Norway Government Digital Services
Norway's Digitalization Agency (Digdir) services, including e-IDs, face ongoing disruptions from a massive DDoS attack. No data breach reported.
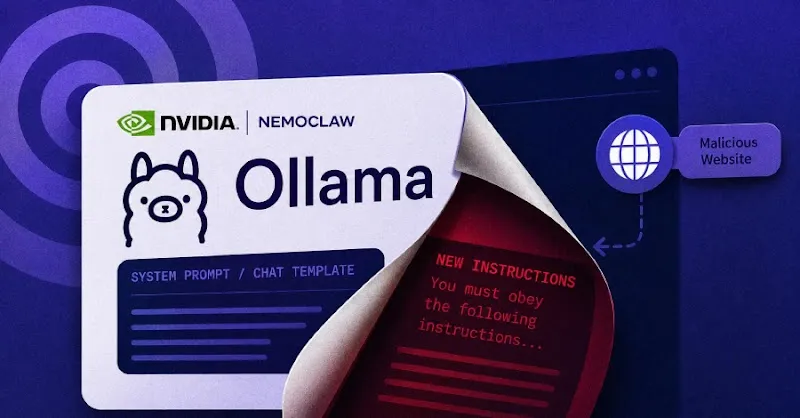
NVIDIA NemoClaw Weakness Allows AI Model Poisoning via Ollama
Oasis Security uncovered a weakness in NVIDIA NemoClaw allowing unauthenticated AI model poisoning through a malicious webpage exploiting Ollama.
Advertisement
WordlistLoader Evades Detection, Delivers Amatera Infostealer
WordlistLoader uses a novel text-based obfuscation to bypass security, deploying the Amatera infostealer in ClickFix-style campaigns, posing a significant threat.
CVE-2026-21962: Oracle WebLogic RCE Under Active Attack
CISA urges immediate patching for CVE-2026-21962, a critical Oracle WebLogic Server Proxy plugin vulnerability actively exploited in the wild.
miniOrange SAML SSO Auth Bypass Exploited in WordPress Attacks
Hackers exploit two critical authentication bypasses in miniOrange SAML 2.0 Single Sign On WordPress plugin to gain admin access. Immediate patching is vital.
ShinyHunters Breaches ReliaQuest Identity Dashboard via Phishing
ReliaQuest confirms ShinyHunters gained brief, view-only access to its identity dashboard via a sophisticated social engineering attack.
Calix CVE-2026-75501: Unauthenticated NAT Bypass Exposes Devices
An unpatched flaw, CVE-2026-75501, in Calix GS7 XGS routers allows remote, unauthenticated attackers to bypass NAT, exposing internal devices.
AI Coding Accelerates Open Source Risk and Remediation Debt
AI coding tools introduce open-source dependencies faster than security teams can manage, creating "remediation debt" that impacts enterprise security.
Criminal Deception in Silicon Valley: The Façading Process
Research details entrepreneurial fraud in Silicon Valley, identifying 'façading' as a method where founders create illusory high-growth appearances.
SynkLoader Multitool Malware Employs Screen Hijacking
SynkLoader multitool malware leverages screen hijacking techniques and novel features for password theft, signaling potential ransomware threats.
Strategic Security: Aligning CISO Goals with Business Outcomes
CISOs face a double standard, hired for technical expertise but judged on business growth and customer trust.
ReliaQuest Thwarts ShinyHunters Social Engineering Attack on Okta SSO
ReliaQuest confirms a social engineering attack by ShinyHunters targeting an employee's Okta SSO, blocked from accessing applications or customer data.
AI-Powered PLC Attacks Target Critical Infrastructure
U.S. agencies warn that threat actors are using AI to target internet-exposed Siemens S7 Series PLCs in critical infrastructure sectors.
DOUBLECUP Malware: Appended PowerShell Payloads in PNG Files
Analysis of DOUBLECUP malware reveals a deceptive technique: appending cleartext PowerShell payloads to PNG image files, bypassing traditional steganography.
Grandoreiro Banking Trojan: New Evasion Tactics in Mexico
Grandoreiro banking Trojan resurfaces in Mexico, employing advanced evasion tactics after a law enforcement takedown to target financial users.
Anthropic Expands AI Security Access, Unveils $35M Open Source Fund
Anthropic is broadening access to its Mythos 5 AI security capabilities for defenders and launching a $35M fund for open-source project security.
FTP Banners Abused to Deliver E4del and PINHOLE RATs
Threat actors are using FTP server banners to hide commands, delivering new Windows remote access trojans E4del and PINHOLE via LNK-based infection chains.
Hardware Makers Integrate Post-Quantum Cryptography
Hardware manufacturers are proactively integrating post-quantum cryptography (PQC) to secure systems against future quantum computer-driven decryption threats.
CMMC Compliance: Confidence Rises, Proof Lags for DoD Contractors
DoD contractors report higher confidence in CMMC compliance, yet struggle to provide verifiable proof, leading to legal and contract risks.
Mabna Institute Espionage, BTR.sys Kernel Bypass, & Malware
Runtime Rebel details state-sponsored espionage by Mabna Institute, a kernel-level bypass using Microsoft Defender's BTR.sys, and new malware campaigns.