Advertisement
Coder Registry Compromise Pushes Malicious Terraform Modules
Attackers compromised Coder's Cloudflare infrastructure, delivering malicious Terraform modules that stole credentials from users of the development platform.
TeamPCP Hackers Arrested in Australia Over Supply Chain Attacks
Australian Federal Police arrest two men linked to TeamPCP, a cybercrime syndicate behind major software supply chain attacks and data extortion.
Hackers Abuse npm Mirrors to Host Phishing Redirects
Threat actors exploit npm and its mirroring platforms like UNPKG to host malicious HTML pages, impersonating Cloudflare CAPTCHAs for phishing redirects.
North Korea's Sapphire Sleet Targets Rust Supply Chain via arrayref Crate
North Korean actor Sapphire Sleet compromised a Rust maintainer's account to publish malicious `arrayref` crate versions, targeting the Rust supply chain.
Android Car Head Units Infected by MoYu Proxy Botnet Malware
A supply-chain attack by MoYu Group uses a legitimate update app to infect Android car head units, forming a proxy botnet for ad fraud.
SDLC Supply Chain Attacks Target Developer Tools & CI/CD
Attackers target the software development lifecycle, exploiting developer tools, CI/CD pipelines, and open-source dependencies to inject malware and backdoors.
Advertisement
Trojanized npm Packages Deliver AI-Powered RedC2 4.0 Linux Backdoor
Malicious npm packages deliver RedC2 4.0 Linux backdoor, featuring AI-assisted command and control for advanced post-exploitation.
Critical: Rust `arrayref` Crate Poisoned with Infostealer Malware
Hackers compromised `arrayref`, `append-only-vec`, and `internment` Rust crates to inject infostealer malware, impacting developers and downstream projects.
Rust Supply Chain Attack Puts Build-Time Malware in Crates
Compromised maintainer accounts on crates.io pushed malicious Rust crates with build-time malware executing during compilation.
TeamPCP Supply Chain Attack: Trivy Compromise Impacts 2,500 Orgs
A supply chain attack attributed to TeamPCP compromised over 2,500 organizations, primarily through Aqua Security's Trivy scanner, not LiteLLM.
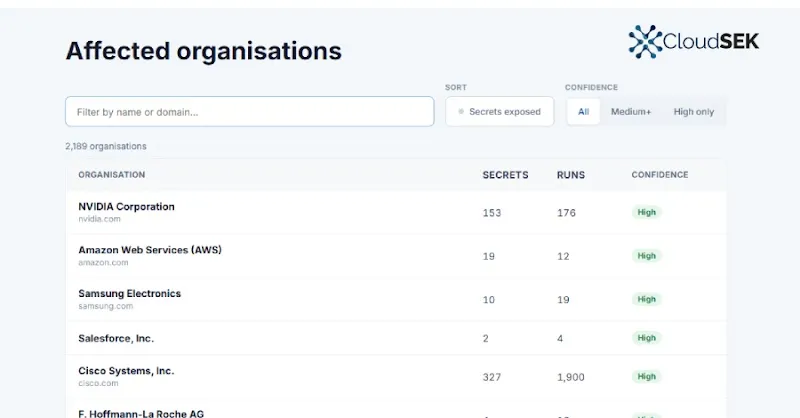
Malicious LiteLLM PyPI Releases Steal Cloud Credentials via TeamPCP
Malicious LiteLLM PyPI releases 1.82.7 and 1.82.8 exfiltrated cloud keys, SSH keys, and tokens from 2,100+ organizations in the TeamPCP supply chain campaign.
Mozilla Rotates Firefox GPG Key After Accidental GitHub Exposure
Mozilla issued a new GPG key for Firefox and Thunderbird artifacts after an accidental exposure in a private GitHub repository, mitigating supply chain risk.
BdThemes WordPress Plugin Supply Chain Attack Creates Rogue Admins
A supply chain attack on BdThemes WordPress plugins exploited an XSS vulnerability, creating stealthy rogue admin accounts and webshells.
Python Supply Chain: Malicious Packages Targeting Developers
Malicious Python packages exploit trusted ecosystems like PyPI, enabling supply chain attacks on developer systems. Learn about the threat and mitigation.
npm Supply Chain Attacks: Shai-Hulud, Miasma, and CI/CD Compromises
The npm ecosystem faces escalating supply chain attacks like Shai-Hulud and Miasma RAT, leading to credential theft and widespread package compromise.
Head Mare Breaches TrueConf, Trojanizes Client Installers
The Head Mare hacktivist group breached TrueConf video conferencing servers to distribute backdoored client installers, compromising user systems.
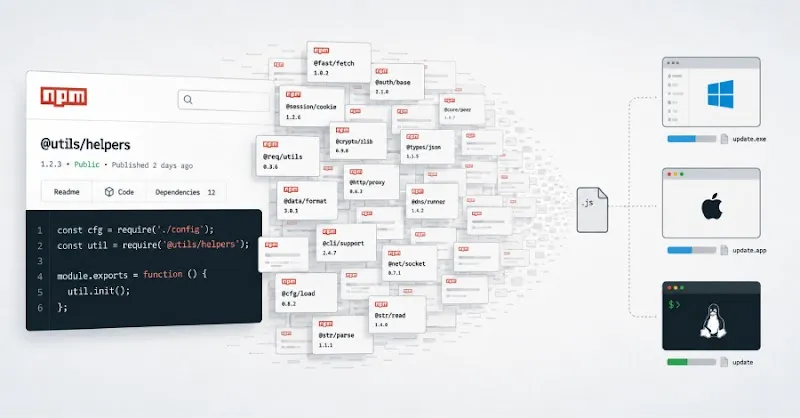
Critical npm Supply Chain Attack Delivers Cross-Platform RAT/Infostealer
Critical npm supply chain attack involving nearly 800 malicious packages delivers WEL1DROPPER RAT and infostealer to Windows, macOS, and Linux users.
Critical Backdoors & Supply Chain Attacks: Zbtlink Routers & QuickFox VPN Compromised
Urgent warning: Zbtlink routers ship with unauthenticated root backdoors, while QuickFox VPN delivers FDMTP implant via supply chain compromise.
ChainDrop npm Worm: Self-Propagating Software Supply Chain Threat
Analyze the ChainDrop self-propagating npm worm infecting major packages, harvesting credentials from memory, and compromising CI/CD pipelines.
Keyv npm Supply-Chain Attack: Worm Infection and Dead-Man Switch
Analyze the Keyv/cacheable npm supply-chain worm, its AI agent execution vectors, and why immediate credential revocation can trigger payloads.
Open VSX Evil Twin Extensions Exfiltrate Developer Data
77 malicious 'evil twin' extensions on Open VSX marketplace exfiltrated developer system and environment data, impersonating legitimate tools.
ChainDrop npm Supply Chain Attack Steals Developer Credentials
Massive ChainDrop npm supply chain attack compromises over 1,300 packages, stealing developer and cloud credentials through malicious preinstall scripts.
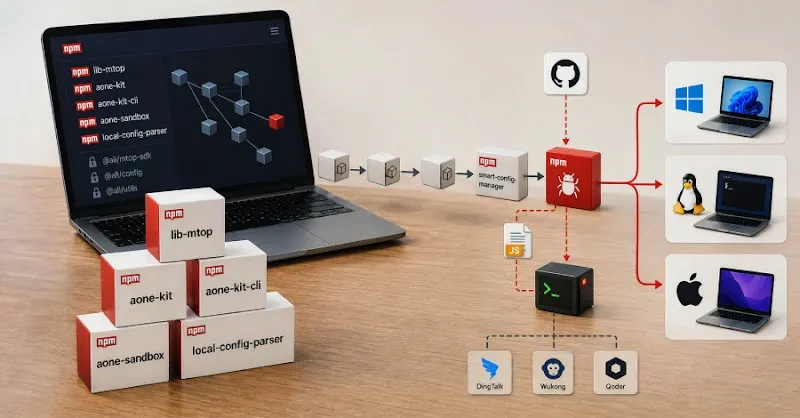
Malicious npm Packages Deliver Cross-Platform RAT to Alibaba Users
Discover how 18 malicious npm packages target Alibaba developer tools with a cross-platform remote access trojan in a supply chain attack.
CISA's Updated SBOM Guidance: Enhancing Software Supply Chain Transparency
CISA has released updated SBOM guidance, refining field definitions for greater software supply chain transparency. Debate continues on its impact on risk management.