Advertisement
Critical Backdoors & Supply Chain Attacks: Zbtlink Routers & QuickFox VPN Compromised
Urgent warning: Zbtlink routers ship with unauthenticated root backdoors, while QuickFox VPN delivers FDMTP implant via supply chain compromise.
ChainDrop npm Worm: Self-Propagating Software Supply Chain Threat
Analyze the ChainDrop self-propagating npm worm infecting major packages, harvesting credentials from memory, and compromising CI/CD pipelines.
Keyv npm Supply-Chain Attack: Worm Infection and Dead-Man Switch
Analyze the Keyv/cacheable npm supply-chain worm, its AI agent execution vectors, and why immediate credential revocation can trigger payloads.
Open VSX Evil Twin Extensions Exfiltrate Developer Data
77 malicious 'evil twin' extensions on Open VSX marketplace exfiltrated developer system and environment data, impersonating legitimate tools.
ChainDrop npm Supply Chain Attack Steals Developer Credentials
Massive ChainDrop npm supply chain attack compromises over 1,300 packages, stealing developer and cloud credentials through malicious preinstall scripts.
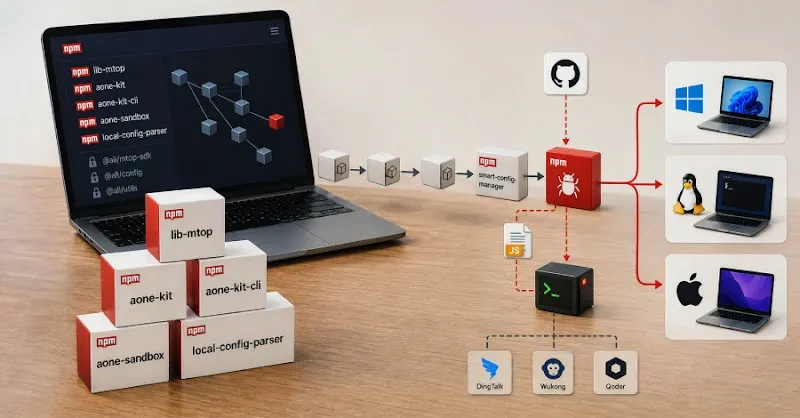
Malicious npm Packages Deliver Cross-Platform RAT to Alibaba Users
Discover how 18 malicious npm packages target Alibaba developer tools with a cross-platform remote access trojan in a supply chain attack.
Advertisement
CISA's Updated SBOM Guidance: Enhancing Software Supply Chain Transparency
CISA has released updated SBOM guidance, refining field definitions for greater software supply chain transparency. Debate continues on its impact on risk management.

Adform Script Poisoning: Crypto Wallet Swapping Attack
Adform's JavaScript was poisoned to swap crypto wallet addresses on customer sites.
North Korean Hackers Exploit npm Supply Chain: Debug & Chalk Under Attack
Amazon links North Korean hackers to supply chain attacks on popular npm packages Debug and Chalk, highlighting nation-state threat to open-source ecosystems.
Defending Against the 1,444% Surge in Open Source Supply Chain Attacks
GTIG reports a massive 1,444% spike in open source repository compromises. Learn how to mitigate threats from actors like UNC6780 and MIDNIGHT NEPTUNE.

FCC Blocks Foreign Robots and Power Inverters via Covered List
The FCC has added foreign-produced mobile robots and networked power inverters to the Covered List, citing supply chain risks and national security concerns.

Compromised Joyfill npm Packages Deliver DEV#POPPER RAT
Beta versions of @joyfill/layouts and @joyfill/components npm packages compromised to deliver a DEV#POPPER RAT upon import. Node.js users at risk.
CubePilot DNS Hijacking: How Attackers Intercepted UAV Flight Data
CubePilot drone software developer hit by DNS hijacking attack. Learn how to detect the exploit and verify ArduPilot firmware integrity in this guide.
GitHub and PyPI Policy Updates Target Supply Chain Security
GitHub and PyPI introduce new restrictions to thwart supply chain attacks, including a Dependabot cooldown and limits on historical package file uploads.
Lookout MSEC: Tackling Supply Chain Risks via Mobile App SBOMs
Lookout launches the Mobile Security Exposure Center (MSEC) to provide visibility into vulnerable third-party components and mobile app dependencies via SBOMs.

GitHub Dependabot 3-Day Cooldown: Mitigating Supply Chain Attacks
GitHub introduces a 3-day cooldown for Dependabot to prevent the rapid adoption of malicious packages, enhancing supply chain security for developers.
VS Code Marketplace Abuse: Detecting Malicious Developer Extensions
Researchers identify malicious Visual Studio Code extensions exfiltrating source code and credentials. Learn how to secure your development environment.
GitHub and PyPI Time-Based Defenses Against Supply Chain Attacks
GitHub and PyPI introduce time-based delays in Dependabot to mitigate supply chain attacks by preventing the immediate ingestion of malicious packages.

GitHub Actions Runners Weaponized to Attack cPanel and WHM Servers
Attackers are leveraging GitHub Actions runners and compromised Packagist packages to launch distributed attacks against cPanel and WHM server instances.

Trojanized Newtonsoft.Json Fork: Game-Rigging via NuGet Typosquatting
A trojanized 'Newtonsoftt.Json.Net' NuGet package, disguised as 'Newtonsoft.Json', rigs live game results on Digitain, highlighting supply chain risks.
Hugging Face Infrastructure Breach: Analyzing Autonomous AI Agent TTPs
Hugging Face discloses a breach where autonomous AI agents compromised production infrastructure, exposing internal datasets and secrets. Learn how to mitigate.

SleeperGem: Malicious RubyGems Target Developer Environments
The SleeperGem supply chain attack uses malicious RubyGems packages like git_credential_manager to compromise developers and deliver secondary payloads.

Malicious Vite npm Packages Deliver RAT via Blockchain C2
Seven malicious npm packages target Vite frontend projects. Dubbed ViteVenom, this software supply chain attack uses a four-tier blockchain C2 to deploy a RAT.
Risk Ledger Secures $32M Series B for Supply Chain Risk Platform
Risk Ledger raises $32 million in Series B funding to scale its collaborative supply chain security platform, addressing critical third-party risk management.