Advertisement
Cloudflare Launches Post-Quantum GeoKey Manager in Closed Beta
Cloudflare introduces a post-quantum geographically restricted key manager to protect customer data sovereignty against future decryption threats.
Securing AI Agent Permissions: Preventing Cloud Data Loss
AI agents can escalate privileges and perform unauthorized actions, leading to data loss. Learn how to implement granular controls for tool calls.
AgentCorruption: AWS Bedrock AgentCore Fleet Takeover Via Single Prompt
Analysis of 'AgentCorruption,' a patched vulnerability in AWS Bedrock AgentCore allowing compromise of an entire fleet via a single AI chatbot.
Cloudflare Interns Drive Key Innovations in Cloud Security
Cloudflare's intern program yields significant contributions, enhancing cloud security, optimizing infrastructure, and advancing post-quantum cryptography.
Cloudflare Traces: End-to-End Observability for Request Paths
Cloudflare Traces introduces end-to-end request tracing, offering deep visibility into security rules, caching, Workers, and origin interactions using OpenTelemetry.
SPIFFE/SPIRE Identity Misuse: Kubernetes Post-Exploitation
Discover how root access on a Kubernetes node enables workload identity spoofing in SPIFFE/SPIRE environments using the Spooffe tool.
Advertisement
Unmasking Cloud Identities: Behavioral Clustering for Detection
Palo Alto Networks Unit 42 reveals a behavioral clustering model to map cloud identities to functional roles, enhancing automated threat detection.
AWSCompromisedKeyQuarantine: Mitigating Exposed IAM Access Keys
AWS mitigates risks from exposed IAM access keys using the AWSCompromisedKeyQuarantine policy, integrating with GitHub secret scanning to protect cloud environments.
Kubernetes Operators: RBAC Misconfigurations & AI Risks
Overly permissive RBAC in Kubernetes operators, especially from OperatorHub, creates severe security risks and silent backdoors, heightened by agentic AI.
Cloud Security Index 2026: Multi-Cloud Risk Analysis
Intruder analyzed cloud misconfigurations across AWS, Azure, and GCP, revealing distinct risk profiles and universal IAM challenges.
Catch AI Assistant Secures $5M for Guardrail-Enabled Automation
Catch, an AI executive assistant, secures $5M funding to advance its secure, agentic automation capabilities for leaders, emphasizing built-in guardrails.
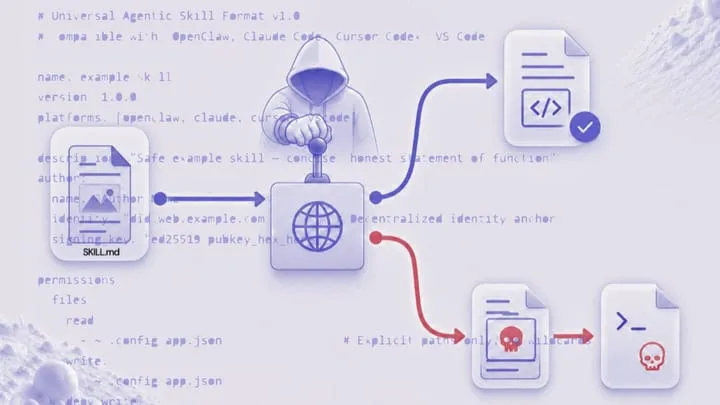
OWASP Releases Top 10 Security List and Universal Skill Format for AI
OWASP debuts a top 10 security list and Universal Skill Format to secure AI add-ons, addressing modern artificial intelligence risks.
Hundreds of Leaked AWS Keys Expose Corporate Cloud Accounts
Research reveals over 9,000 publicly exposed Amazon Web Services access keys remain active, including hundreds of root and administrator credentials.
CUSTODY Framework: Constraining Enterprise AI Agents
Enterprise security expert Jake Williams releases the CUSTODY framework to restrict agentic AI behavior following attacks on Hugging Face.
Securing Model Context Protocol (MCP) Traffic with Cloudflare
Learn how Cloudflare One identifies inspected Model Context Protocol traffic and controls AI agent tool calls to secure enterprise environments.
Security Blind Spots in AI Accelerators and Neo-Clouds
AI accelerators and neo-clouds introduce significant security blind spots, challenging traditional tools and creating an invisible supply chain threat to AI models.
ChatGPT Secure Sandbox PoC Enables C2-Style Influence
A researcher demonstrated a proof-of-concept attack chain enabling C2-style influence over ChatGPT's secure sandbox environment.

Azure Cosmos DB CosmosEscape Flaw: Cross-Tenant Database Access
Wiz researchers uncover CosmosEscape, a sandbox escape in Azure Cosmos DB's Gremlin API allowing unauthorized cross-tenant read and write access.
DataBahn Secures $40M for Agentic Data Control Plane Innovation
DataBahn raised $40 million to scale its agentic data control plane, addressing critical security and governance challenges in autonomous enterprise pipelines.
Mitigating Cloud Attack Paths from Non-Human Identity Sprawl
Non-human identity sprawl in cloud environments creates new attack paths through dormant or over-privileged credentials. Learn to detect and mitigate these risks.
Confused Deputy Flaws in Google Cloud & Azure: Admin Bypass
Analysis of 'Confused Deputy' vulnerabilities across Google Cloud and Microsoft Azure, enabling administrative privilege escalation and access control bypass.
Securing Autonomous AI Agents: Discovery and Governance Strategies
Learn how to detect and secure shadow AI agents within enterprise environments to prevent data leakage and unmanaged autonomous permission risks.
Azure Automation Default Setting: Cross-Tenant Identity Takeover
Runtime Rebel analyzes a critical security flaw in Azure Automation's default settings allowing cross-tenant identity takeover and access to sensitive data.
Microsoft 365 Outage: How an Automated Network Maintenance Bug Impacted Azure
Technical analysis of the Microsoft 365 and Azure outage caused by a bug in the automated network maintenance system, resulting in accidental IP route removal.