Advertisement
FBI Arrests Ploutus ATM Malware Developer, Disrupting TdA
FBI arrests Anibal Alexander Canelon Aguirre, primary developer of Ploutus ATM malware, disrupting Tren de Aragua's extensive jackpotting operations across 47 US states.
ClingSTUN Backdoor Exploits 24 IoT Flaws for Proxy Network
The ClingSTUN Linux backdoor exploits 24 known vulnerabilities in IoT devices, turning them into proxy nodes and using STUN servers to obscure communications.
ClingSTUN Linux Backdoor Exploits Dozens of Flaws via STUN Protocol
FortiGuard Labs identifies ClingSTUN, a Linux backdoor that abuses the STUN protocol and exploits dozens of flaws for self-propagation.
CloudSyncD Backdoor Targets macOS Users via Fake Zoom Installer
macOS users are targeted by CloudSyncD, a persistent backdoor delivered via fake Zoom installers, gaining root access through social engineering.
CL-CRI-1171 PPI Network Targets Gamers & Enterprises
Unit 42 uncovers CL-CRI-1171, a pay-per-install network spreading malware via YouTube and SEO poisoning to gamers and critical infrastructure.
AMOS Stealer: Evolving macOS Info-Stealer Tactics & Mitigation
Analysis of AMOS stealer macOS activity, detailing distribution, persistence, data exfiltration, and mitigation guidance for defenders.
Advertisement
Sophisticated Malicious npm Packages Evade Detection
Sophisticated malicious npm packages designed to evade install-time scanning pose a significant supply chain risk, demanding runtime behavioral analysis.
Warlock Ransomware Targets Spanish, Portuguese Orgs
Warlock ransomware campaign targets large organizations in Spain and Portugal, exhibiting characteristics of both cybercrime and state-associated APTs.
SC Self-Healing WordPress Backdoor and wpForo SQLi Exploitation
A sophisticated 'self-healing' WordPress backdoor (SC) utilizes multiple persistence mechanisms, including shared memory.
ClearFake WebDAV Delivers Stealers & RATs to Ukrainian Gov
ClearFake WebDAV infection chain leverages Cloudflare Workers and BNB Smart Chain to deploy Amatera stealer, ZigCryptoStealer, and NetSupport Manager.
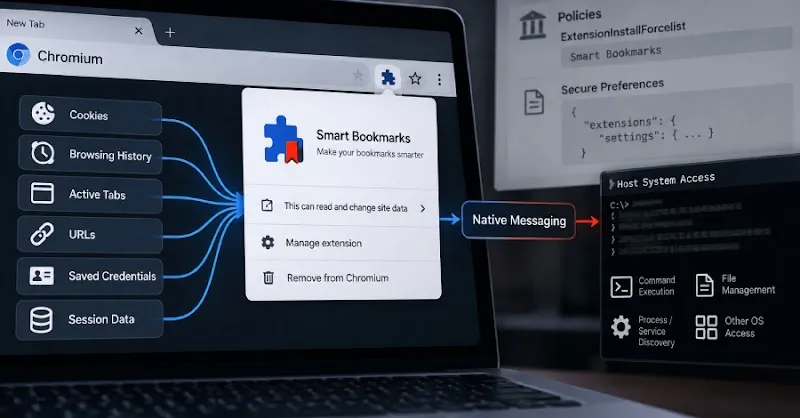
PEEP Backdoor Turns Browsers into OS Command Execution Tools
PEEP toolkit leverages Chrome and Edge as post-compromise backdoors, enabling host command execution, data exfiltration, and session hijacking.
REVSTEALER Modules Disable Defenses, Deploy Miner, Steal Data
Elastic Security unveils four REVSTEALER-linked modules that disable Windows defenses, deploy crypto miners, and exfiltrate sensitive user data.
ClickFix Payloads via Blockchain Affect 5,400+ Websites
Over 5,400 compromised WordPress and PrestaShop sites deliver ClickFix payloads and WebRTC stagers from BNB Smart Chain via EtherHiding.
Silver Fox Malware Campaign Impersonates Software Vendors
An active Silver Fox malware campaign uses fake software download sites to disable Windows Update and weaken Microsoft Defender defenses.
WordlistLoader Evades Detection, Delivers Amatera Infostealer
WordlistLoader uses a novel text-based obfuscation to bypass security, deploying the Amatera infostealer in ClickFix-style campaigns, posing a significant threat.
SynkLoader Multitool Malware Employs Screen Hijacking
SynkLoader multitool malware leverages screen hijacking techniques and novel features for password theft, signaling potential ransomware threats.
DOUBLECUP Malware: Appended PowerShell Payloads in PNG Files
Analysis of DOUBLECUP malware reveals a deceptive technique: appending cleartext PowerShell payloads to PNG image files, bypassing traditional steganography.
Grandoreiro Banking Trojan: New Evasion Tactics in Mexico
Grandoreiro banking Trojan resurfaces in Mexico, employing advanced evasion tactics after a law enforcement takedown to target financial users.
FTP Banners Abused to Deliver E4del and PINHOLE RATs
Threat actors are using FTP server banners to hide commands, delivering new Windows remote access trojans E4del and PINHOLE via LNK-based infection chains.
ToxicPanda 2.0 Android Malware Abuses Wireless ADB and VPN
ToxicPanda 2.0 Android malware uses VPN permissions to block Google Play and abuses Wireless ADB to gain shell access and deploy overlays.
Banking Trojans Manic, Grandoreiro, ToxicPanda 2.0 Active
New and updated banking trojans Manic, Grandoreiro, and ToxicPanda 2.0 are actively targeting financial users globally, stealing credentials and data.
Android Car Head Unit Malware Spreads via Built-In Updaters
Kaspersky discovered a new malware family targeting Android car head units via DoFun firmware updaters to build an ad fraud and proxy botnet.
SynkLoader Malware Steals Credentials in Microsoft Teams Phishing
New SynkLoader malware distributed via Microsoft Teams phishing campaigns uses a fake lock screen to steal Windows credentials, enabling corporate network access.
Evooo1Bot Linux Botnet: Beyond DDoS with Exploits & Credential Theft
Evooo1Bot Linux botnet evolves, adding exploitation modules, credential theft, and SOCKS relays, transforming compromised devices into persistent attacker infrastructure.