Advertisement
Android Car Head Unit Malware Spreads via Built-In Updaters
Kaspersky discovered a new malware family targeting Android car head units via DoFun firmware updaters to build an ad fraud and proxy botnet.
SynkLoader Malware Steals Credentials in Microsoft Teams Phishing
New SynkLoader malware distributed via Microsoft Teams phishing campaigns uses a fake lock screen to steal Windows credentials, enabling corporate network access.
Evooo1Bot Linux Botnet: Beyond DDoS with Exploits & Credential Theft
Evooo1Bot Linux botnet evolves, adding exploitation modules, credential theft, and SOCKS relays, transforming compromised devices into persistent attacker infrastructure.
AmnesiaStealer macOS Malware Hijacks Browser Sessions via Remote Control
AmnesiaStealer targets macOS users via ClickFix attacks, cloning Chromium profiles to enable live remote control of authenticated browser sessions.
Evooo1Bot Linux Botnet Turns Routers Into SOCKS5 Relays
A new Mirai-based modular Linux botnet called Evooo1Bot targets internet routers, turning them into SOCKS5 traffic relay nodes.
New JWR Phishing Framework Bypasses MFA with Live Monitoring
JWR, a new real-time phishing framework, uses WebSockets to bypass MFA and steal sensitive data via SMS lures, posing a critical threat.
Advertisement
JWR Phishing Framework: Real-time Data Theft via PhaaS
The JWR phishing framework, a variant of The Outsider PhaaS, harvests payment data, PII, and 2FA codes in real-time via operator-controlled sessions.
Android Malware WindRelay & SpyNote: NFC Relay for Loan Fraud
A sophisticated Android malware combination, WindRelay and SpyNote, facilitates real-time NFC credit card fraud and unauthorized loans.
Malicious Chrome VPN Extensions Route Traffic via SOCKS5 Proxies
Over 730 free Chrome VPN extensions are redirecting user browser traffic through SOCKS5 proxies, enabling man-in-the-middle attacks and data interception.
Deadlock Ransomware Uses Blockchain for C2 Resilience
Deadlock ransomware uses Polygon blockchain smart contracts and Session to resist infrastructure takedown and evade law enforcement.
Kimwolf v7 Botnet Evolves with Advanced DDoS and C2 Resilience
Kimwolf v7, an Android/IoT botnet, enhances DDoS capabilities with HTTP/2 fingerprinting and robust, multi-layered C2 infrastructure.
Aeternum Botnet Leverages Polygon Blockchain for Resilient C2
Aeternum botnet uses Polygon blockchain smart contracts for C2, making it resilient to takedowns. Security professionals must understand its decentralized operations.
Solidity Pro VS Code Extensions Steal Crypto Wallets & Credentials
Malicious 'Solidity Pro' VS Code extensions steal crypto wallets, API keys, and credentials, using delayed activation to evade detection. Immediate removal is advised.
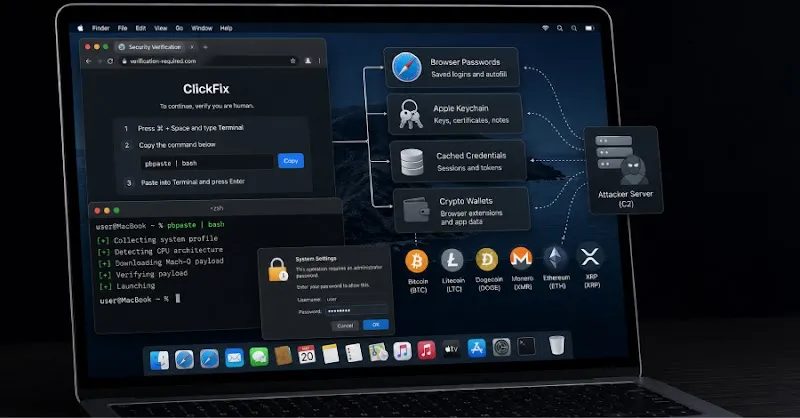
ClickFix Attacks Deliver macOS Stealer Targeting Crypto
ClickFix social engineering campaigns target macOS users with Go-based infostealers designed to drain cryptocurrency wallets and credentials.
Vidar Stealer & XMRig Campaign Leverages Malvertising, AMSI Bypass
Financially motivated campaign delivers Vidar stealer and XMRig miner via malvertising for cracked software, targeting consumers and SMBs globally.
TuxBot v3: LLM-Assisted IoT Botnet Framework Analysis
Analysis of TuxBot v3 Evolution, a modular IoT botnet framework developed with LLM assistance, leveraging Telnet brute-force and C2 for DDoS.
XCSSET v40 Malware Targets macOS Developers via Xcode
Discover how XCSSET v40 targets macOS developers using fileless persistence, memory execution, and Xcode project supply chain attacks.
msaRAT: Chaos Ransomware's Covert Browser-Based C2
Cisco Talos uncovers msaRAT, a new Rust-based RAT used by Chaos ransomware for covert C2 via Chrome DevTools Protocol, evading detection.
ClickFix Attack Deploys macOS Infostealer for Crypto Theft
The ClickFix attack leverages a Go-based macOS infostealer to pilfer cryptocurrency, browser data, and Apple Keychain credentials via a Bash script loader.

Fuyao Operation: Android TV Boxes Mimic Phones, Hijack Bandwidth
Cheap Android TV boxes are pre-installed with Fuyao malware, impersonating phones for ad fraud and turning devices into residential proxy nodes.
SSH Botnet Reconnaissance Before Linux Cryptominer Deployment
An SSH botnet performs extensive hardware and system reconnaissance on Linux targets before deploying an optimized cryptocurrency miner. Weak credentials exploited.
Flying Eagle Mobile RAT Builder: China's Infostealer-as-a-Service
Analysis of the 'Flying Eagle' mobile RAT builder, a sophisticated malware-as-a-service platform from China, used by threat groups to deploy infostealers targeting…

Tengu Botnet Exploits Linux Watchdog for Reboot-Based Persistence
The Mirai-derived Tengu botnet utilizes hardware watchdog timers to trigger reboots when its process is terminated, ensuring persistence on Linux devices.
Dysphoria Botnet: 200K Devices Engaged in DDoS and Traffic Relay
Analysis of the Dysphoria DDoS botnet, which has compromised 200,000 devices globally for denial-of-service attacks and traffic relay operations. Learn mitigation.