Advertisement
CVE-2015-3306: ProFTPD Improper Access Control Exploitation
Critical improper access control vulnerability in ProFTPD (CVE-2015-3306) allows remote file manipulation, actively exploited.
CVE-2021-3199: ONLYOFFICE Docs RCE via Path Traversal
Actively exploited path traversal vulnerability [CVE-2021-3199] in ONLYOFFICE Docs Server enables remote code execution when JWT is used. Immediate patching is critical.
CVE-2023-22894: Strapi Cleartext Storage Exploited
CISA confirms active exploitation of CVE-2023-22894, a Strapi cleartext storage vulnerability exposing sensitive user data, potentially chained for RCE.
CVE-2016-3081: Apache Struts RCE via Command Injection — Patch Now
CISA confirms active exploitation of CVE-2016-3081, an Apache Struts command injection flaw leading to remote code execution.
CVE-2015-5477: Remote DoS in ISC BIND via TKEY Queries
CISA confirms active exploitation of CVE-2015-5477, a remote Denial of Service vulnerability in ISC BIND affecting critical DNS infrastructure.
Cisco Patches 35 Vulnerabilities: Critical Flaws in Meraki, NX-OS
Cisco released patches for 35 vulnerabilities, including multiple critical issues in Meraki, License On-Prem, NX-OS, and APIC products.
Advertisement
Atlassian Arbitrary File Access Exploitation Scans Observed
Atlassian products are targeted by scans exploiting CVE-2026-21589 for arbitrary file access, potentially exposing sensitive configuration.
Multi-Vendor Patches: Adobe, Apple, Foxit, Microsoft Vulnerabilities
Cisco Talos discloses patched privilege escalation, RCE, and information disclosure vulnerabilities across Adobe, Apple, Foxit, and Microsoft products.
WordPress Plugin XSS: Ninja Forms & WPC Product Bundles Exploited
Hackers are exploiting XSS vulnerabilities in Ninja Forms and WPC Product Bundles for WooCommerce to install backdoors and create rogue admin accounts on WordPress sites.
Pwn2Own Ireland Uncovers 32 Zero-Days Across Diverse Systems
Security researchers exploited 32 zero-day vulnerabilities in mobile phones, smart home devices, and AI systems on day one of Pwn2Own Ireland 2026.
Apple iOS Inactivity Reboot Bypass by Magnet Forensics
A cyber-weapons manufacturer exploits a possible iOS vulnerability, allowing law enforcement to bypass automatic reboot and preserve data indefinitely.
LibreOffice & OpenOffice RCE via Malicious Spreadsheets
Vulnerabilities in LibreOffice (CVE-2026-63277) and Apache OpenOffice (CVE-2026-59265) allow RCE via malicious spreadsheets without macro warnings.
CVE-2026-61500: Rejetto HFS RCE via Weak Signing Key Flaw
Hackers are actively scanning for a critical RCE flaw in Rejetto HFS versions 3.0.0-3.2.0 (CVE-2026-61500), enabling session forgery and account takeover.
CVE-2026-96940: Exchange Server Auth Flaw Exposes Mailboxes
Microsoft addresses a high-severity flaw, CVE-2026-96940, in on-premises Exchange Server allowing authenticated attackers to read mailboxes.
CVE-2026-88779: NetScaler DoS Exploit – Patch Now
CISA confirms active exploitation of CVE-2026-88779 in Citrix NetScaler ADC and Gateway, leading to Denial of Service. Immediate action required.
Dell CSM Critical Flaws: Unauthenticated Admin on Kubernetes Nodes
Dell Container Storage Modules (CSM) versions prior to 1.17.0 are critically vulnerable, enabling unauthenticated admin access and Kubernetes node compromise.
Dell Container Storage Modules Flaws Give Attackers Admin Privileges
Dell patches multiple maximum severity vulnerabilities in Container Storage Modules impacting enterprise storage and Kubernetes environments.
Fortra BoKS Patches Critical Vulnerabilities: RCE, Auth Bypass
Fortra patches critical flaws in BoKS Core Privileged Access Manager, including authentication bypass (CVE-2026-79901) and command injection (CVE-2026-79898).
SWIFT & Government Middleware RCE Risk
Critical RCE vulnerabilities in middleware used by SWIFT banking and government sectors enable hardware-based MFA exploits. Immediate patching is vital.
CVE-2026-102489: Zammad Session Fixation Leads to RCE – Patch Now
CISA confirms active exploitation of CVE-2026-102489 in Zammad, a session fixation vulnerability enabling remote code execution.
CVE-2026-102490: Zammad Privilege Escalation Exploit in Wild
CVE-2026-102490 allows local Zammad users to escalate privileges to root. CISA confirms active exploitation; patch immediately.
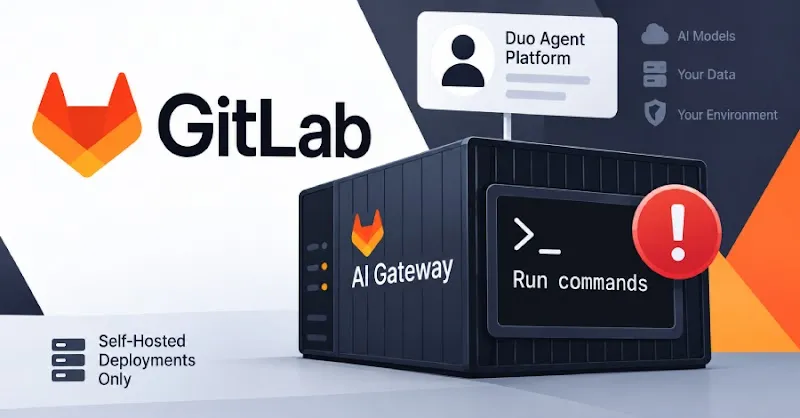
CVE-2026-90970: GitLab AI Gateway RCE Flaw — Update Self-Hosted Now
GitLab patched a critical AI Gateway flaw (CVE-2026-90970). Logged-in Duo Agent users can achieve remote command execution on self-hosted instances. Update immediately.
Vulnerability Backlogs: The Ownership Problem
Many organizations struggle with growing vulnerability backlogs due to unclear asset ownership and remediation responsibilities, increasing cyber risk.
Cisco FMC RCE via CVE-2026-20079: Patch Now
Active exploitation of critical Cisco Secure Firewall Management Center vulnerabilities (CVE-2026-20079, CVE-2026-20316) by state-sponsored and crimeware actors.