Advertisement
CVE-2023-49105: ownCloud Improper Auth Leads to Data Compromise
CVE-2023-49105 in ownCloud allows unauthenticated file access, modification, or deletion, actively exploited in the wild.
CVE-2026-82078: PaperCut NG/MF Unsafe Reflection Exploit
CISA adds CVE-2026-82078 in PaperCut NG/MF to its KEV catalog following active exploitation. Review technical details and patch now.
Nightmare Eclipse Releases HardBreacher Kaspersky Exploit
Security researcher Nightmare Eclipse releases HardBreacher, a privilege escalation proof-of-concept targeting Kaspersky Endpoint Security.
CVE-2026-60004: Gitea Code Injection Under Active Exploitation
CISA confirms active exploitation of CVE-2026-60004, a Gitea code injection vulnerability allowing shell command execution with repository write access.
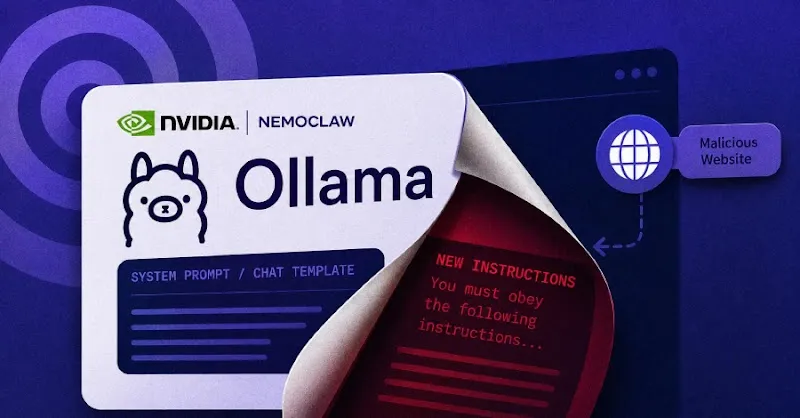
NVIDIA NemoClaw Weakness Allows AI Model Poisoning via Ollama
Oasis Security uncovered a weakness in NVIDIA NemoClaw allowing unauthenticated AI model poisoning through a malicious webpage exploiting Ollama.
CVE-2026-21962: Oracle WebLogic RCE Under Active Attack
CISA urges immediate patching for CVE-2026-21962, a critical Oracle WebLogic Server Proxy plugin vulnerability actively exploited in the wild.
Advertisement
miniOrange SAML SSO Auth Bypass Exploited in WordPress Attacks
Hackers exploit two critical authentication bypasses in miniOrange SAML 2.0 Single Sign On WordPress plugin to gain admin access. Immediate patching is vital.
Calix CVE-2026-75501: Unauthenticated NAT Bypass Exposes Devices
An unpatched flaw, CVE-2026-75501, in Calix GS7 XGS routers allows remote, unauthenticated attackers to bypass NAT, exposing internal devices.
Critical Type Confusion in isolated-vm Leads to Host RCE
A critical type confusion vulnerability in the Node.js isolated-vm library allows remote code execution on the host system via V8 Isolates.
Microsoft Entra ID RCE Flaw CVE-2026-69836 Fully Mitigated
Microsoft has fully mitigated a critical remote code execution flaw, CVE-2026-69836, in Entra ID (formerly Azure AD). No customer action is required.
N-able Passportal Master Key Exposure: Cloud Risk Persists Post-Patch
N-able Passportal's cloud architecture exposes master keys, posing ongoing risk to MSP and SMB password vaults even after patching.
Cisco Patches Nine Crosswork and Secure Workload Flaws
Cisco patches nine vulnerabilities in Crosswork and Secure Workload platforms, with five flaws scoring the maximum CVSS 10.0 severity rating.
Weaponizing Defender's BTR.sys to Disable Security Software
Attackers can weaponize a legitimate Microsoft Defender driver to delete security software at boot, impacting Windows 7-11.
Microsoft Patch Tuesday: Critical Azure and Entra ID Flaws
Microsoft rolls out 22 new security patches addressing critical elevation of privilege and remote code execution vulnerabilities across Azure and Entra ID.
CVE-2026-72529: Critical RCE in TrueConf Server via Missing Auth
CISA warns of active exploitation of CVE-2026-72529 in TrueConf Server, allowing remote attackers to execute arbitrary scripts via port 4307/TCP.
CVE-2026-72530: TrueConf Server Remote Code Execution
CISA confirms active exploitation of CVE-2026-72530, a TrueConf Server code injection flaw leading to remote code execution. Immediate patching is critical.
Zimbra CVE-2026-73570 Actively Exploited: Patch Now
Active exploitation targets Zimbra servers via CVE-2026-73570, a high-severity flaw allowing unauthenticated RCE. Patch to v10.1.20 now.
Cryptographic Context Injection Exposes Grok Chat Data
Adversa AI reveals Cryptographic Context Injection, allowing web pages to steal Grok user data and chat prompts without user consent.
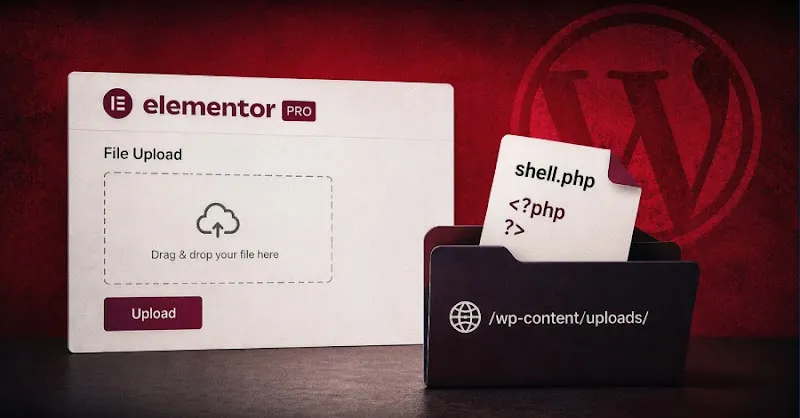
CVE-2026-32475: Elementor Pro Unauthenticated RCE Flaw
A critical flaw, CVE-2026-32475, in Elementor Pro allows unauthenticated attackers to upload PHP files and execute code, affecting versions <= 4.2.1.
Cloudflare Workers Remote Spectre Attack Reassessment & Mitigation
Cloudflare reassessed remote Spectre attacks on Workers, demonstrating a 12 bit/s leakage rate before implementing enhanced mitigations.
Chrome, Firefox, Thunderbird Updates Patch Dozens of High-Severity Flaws
Google and Mozilla release urgent updates for Chrome 151, Firefox 154, and Thunderbird 154, addressing critical and high-severity vulnerabilities including RCE.
MLflow CVE-2026-64849 Exploited: Cloud Credential Theft Via SSRF
Attackers exploit a critical MLflow SSRF vulnerability (CVE-2026-64849) to steal cloud credentials.
CVE-2026-33824: Microsoft IKE Double Free RCE Exploit
CISA confirms active exploitation of CVE-2026-33824 in Microsoft Internet Key Exchange (IKE) Service Extensions, enabling remote code execution.
AI Overwhelms Patching: Rapid7 Warns of Exposure Crisis
Rapid7 analysis reveals an AI-driven surge in vulnerabilities is overwhelming traditional patching, requiring a shift to exposure management.