Advertisement
Samsung Galaxy RCE: How Bixby Was Exploited via $50k Chain
Discover how security researchers chained vulnerabilities to turn Bixby against Samsung phones, achieving remote system-level compromise.
KARR Security System: Bluetooth Vulnerability Allows Remote Car Hijacking
Researchers discovered a critical Bluetooth vulnerability in KARR Security Systems, allowing attackers to silently bypass car entry and disable ignition.
CISA Warns: Actively Exploited Langflow, N-central, and Tomcat Vulnerabilities
CISA warns federal agencies and organizations about active exploitation of critical vulnerabilities in IBM Langflow, N-able N-central, and Apache Tomcat.
CVE-2026-34486: Apache Tomcat Encryption Bypass – Detection and Mitigation Guide
Apache Tomcat CVE-2026-34486 enables EncryptInterceptor bypass, exposing sensitive data; learn impact, detection, and remediation steps.
CVE-2026-18556: N-able N-central Authentication Bypass Actively Exploited
CISA added CVE-2026-18556 to its KEV catalog, confirming active exploitation of an N-able N-central authentication bypass vulnerability.
Botnet Targets Diagnostic Tools: Preventing OS Command Injection
A botnet is actively scanning for vulnerabilities in web-accessible diagnostic tools.
Advertisement
Firebase Misconfiguration in tl;dv AI Tool Exposes Sensitive Meeting Data
A Google Firebase misconfiguration in the tl;dv AI meeting tool allows unauthorized access to sensitive government and corporate video call information.
Google ADK for Python RCE: Agent-to-Agent Attacks Expose Secrets
Pillar Security uncovered agent-to-agent RCE flaws in Google's ADK for Python, allowing secret exposure and PR tampering, risking supply chain integrity.
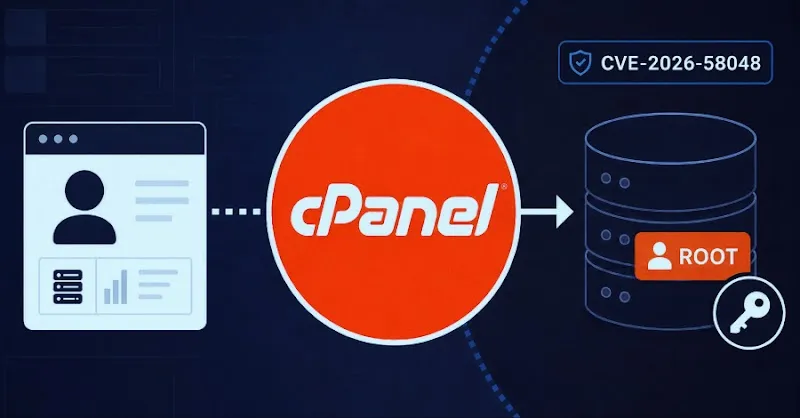
CVE-2026-58048: cPanel & WHM Critical SQL Privilege Escalation
A critical flaw in cPanel & WHM (CVE-2026-58048) allows authenticated users to execute SQL as database root, potentially leading to OS-level compromise.
CVE-2026-18577: Attackers Exploit N-able Patch Bypass
Security teams face active exploitation of CVE-2026-18577, an N-able authentication bypass vulnerability granting administrator access.
CVE-2026-50522: SharePoint RCE via Deserialization — Patch Now
CISA confirmed active exploitation of CVE-2026-50522 in Microsoft SharePoint. Attackers leverage a deserialization vulnerability to execute code remotely. Patch…
CVE-2026-60137: WordPress Core SQL Injection to RCE — Patch Now
CISA warns of active exploitation for CVE-2026-60137, a WordPress Core SQL Injection vulnerability chaining to RCE for unauthenticated attackers.
CVE-2026-16232: Check Point SmartConsole Admin Bypass via Auth Flaw
CISA warns of active exploitation for CVE-2026-16232, an improper authentication vulnerability in Check Point SmartConsole allowing unauthenticated admin access…

Coldcard Firmware Flaw Enables $70M Bitcoin Theft
A critical firmware flaw in Coldcard hardware wallets, specifically a March 2021 integration error affecting seed generation, led to over $70 million in Bitcoin theft.
Rails Active Storage RCE via Critical Flaw — Patch Now
A critical flaw in Rails Active Storage permits unauthenticated attackers to read arbitrary files and potentially achieve remote code execution.

Google Chrome Updates Resolve 1,442 Security Flaws
Google Chrome recently addressed 1,442 security flaws across versions 149, 150, and 151. Learn why immediate updates are crucial for user security.
CVE-2025-68686: Fortinet FortiOS Patch Bypass for Post-Exploit Persistence
CISA warns of active exploitation of CVE-2025-68686 in Fortinet FortiOS, allowing attackers to bypass a patch for post-exploit persistence and expose sensitive data.
CVE-2026-20316: Cisco Secure FMC Hard-coded Password Vulnerability
CISA confirms active exploitation of CVE-2026-20316, a hard-coded password vulnerability in Cisco Secure Firewall Management Center.
VMware Critical Flaws: Auth Bypass, RCE, VM Escapes Patched
VMware has patched critical vulnerabilities across vCenter, ESX, Workstation, and Fusion, addressing authentication bypass, remote code execution, and VM escapes.
AI-Powered Vulnerability Research: Google Patches 1,000+ Chrome Bugs
Google utilizes Big Sleep AI to identify and remediate over 1,000 security vulnerabilities in Chrome releases, signaling a shift in automated bug hunting.

Persistent Prompt Injection Risks in Microsoft 365 Copilot for Word
Researchers demonstrate how hidden instructions in Word documents can persist through Microsoft 365 Copilot drafting, creating risks of malicious prompt propagation.
Ruflo MCP Bridge Command Execution: Mitigation Guide
Unauthenticated attackers can exploit a critical vulnerability in Ruflo to execute commands in the MCP bridge container and spawn rogue AI swarms.

Cisco FMC CVE-2026-20316: Static Credentials Actively Exploited
CISA adds CVE-2026-20316 to its Known Exploited Vulnerabilities catalog following active exploitation of static credentials in Cisco Firewall Management Center.

CVE-2026-66066: Unauthenticated File Read in Rails Active Storage
Unauthenticated attackers can exploit CVE-2026-66066 in Ruby on Rails Active Storage to read sensitive server files, potentially leading to full compromise.