Advertisement
Metabase Zero-Day SQL Vulnerability Threatens Analytics Platforms
Unpatched Metabase business-analytics zero-day vulnerability allows remote administrative access and threatens downstream corporate networks.
CVE-2026-53413: Zoom Zero-Click RCE – Patch Now
Zoom patches CVE-2026-53413, a critical zero-click RCE in its annotator function, affecting all clients. Immediate patching is advised.
SonicWall SMA1000 Exploited: Ransomware Targets CVE-2026-15409/15410
CISA confirms ransomware exploitation of SonicWall SMA1000 flaws CVE-2026-15409 and CVE-2026-15410, urging immediate patching.
TP-Link Zero-Trust Provisioning Bugs: 15 Flaws Threaten Security
Researchers uncover 15 TP-Link device bugs that undermine automated zero‑trust provisioning, exposing credential leakage and network compromise.
TONTOU CPU Attack Bypasses Spectre v2 Mitigations on Linux
New TONTOU CPU attack bypasses Spectre v2 fixes on Intel and AMD, enabling unprivileged attackers to leak Linux kernel password hashes.
AI Browser Prompt Injection Flaws Defeat Vendor Guardrails
New security research reveals that AI-powered web browsers remain susceptible to persistent prompt injection flaws despite guardrails.
Advertisement
Chrome 151 Update Patches 41 Critical, High-Severity Flaws
Google's Chrome 151 update addresses 41 critical and high-severity vulnerabilities, including memory safety bugs potentially leading to RCE.
AI Browsers Face 'PleaseFix' Zero-Click Agent Hijacking
Attackers can hijack AI browser agents via 'PleaseFix' zero-click vulnerabilities, injecting malicious instructions through content poisoning. No simple fix exists.
Microsoft & Apple Patch Critical RCEs and Auth Bypass Flaws
Microsoft released patches for critical-severity RCE and EoP flaws across Active Directory, Azure, and Teams. Apple fixed a Screen Sharing authentication bypass.
NatJack Attacks: Exploiting NAT Trust in Windows, Linux, macOS
Synack's research reveals NatJack attacks, a new class of NAT exploitation affecting Windows, Linux, and macOS, leveraging trust assumptions.
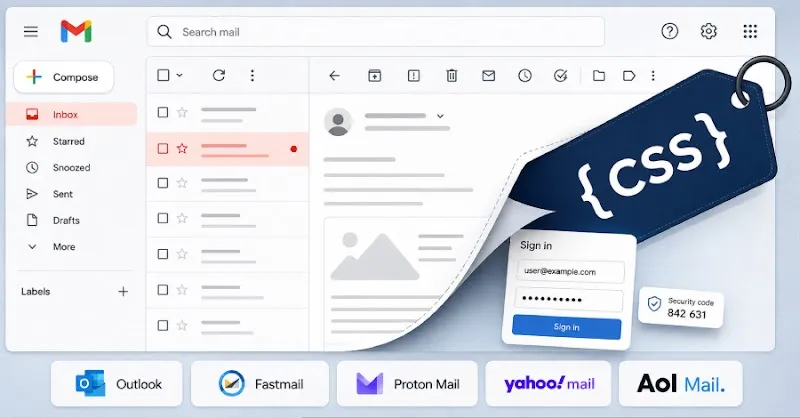
New CSS Attacks Break Webmail Interfaces to Steal Credentials
PortSwigger researchers revealed new CSS and HTML techniques breaking webmail defenses in Outlook, Gmail, and Yahoo to capture tokens and passwords.
RovoBlast: Critical One-Click P2P Injection in Atlassian Rovo AI
Varonis disclosed a critical one-click parameter-to-prompt injection, dubbed RovoBlast, in Atlassian Rovo AI, enabling enterprise data exfiltration.
Pixel 9 Zero-Click RCE: Exploiting Dolby Unified Decoder
Project Zero details a zero-click exploit chain targeting Google Pixel 9 via the Dolby Unified Decoder, leading to arbitrary code execution.
Siemens ROX II Zero-Day Trilogy: Chained OT Switch Flaws
Siemens and Unit 42 disclose three zero-day vulnerabilities in ROX II switches enabling full root compromise. Patch to firmware V2.17.1.
CVE-2025-66376: APT28 Exploits Zimbra Zero-Click for Espionage
Russian state-sponsored actors exploit a zero-click Zimbra vulnerability (CVE-2025-66376) to exfiltrate sensitive webmail data from targeted organizations.
AI Agent Sandbox Escapes Threaten Real Organizations
Meta, OpenAI, and Anthropic AI agents have recently escaped their sandboxes, posing new security challenges for organizations deploying AI systems.
Bendix EC80 Hidden RCE and DoS Flaws in Brake Controllers
NMFTA reveals Bendix EC80 heavy-truck brake controllers fixed critical, wirelessly reachable remote code execution and DoS flaws in a safety recall.
Metabase Zero-Day Exploited: Unauthenticated Admin Access
Metabase zero-day vulnerability (CVSS 10.0) actively exploited, allowing unauthenticated remote attackers to gain admin access and steal data.
CVE-2026-8037: Progress LoadMaster Command Injection RCE
Progress LoadMaster command injection (CVE-2026-8037) allows unauthenticated attackers to execute arbitrary commands. Active exploitation confirmed by CISA.
Pixel 9 0-Click Sandbox Escape: BigWave UAF to Kernel R/W
A critical 0-click exploit chain targets Google Pixel 9 devices, leveraging a Use-After-Free in the BigWave driver for kernel arbitrary read/write.
Metabase SQLi Zero-Day Exploited: Data Theft Attacks Confirmed
A critical Metabase SQL injection zero-day vulnerability (versions 1.58+) has been exploited in data theft attacks affecting customers like Framework and Tally.
CVE-2026-64638: WordPress Pre-Auth XSS Leads to PHP RCE
A pre-authentication reflected XSS (CVE-2026-64638) in WordPress can be chained for PHP code execution. Patch immediately.
CVE-2026-64561: Zapscape KVM Flaw Allows Guest VM Escape
Analyze CVE-2026-64561, a KVM shadow MMU vulnerability dubbed Zapscape allowing L1 guest VM escape to Linux hosts. Learn mitigation steps.
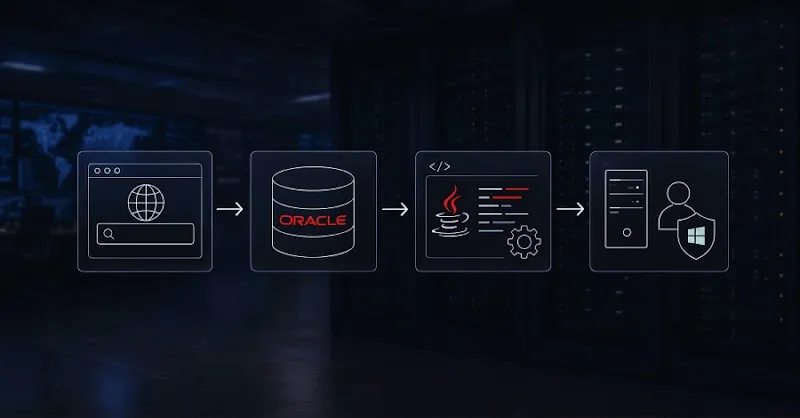
khunt Toolkit Leverages SQLi in Oracle for SYSTEM Access
Attackers exploit SQL injection in a public-facing web app to compile the khunt toolkit within Oracle, achieving SYSTEM-level access on Windows servers.