Advertisement
CVE-2026-72530: TrueConf Server Remote Code Execution
CISA confirms active exploitation of CVE-2026-72530, a TrueConf Server code injection flaw leading to remote code execution. Immediate patching is critical.
Zimbra CVE-2026-73570 Actively Exploited: Patch Now
Active exploitation targets Zimbra servers via CVE-2026-73570, a high-severity flaw allowing unauthenticated RCE. Patch to v10.1.20 now.
Cryptographic Context Injection Exposes Grok Chat Data
Adversa AI reveals Cryptographic Context Injection, allowing web pages to steal Grok user data and chat prompts without user consent.
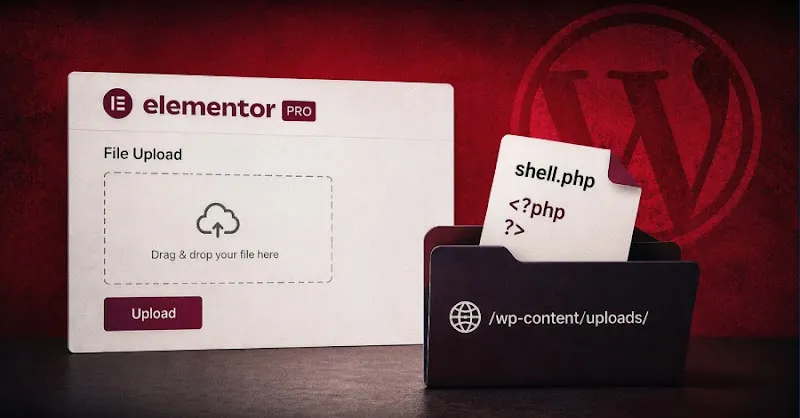
CVE-2026-32475: Elementor Pro Unauthenticated RCE Flaw
A critical flaw, CVE-2026-32475, in Elementor Pro allows unauthenticated attackers to upload PHP files and execute code, affecting versions <= 4.2.1.
Cloudflare Workers Remote Spectre Attack Reassessment & Mitigation
Cloudflare reassessed remote Spectre attacks on Workers, demonstrating a 12 bit/s leakage rate before implementing enhanced mitigations.
Chrome, Firefox, Thunderbird Updates Patch Dozens of High-Severity Flaws
Google and Mozilla release urgent updates for Chrome 151, Firefox 154, and Thunderbird 154, addressing critical and high-severity vulnerabilities including RCE.
Advertisement
MLflow CVE-2026-64849 Exploited: Cloud Credential Theft Via SSRF
Attackers exploit a critical MLflow SSRF vulnerability (CVE-2026-64849) to steal cloud credentials.
CVE-2026-33824: Microsoft IKE Double Free RCE Exploit
CISA confirms active exploitation of CVE-2026-33824 in Microsoft Internet Key Exchange (IKE) Service Extensions, enabling remote code execution.
AI Overwhelms Patching: Rapid7 Warns of Exposure Crisis
Rapid7 analysis reveals an AI-driven surge in vulnerabilities is overwhelming traditional patching, requiring a shift to exposure management.
CVE-2026-12569: Clop Exploits Windchill with Custom Web Shell
Clop ransomware group exploited CVE-2026-12569 in PTC Windchill and FlexPLM servers, deploying a custom web shell for deep data theft. Patch immediately.
CVE-2026-24301: CoSnitch Exploits Microsoft Copilot Personal
Varonis disclosed CoSnitch (CVE-2026-24301), affecting Microsoft Copilot Personal, enabling one-click data exfiltration and persistent memory poisoning.
Apple Patches iOS/iPadOS 18 and macOS: 108 Vulnerabilities Addressed
Apple has released significant security updates for iOS/iPadOS 18 and macOS, fixing 108 vulnerabilities, none exploited in the wild.
Unisoc Modem Exploit Chain: Android Takeover via Video Call
An exploit chain targeting Unisoc modems allows remote Android device takeover through a malicious video call, requiring victim interaction.
GitLab GraphQL Flaw CVE-2026-19478: Unauthenticated Project Deletion
GitLab addresses a critical GraphQL flaw (CVE-2026-19478) allowing unauthenticated attackers to delete public projects and user data on self-managed CE/EE instances.
CVE-2025-62593: Ray-Project Ray RCE Exploited In Wild
CISA confirms active exploitation of CVE-2025-62593, a critical code injection vulnerability in Ray-Project Ray allowing remote code execution. Developers are targeted.
Apple Screen Sharing Exploits: Secure Your macOS Systems Now
Critical vulnerabilities in Apple Screen Sharing are actively exploited, allowing system compromise. Learn how to secure macOS against these threats.
SharePoint RCE via CVE-2026-55040 & CVE-2026-63520: Patch Now
An AI-assisted exploit chain, leveraging CVE-2026-55040 and CVE-2026-63520, enables unauthenticated RCE on Microsoft SharePoint Server. Immediate patching is critical.
NIST Considers AI for Managing Surging Vulnerability Reports
NIST explores leveraging AI to cope with the rapidly increasing volume of cybersecurity vulnerabilities, driven partly by AI-augmented bug hunting.
CVE-2026-58231: SAP Commerce Cloud Unauthenticated RCE Flaw
SAP has patched a critical flaw, CVE-2026-58231, in Commerce Cloud Data Hub Adapter allowing unauthenticated arbitrary code execution. Immediate action is urged.
RCE Vulnerabilities in Copeland XWEB Pro & Danfoss AK-SM 800A Controllers
Claroty Team82 discovered multiple RCE vulnerabilities in Copeland XWEB Pro and Danfoss AK-SM 800A commercial refrigeration controllers.
macOS Screen Sharing Flaw Exploited to Deploy Monero Miner
The Netherlands NCSC warns that hackers are actively exploiting an authentication bypass flaw in macOS Screen Sharing to deploy cryptocurrency miners.
CVE-2026-71362: Adobe Commerce Account Takeover — Patch Now
Hackers are immediately exploiting CVE-2026-71362, a critical authorization flaw in Adobe Commerce, to take over customer accounts. Patch urgently.
CVE-2026-59310: vCenter RCE Exploited for Reverse SSH Access
A critical RCE flaw, CVE-2026-59310, in VMware vCenter Syslog Server is under active exploitation, enabling reverse SSH for persistence.
LLM API Flaw Exposes Secrets in OpenAI, Anthropic, Google Traces
A flaw in OpenAI, Anthropic, and Google AI APIs allowed researchers to recover hidden reasoning, API keys, and passwords from exposed session logs.