Advertisement
CVE-2026-12569: Clop Exploits Windchill with Custom Web Shell
Clop ransomware group exploited CVE-2026-12569 in PTC Windchill and FlexPLM servers, deploying a custom web shell for deep data theft. Patch immediately.
CVE-2026-24301: CoSnitch Exploits Microsoft Copilot Personal
Varonis disclosed CoSnitch (CVE-2026-24301), affecting Microsoft Copilot Personal, enabling one-click data exfiltration and persistent memory poisoning.
Apple Patches iOS/iPadOS 18 and macOS: 108 Vulnerabilities Addressed
Apple has released significant security updates for iOS/iPadOS 18 and macOS, fixing 108 vulnerabilities, none exploited in the wild.
Unisoc Modem Exploit Chain: Android Takeover via Video Call
An exploit chain targeting Unisoc modems allows remote Android device takeover through a malicious video call, requiring victim interaction.
GitLab GraphQL Flaw CVE-2026-19478: Unauthenticated Project Deletion
GitLab addresses a critical GraphQL flaw (CVE-2026-19478) allowing unauthenticated attackers to delete public projects and user data on self-managed CE/EE instances.
CVE-2025-62593: Ray-Project Ray RCE Exploited In Wild
CISA confirms active exploitation of CVE-2025-62593, a critical code injection vulnerability in Ray-Project Ray allowing remote code execution. Developers are targeted.
Advertisement
Apple Screen Sharing Exploits: Secure Your macOS Systems Now
Critical vulnerabilities in Apple Screen Sharing are actively exploited, allowing system compromise. Learn how to secure macOS against these threats.
SharePoint RCE via CVE-2026-55040 & CVE-2026-63520: Patch Now
An AI-assisted exploit chain, leveraging CVE-2026-55040 and CVE-2026-63520, enables unauthenticated RCE on Microsoft SharePoint Server. Immediate patching is critical.
NIST Considers AI for Managing Surging Vulnerability Reports
NIST explores leveraging AI to cope with the rapidly increasing volume of cybersecurity vulnerabilities, driven partly by AI-augmented bug hunting.
CVE-2026-58231: SAP Commerce Cloud Unauthenticated RCE Flaw
SAP has patched a critical flaw, CVE-2026-58231, in Commerce Cloud Data Hub Adapter allowing unauthenticated arbitrary code execution. Immediate action is urged.
RCE Vulnerabilities in Copeland XWEB Pro & Danfoss AK-SM 800A Controllers
Claroty Team82 discovered multiple RCE vulnerabilities in Copeland XWEB Pro and Danfoss AK-SM 800A commercial refrigeration controllers.
macOS Screen Sharing Flaw Exploited to Deploy Monero Miner
The Netherlands NCSC warns that hackers are actively exploiting an authentication bypass flaw in macOS Screen Sharing to deploy cryptocurrency miners.
CVE-2026-71362: Adobe Commerce Account Takeover — Patch Now
Hackers are immediately exploiting CVE-2026-71362, a critical authorization flaw in Adobe Commerce, to take over customer accounts. Patch urgently.
CVE-2026-59310: vCenter RCE Exploited for Reverse SSH Access
A critical RCE flaw, CVE-2026-59310, in VMware vCenter Syslog Server is under active exploitation, enabling reverse SSH for persistence.
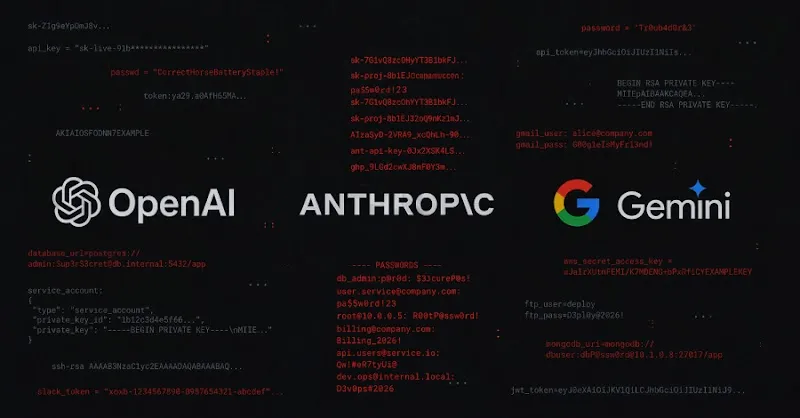
LLM API Flaw Exposes Secrets in OpenAI, Anthropic, Google Traces
A flaw in OpenAI, Anthropic, and Google AI APIs allowed researchers to recover hidden reasoning, API keys, and passwords from exposed session logs.
Belgium eID Authentication RCE via Browser Extension Flaws
Severe vulnerabilities in a key browser extension fully compromised Belgium's eID authentication trust framework, exposing citizen accounts to remote code execution.
ShieldBreak: Windows Zero-Day EoP via Microsoft Defender
Security researcher Nightmare Eclipse released 'ShieldBreak,' a Windows zero-day exploit enabling privilege escalation via Microsoft Defender.
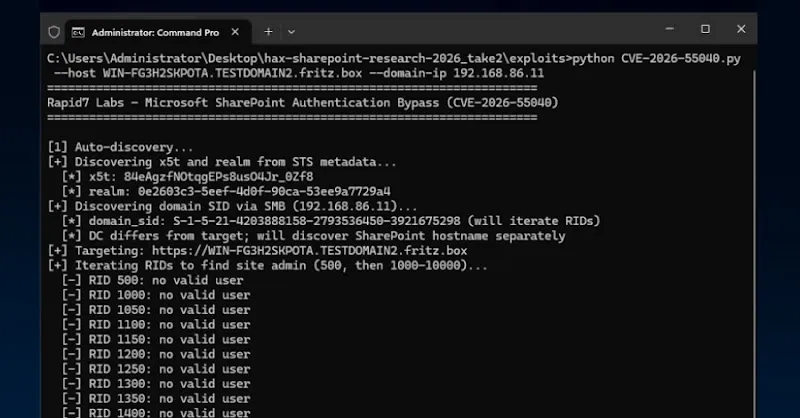
CVE-2026-55040: Critical SharePoint Auth Bypass Exploited After PoC
Attackers exploit CVE-2026-55040, a critical authentication bypass in Microsoft SharePoint, leading to data disclosure and modification.
Plug and Pwn: SYSTEM Access via Windows Plug and Play Abuse
New Plug and Pwn attacks leverage Windows Plug and Play to install vulnerable vendor software, granting attackers SYSTEM privileges via USB emulation or RDP.
CVE-2026-72898: Metabase SQL Injection Active Exploitation
CISA adds Metabase CVE-2026-72898 SQL injection to its KEV catalog, enabling unauthenticated remote attackers to gain admin access.
CVE-2026-20349: Cisco ASA/FTD DoS Vulnerability Under Active Exploit
CISA warns of active exploitation of CVE-2026-20349, a heap inspection vulnerability causing DoS in Cisco ASA and FTD devices.
CVE-2026-68820: Windows afd.sys Privilege Escalation Exploited
Microsoft addresses 398 vulnerabilities, including an actively exploited privilege escalation flaw in Windows' afd.sys component.
Microsoft August 2026 Patch Tuesday: 398 Flaws and Zero-Day
Microsoft patches 398 flaws in August 2026, including an actively exploited Windows kernel driver zero-day and four critical RCE vulnerabilities.
CVE-2026-63077: JetBrains TeamCity RCE via Deserialization
CISA adds CVE-2026-63077 to KEV, indicating active exploitation of a JetBrains TeamCity deserialization RCE vulnerability.