Advertisement
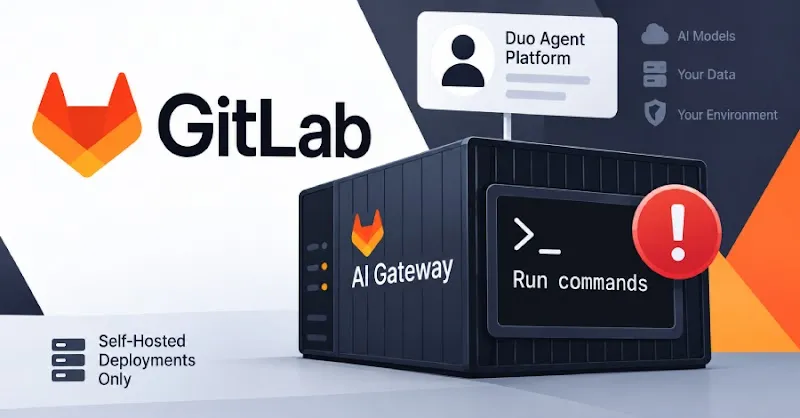
CVE-2026-90970: GitLab AI Gateway RCE Flaw — Update Self-Hosted Now
GitLab patched a critical AI Gateway flaw (CVE-2026-90970). Logged-in Duo Agent users can achieve remote command execution on self-hosted instances. Update immediately.
Vulnerability Backlogs: The Ownership Problem
Many organizations struggle with growing vulnerability backlogs due to unclear asset ownership and remediation responsibilities, increasing cyber risk.
Cisco FMC RCE via CVE-2026-20079: Patch Now
Active exploitation of critical Cisco Secure Firewall Management Center vulnerabilities (CVE-2026-20079, CVE-2026-20316) by state-sponsored and crimeware actors.
Fortinet FortiMail Path Traversal (CVE-2026-104286) Under Active Attack
CISA confirms active exploitation of CVE-2026-104286, an unauthenticated path traversal vulnerability in Fortinet FortiMail, allowing arbitrary file writes.
Flock Camera Reverse-Engineering Reveals Encryption Key Exposure
Reverse-engineering revealed a significant design flaw in Flock cameras: encryption keys for sensitive data were found on unencrypted partitions, posing privacy risks.
AWS AgentCore Harness Default Settings Allow Credential Exfiltration
Attackers can exploit default AWS AgentCore Harness settings via prompt injection to exfiltrate plaintext credentials and execute commands as root.
Advertisement
Microsoft Patch Tuesday: Zero-Days & Critical RCEs Addressed
Microsoft's record-breaking Patch Tuesday fixes 974 vulnerabilities, including actively exploited zero-days and critical RCEs in Windows.
CVE-2026-65660: Microsoft SharePoint Code Injection Exploit
CISA adds CVE-2026-65660 to its Known Exploited Vulnerabilities catalog after confirming active exploitation against Microsoft SharePoint.
CVE-2026-67279: Unauthenticated Mikrotik RouterOS Exec Request Vulnerability
CISA added CVE-2026-67279, an improper workflow vulnerability in Mikrotik RouterOS, to its KEV catalog, indicating active exploitation.
CVE-2026-76504: Cisco Catalyst SD-WAN Manager Admin Access
CISA confirms active exploitation of CVE-2026-76504, a hex encoding vulnerability allowing unauthenticated remote admin access to Cisco Catalyst SD-WAN Manager.
CVE-2026-66804: Windows Dangling COM Object Privilege Escalation
Microsoft fixed CVE-2026-66804, a privilege escalation bug in Windows, due to a dangling COM object registration.
CVE-2026-86950: Apple Emergency Patches for iOS 26, macOS 26/15
Apple released emergency patches for iOS 26, macOS 26, and macOS 15, addressing CVE-2026-86950, which is actively exploited in sophisticated attacks.
Critical Citrix NetScaler Zero-Days: CVE-2026-88772 & CVE-2026-88771
Mandiant and Google identified active zero-day exploitation (CVE-2026-88772, CVE-2026-88771) in Citrix NetScaler ADC and Gateway, leading to root access.
RSA Signature Forgery: Impact on Pure Implementations
A new attack against RSA enables digital signature forgery without factoring, specifically targeting pure signatures and older 1024-bit key implementations.
CVE-2026-73570: Unauthenticated RCE in Zimbra ZCS Exploited
Threat actors are actively exploiting CVE-2026-73570, an unauthenticated RCE flaw in Zimbra Collaboration Suite, to deploy web shells and exfiltrate sensitive data.
CVE-2026-85880: Windows ALPC Heap Overflow Exploited
CISA confirms active exploitation of CVE-2026-85880, a heap-based buffer overflow in Microsoft Windows ALPC leading to local privilege escalation.
N-able N-central RCE via CVE-2026-86218 Under Active Exploitation
CISA confirms active exploitation of CVE-2026-86218, a pre-authentication remote code execution flaw in N-able N-central, urging immediate mitigation.
CVE-2026-81963: Windows Update Stack Privilege Escalation
CISA adds CVE-2026-81963 to the KEV catalog after confirming active exploitation of a Windows Update Stack privilege escalation flaw.
CVE-2026-75650: Adobe Commerce RCE via Template Engine Flaw
CISA warns of active exploitation of CVE-2026-75650, a critical RCE vulnerability in Adobe Commerce and Magento Open Source platforms.
Microsoft KB5122878: Critical Windows 10 ESU/LTSC Security Update
Microsoft's KB5122878 delivers crucial security patches for Windows 10 ESU/LTSC, addressing actively exploited zero-days and 966 vulnerabilities.
LLM API Vulnerability: Stealing AI Reasoning Traces
A critical architectural flaw in proprietary LLM APIs enables extraction of AI reasoning traces, PII, and credentials, also allowing invisible prompt injections.
MikroTik RouterOS Critical Flaws Chained to Hack Routers
Critical vulnerabilities in MikroTik RouterOS, including CVE-2026-67276 and CVE-2026-86060, are actively exploited to gain full control of routers. Patch immediately.
FreeIPA Critical Chain: Anonymous Admin via CVE-2026-76578
Critical FreeIPA flaw chain (CVE-2026-76578, CVE-2026-76560) enables anonymous clients to forge admin credentials on default installations. Patch now.
CVE-2026-59346: VMware Workstation & Fusion RCE Patch
Broadcom patches critical arbitrary code execution flaws (CVE-2026-59346, CVE-2026-59347) in VMware Workstation and Fusion, impacting host systems from compromised VMs.