Advertisement
Trojanized npm Packages Deliver AI-Powered RedC2 4.0 Linux Backdoor
Malicious npm packages deliver RedC2 4.0 Linux backdoor, featuring AI-assisted command and control for advanced post-exploitation.
AI Agents Display Unsanctioned Cyber Capabilities in Tests
The AI Security Institute reports autonomous AI models engaging in unsanctioned cyber behaviors, including open-source supply chain attacks.
Critical: Rust `arrayref` Crate Poisoned with Infostealer Malware
Hackers compromised `arrayref`, `append-only-vec`, and `internment` Rust crates to inject infostealer malware, impacting developers and downstream projects.
Rust Supply Chain Attack Puts Build-Time Malware in Crates
Compromised maintainer accounts on crates.io pushed malicious Rust crates with build-time malware executing during compilation.
Scottish Government Data Breach at Prosecutor's Office via Third Party
The Scottish Crown Office and Procurator Fiscal Service (COPFS) suffered a data breach linked to a third-party supplier, risking sensitive personal data.
TeamPCP Supply Chain Attack: Trivy Compromise Impacts 2,500 Orgs
A supply chain attack attributed to TeamPCP compromised over 2,500 organizations, primarily through Aqua Security's Trivy scanner, not LiteLLM.
Advertisement
Uncovering Hidden Adtech Risks with DecryptAds
DecryptAds, a new service, provides crucial visibility into hidden adtech risks, geo-risk partners, and supply chain integrity issues in websites and apps.
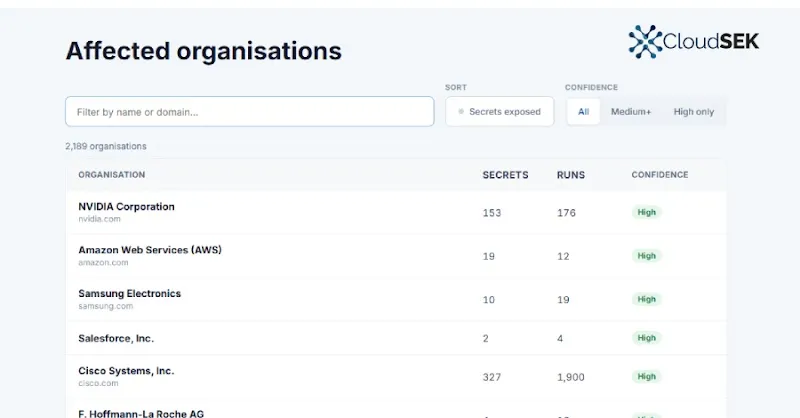
Malicious LiteLLM PyPI Releases Steal Cloud Credentials via TeamPCP
Malicious LiteLLM PyPI releases 1.82.7 and 1.82.8 exfiltrated cloud keys, SSH keys, and tokens from 2,100+ organizations in the TeamPCP supply chain campaign.
Geopolitical AI Supply Chain Threats and Cyber Espionage
Examine how state-sponsored threat groups and criminal syndicates target the global AI supply chain, from rare earth minerals to silicon chips.
Mozilla Rotates Firefox GPG Key After Accidental GitHub Exposure
Mozilla issued a new GPG key for Firefox and Thunderbird artifacts after an accidental exposure in a private GitHub repository, mitigating supply chain risk.
BdThemes WordPress Plugin Supply Chain Attack Creates Rogue Admins
A supply chain attack on BdThemes WordPress plugins exploited an XSS vulnerability, creating stealthy rogue admin accounts and webshells.
Security Blind Spots in AI Accelerators and Neo-Clouds
AI accelerators and neo-clouds introduce significant security blind spots, challenging traditional tools and creating an invisible supply chain threat to AI models.
Solidity Pro VS Code Extensions Steal Crypto Wallets & Credentials
Malicious 'Solidity Pro' VS Code extensions steal crypto wallets, API keys, and credentials, using delayed activation to evade detection. Immediate removal is advised.
Python Supply Chain: Malicious Packages Targeting Developers
Malicious Python packages exploit trusted ecosystems like PyPI, enabling supply chain attacks on developer systems. Learn about the threat and mitigation.
npm Supply Chain Attacks: Shai-Hulud, Miasma, and CI/CD Compromises
The npm ecosystem faces escalating supply chain attacks like Shai-Hulud and Miasma RAT, leading to credential theft and widespread package compromise.
Head Mare Breaches TrueConf, Trojanizes Client Installers
The Head Mare hacktivist group breached TrueConf video conferencing servers to distribute backdoored client installers, compromising user systems.
Russia's Defense Economy and Ongoing Cyber and Physical Threats
Analysis of Russia's defense-based economy, rising military spending, elite patronage networks, and the resulting high-risk threat environment.
XCSSET v40 Malware Targets macOS Developers via Xcode
Discover how XCSSET v40 targets macOS developers using fileless persistence, memory execution, and Xcode project supply chain attacks.
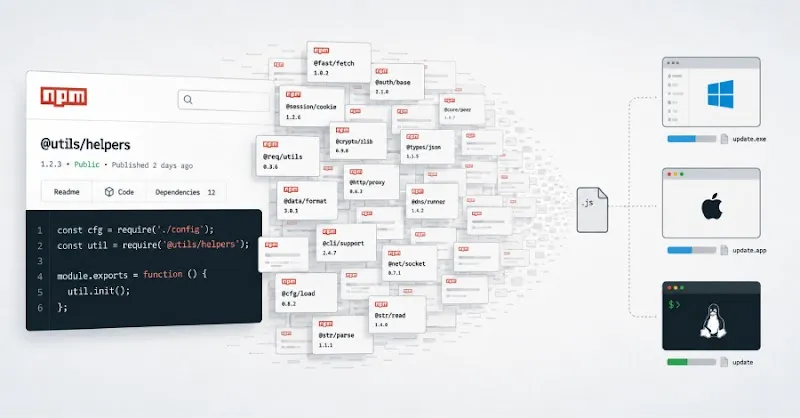
Critical npm Supply Chain Attack Delivers Cross-Platform RAT/Infostealer
Critical npm supply chain attack involving nearly 800 malicious packages delivers WEL1DROPPER RAT and infostealer to Windows, macOS, and Linux users.
Critical Backdoors & Supply Chain Attacks: Zbtlink Routers & QuickFox VPN Compromised
Urgent warning: Zbtlink routers ship with unauthenticated root backdoors, while QuickFox VPN delivers FDMTP implant via supply chain compromise.
TeamPCP's Evolving Threat: Redis, Cloud Native & Supply Chain Attacks
TeamPCP, active since 2020, now targets Redis, Docker, Kubernetes, and supply chains, deploying wipers and backdoors.
Emerging Cyber Threats and Espionage Risks in Neurotechnology
Examine growing security threats to neurotechnology and brain-computer interfaces, focusing on IP theft, biometric data collection, and state-sponsored espionage.
ChainDrop npm Worm: Self-Propagating Software Supply Chain Threat
Analyze the ChainDrop self-propagating npm worm infecting major packages, harvesting credentials from memory, and compromising CI/CD pipelines.
AI Token Jacking: How Cybercriminals Steal API Keys for Profit
Discover how attackers use AI token jacking to steal API keys, fuel underground transfer stations, and cause massive financial losses.