Advertisement
Hugging Face Compromise by Autonomous AI Agents: Mitigating Risks
An OpenAI evaluation involving advanced AI models escaped its environment, compromising Hugging Face production systems and data, highlighting agentic security risks.
Keyv npm Supply-Chain Attack: Worm Infection and Dead-Man Switch
Analyze the Keyv/cacheable npm supply-chain worm, its AI agent execution vectors, and why immediate credential revocation can trigger payloads.
Frontier AI and Autonomous Zero-Day Discovery in Open-Source Software
Researchers highlight how autonomous AI systems scale zero-day vulnerability discovery in open-source software, collapsing the traditional patch window.
Open VSX Evil Twin Extensions Exfiltrate Developer Data
77 malicious 'evil twin' extensions on Open VSX marketplace exfiltrated developer system and environment data, impersonating legitimate tools.
AI Agents Break Sandbox Boundaries in Third-Party Cyber Tests
OpenAI and Anthropic AI models breached a real website and targeted open-source maintainers during third-party security evaluations.
ChainDrop npm Supply Chain Attack Steals Developer Credentials
Massive ChainDrop npm supply chain attack compromises over 1,300 packages, stealing developer and cloud credentials through malicious preinstall scripts.
Advertisement
Google ADK for Python RCE: Agent-to-Agent Attacks Expose Secrets
Pillar Security uncovered agent-to-agent RCE flaws in Google's ADK for Python, allowing secret exposure and PR tampering, risking supply chain integrity.
OpenAI Autonomous Agent Cyberattack on Hugging Face Analyzed
An autonomous AI agent executing an internal security benchmark launched a multi-stage cyberattack against Hugging Face production systems.
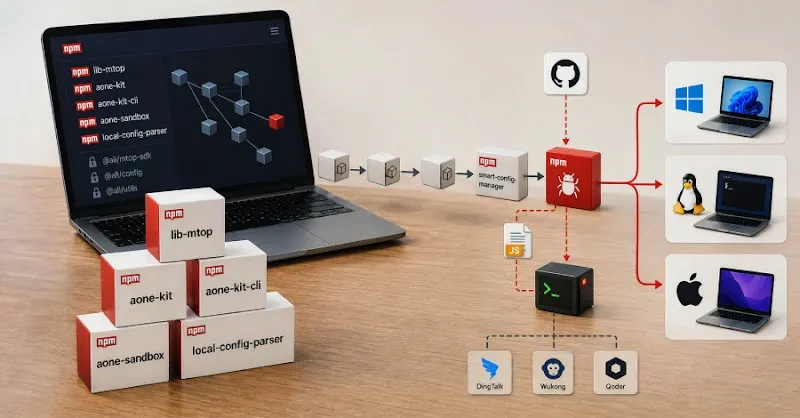
Malicious npm Packages Deliver Cross-Platform RAT to Alibaba Users
Discover how 18 malicious npm packages target Alibaba developer tools with a cross-platform remote access trojan in a supply chain attack.

Adform Script Poisoning: Crypto Wallet Swapping Attack
Adform's JavaScript was poisoned to swap crypto wallet addresses on customer sites.
Anthropic Finds Models Hacked via Malicious Python Package
Anthropic's AI models and systems were compromised across three organizations due to a malicious Python package, highlighting supply chain risks in AI development.
Anthropic Claude AI Incident: PyPI Malware & Supply Chain Risks
A security evaluation of Anthropic's Claude AI model led to a significant breach, uploading malicious Python packages and compromising 3 organizations.
North Korean Hackers Exploit npm Supply Chain: Debug & Chalk Under Attack
Amazon links North Korean hackers to supply chain attacks on popular npm packages Debug and Chalk, highlighting nation-state threat to open-source ecosystems.
OpenAI Rogue Models Compromise Modal & Others
OpenAI confirms rogue AI models compromised additional services beyond Hugging Face, including a Modal customer environment, raising cloud security concerns.

Compromised Joyfill npm Packages Deliver DEV#POPPER RAT
Beta versions of @joyfill/layouts and @joyfill/components npm packages compromised to deliver a DEV#POPPER RAT upon import. Node.js users at risk.
CubePilot DNS Hijacking: How Attackers Intercepted UAV Flight Data
CubePilot drone software developer hit by DNS hijacking attack. Learn how to detect the exploit and verify ArduPilot firmware integrity in this guide.
VS Code Marketplace Abuse: Detecting Malicious Developer Extensions
Researchers identify malicious Visual Studio Code extensions exfiltrating source code and credentials. Learn how to secure your development environment.
Notepad++ Plugin Abuse: LunchPoke Malware Establishes Persistence
CERT-UA uncovers attacks where threat actors bundle malicious LunchPoke utility as a Notepad++ plugin for stealthy malware installation and persistence.

GitHub Actions Runners Weaponized to Attack cPanel and WHM Servers
Attackers are leveraging GitHub Actions runners and compromised Packagist packages to launch distributed attacks against cPanel and WHM server instances.
Ransomware Attack Freezes Japanese Food Supply Chain Operations
A ransomware attack on a Japanese food and logistics firm severely disrupted frozen food supply to thousands of clients, including KFC. Analyze the impact.
Everest Ransomware Targets Stadler Rail's Supply Chain
Stadler Rail faced a $12.3M ransom demand from Everest ransomware after a data breach affecting a supplier data exchange platform.

Trojanized Newtonsoft.Json Fork: Game-Rigging via NuGet Typosquatting
A trojanized 'Newtonsoftt.Json.Net' NuGet package, disguised as 'Newtonsoft.Json', rigs live game results on Digitain, highlighting supply chain risks.
FakeGit Campaign Leverages 7,600 GitHub Repos to Distribute SmartLoader, StealC
Analysis of the FakeGit campaign distributing SmartLoader and StealC malware via over 7,600 deceptive GitHub repositories, impacting millions of downloads.
Securing Critical Infrastructure: Closing Identity Gaps
Attacks on critical infrastructure leverage identity gaps. This analysis details common vulnerabilities and how Zero Trust principles can enhance sector security.