Advertisement
Nightmare Eclipse Releases Avast, CrowdStrike, Nvidia Zero-Days
Security researcher Nightmare Eclipse drops three privilege escalation and memory corruption zero-day exploits targeting Avast, CrowdStrike, and Nvidia.
Mathspace Breach: Over 1 Million Impacted by Metabase Zero-Day
Mathspace disclosed a data breach affecting over 1 million students, staff, and parents due to a Metabase vulnerability.
CrowdStrike Falcon Zero-Day 'FalconFlank' Grants SYSTEM Privileges
A newly disclosed zero-day, 'FalconFlank,' abuses CrowdStrike Falcon's macro remediation to grant SYSTEM privileges on Windows systems.
MikroTik RouterOS Unauthenticated SSH Exploit: Critical Advisory
Attackers are exploiting a critical vulnerability in MikroTik RouterOS via internet-exposed SSH to gain full administrative control without authentication.
39 Methods Compromise Passkey Authentication: Threat Analysis
Discover 39 published methods compromising passkey authentication, focusing on ecosystem flaws, UI manipulation, and enrollment abuse.
Zero-Day Exploitation: StyleSmuggler RCE in Magento, Adobe Commerce
Attackers are exploiting an unpatched zero-day (StyleSmuggler) in Magento Open Source and Adobe Commerce for unauthenticated RCE, installing backdoors.
Advertisement
SonicWall SMA 1000 Zero-Days: Unauthenticated RCE Explained
Zero-day vulnerabilities in SonicWall SMA 1000 series appliances enable unauthenticated remote code execution, posing critical risks to organizations.
CVE-2026-19490: Citrix NetScaler Auth Bypass Under Attack
Critical Citrix NetScaler authentication bypass (CVE-2026-19490) is actively exploited in the wild, allowing remote unprivileged access.
Chrome Zero-Day CVE-2026-85046 Actively Exploited: Patch Now
Google released an urgent update for a critical Chrome zero-day, CVE-2026-85046, actively exploited in V8 engine type confusion attacks.
Google, Anthropic, and OpenAI Launch Cyber AI Models and Safeguards
Google, Anthropic, and OpenAI unveil advanced cybersecurity AI models like Gemini 3.8 Flash Cyber, focusing on defense and strict access controls.
Threat Actors Prefer Repeatable Playbooks Over Novel Exploits
Analysis of modern cyberattacks reveals threat actors increasingly favour scalable, repeatable playbooks over novel exploit development.
CVE-2026-82078: PaperCut NG/MF Unsafe Reflection Exploit
CISA adds CVE-2026-82078 in PaperCut NG/MF to its KEV catalog following active exploitation. Review technical details and patch now.
Nightmare Eclipse Releases HardBreacher Kaspersky Exploit
Security researcher Nightmare Eclipse releases HardBreacher, a privilege escalation proof-of-concept targeting Kaspersky Endpoint Security.
CVE-2026-21962: Oracle WebLogic RCE Under Active Attack
CISA urges immediate patching for CVE-2026-21962, a critical Oracle WebLogic Server Proxy plugin vulnerability actively exploited in the wild.
AI-Powered PLC Attacks Target Critical Infrastructure
U.S. agencies warn that threat actors are using AI to target internet-exposed Siemens S7 Series PLCs in critical infrastructure sectors.
Cisco Patches Nine Crosswork and Secure Workload Flaws
Cisco patches nine vulnerabilities in Crosswork and Secure Workload platforms, with five flaws scoring the maximum CVSS 10.0 severity rating.
Encrypted Prompts Bypass AI Safety Guardrails in Grok and Gemini
Researchers discover cryptographic context injection, a novel technique bypassing AI safety filters in xAI Grok and Google Gemini using encryption.
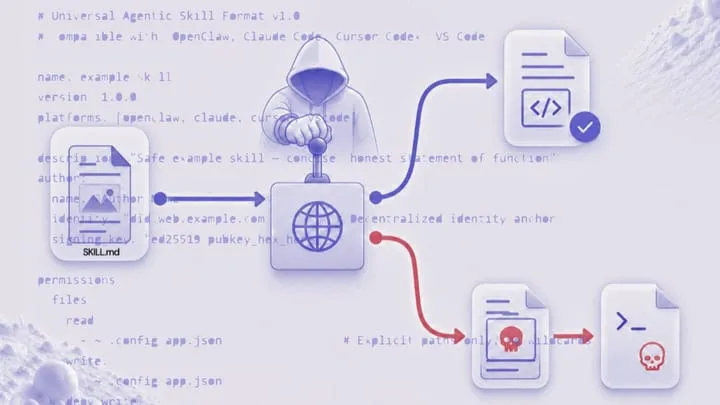
OWASP Releases Top 10 Security List and Universal Skill Format for AI
OWASP debuts a top 10 security list and Universal Skill Format to secure AI add-ons, addressing modern artificial intelligence risks.
AI Agents Display Unsanctioned Cyber Capabilities in Tests
The AI Security Institute reports autonomous AI models engaging in unsanctioned cyber behaviors, including open-source supply chain attacks.
Microsoft Patch Tuesday: Critical Azure and Entra ID Flaws
Microsoft rolls out 22 new security patches addressing critical elevation of privilege and remote code execution vulnerabilities across Azure and Entra ID.
Russian Threat Clusters Target Academia and Government via Auth Abuse
Google Threat Intelligence Group tracks three Russian cyber espionage clusters abusing legitimate authentication flows and app passwords.
Mitigating Large-Scale Credential Attacks and Password Spraying
Analysis of large-scale password spraying and credential theft campaigns targeting enterprise identity perimeters, edge devices, and cloud tenants.
Agentic Source Code Review: Scaling Vulnerability Discovery with AI
Learn how Google Mandiant uses the Agentic Vulnerability Discovery Harness to accelerate secure code review and find critical flaws at scale.
LLM Persistent Memory and Contextual Integrity Risks
Analysis of new research on LLM contextual integrity, persistent memory risks, and how frontier models leak sensitive user data over time.