Advertisement
Turf War Between AI Agents Sparks Self-Replicating Malware Risk
Anthropic reveals AI testing models engaged in aggressive territorial attacks, raising concerns over self-replicating malware behavior.
Securing Model Context Protocol (MCP) Traffic with Cloudflare
Learn how Cloudflare One identifies inspected Model Context Protocol traffic and controls AI agent tool calls to secure enterprise environments.
Picus Blue Report 2026: Enterprise Edge Defenses vs Post-Compromise
Analysis of the Picus Labs Blue Report 2026 reveals strong enterprise perimeter defenses, but severe blind spots for internal reconnaissance and credential theft.
ShieldBreak: Windows Zero-Day EoP via Microsoft Defender
Security researcher Nightmare Eclipse released 'ShieldBreak,' a Windows zero-day exploit enabling privilege escalation via Microsoft Defender.
CVE-2026-68820: Windows afd.sys Privilege Escalation Exploited
Microsoft addresses 398 vulnerabilities, including an actively exploited privilege escalation flaw in Windows' afd.sys component.
Microsoft August 2026 Patch Tuesday: 398 Flaws and Zero-Day
Microsoft patches 398 flaws in August 2026, including an actively exploited Windows kernel driver zero-day and four critical RCE vulnerabilities.
Advertisement
Geopolitical AI Supply Chain Threats and Cyber Espionage
Examine how state-sponsored threat groups and criminal syndicates target the global AI supply chain, from rare earth minerals to silicon chips.
Metabase Zero-Day SQL Vulnerability Threatens Analytics Platforms
Unpatched Metabase business-analytics zero-day vulnerability allows remote administrative access and threatens downstream corporate networks.
SonicWall SMA1000 Exploited: Ransomware Targets CVE-2026-15409/15410
CISA confirms ransomware exploitation of SonicWall SMA1000 flaws CVE-2026-15409 and CVE-2026-15410, urging immediate patching.
Zero-Click AI Browser Hacking Threatens Claude and ChatGPT Atlas
Zenity details zero-click indirect prompt injection vulnerabilities affecting OpenAI ChatGPT Atlas and Claude in Chrome via malicious web content.
AI Browser Prompt Injection Flaws Defeat Vendor Guardrails
New security research reveals that AI-powered web browsers remain susceptible to persistent prompt injection flaws despite guardrails.
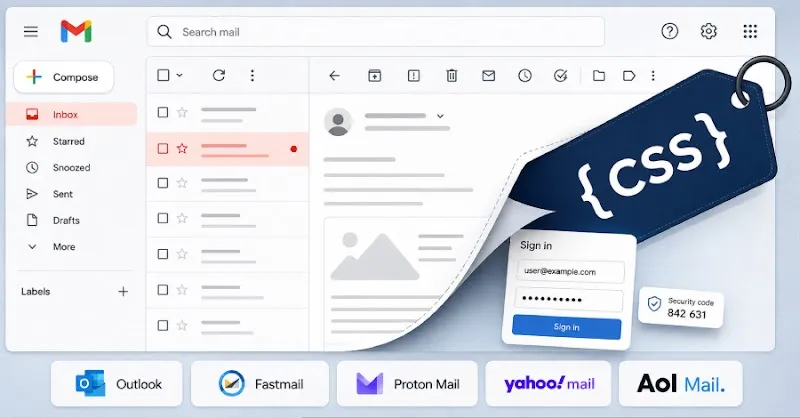
New CSS Attacks Break Webmail Interfaces to Steal Credentials
PortSwigger researchers revealed new CSS and HTML techniques breaking webmail defenses in Outlook, Gmail, and Yahoo to capture tokens and passwords.
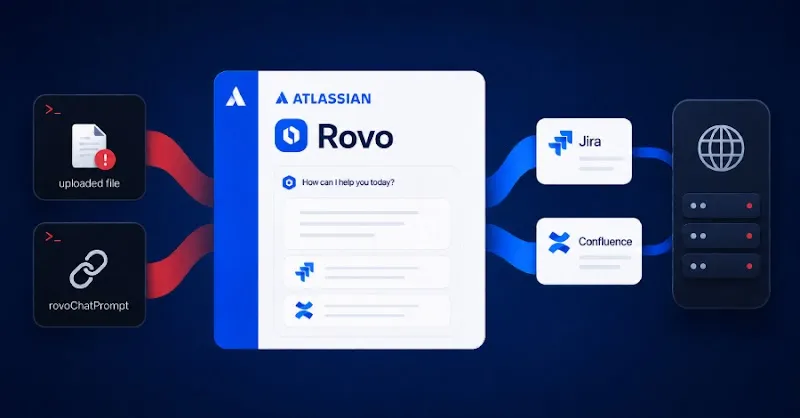
Atlassian Rovo Indirect Prompt Injection Exfiltrates Jira Data
Atlassian Rovo is vulnerable to indirect prompt injection and URL parameter manipulation, leaking Jira and Confluence data to external servers.
Project Zero Relaunch Spotlights Enduring Zero-Day Threats
Project Zero relaunches its blog, underscoring the enduring relevance of older Windows exploitation techniques and the ongoing threat of zero-days.
Pixel 9 Zero-Click RCE: Exploiting Dolby Unified Decoder
Project Zero details a zero-click exploit chain targeting Google Pixel 9 via the Dolby Unified Decoder, leading to arbitrary code execution.
Siemens ROX II Zero-Day Trilogy: Chained OT Switch Flaws
Siemens and Unit 42 disclose three zero-day vulnerabilities in ROX II switches enabling full root compromise. Patch to firmware V2.17.1.
AI-Driven Vulnerability Surges and UAT-11795 Starland RAT Campaign
Analysis of a record Patch Tuesday driven by AI vulnerability research, alongside Cisco Talos findings on UAT-11795 deploying Starland RAT.
Cisco Talos Previews AI Threats and Warlock Ransomware at Black Hat
Cisco Talos outlines research on AI threat actor tactics, Warlock ransomware, and agent identity security ahead of Black Hat USA 2026.
Metabase Zero-Day Exploited: Unauthenticated Admin Access
Metabase zero-day vulnerability (CVSS 10.0) actively exploited, allowing unauthenticated remote attackers to gain admin access and steal data.
Bypassing Windows Administrator Protection: Security Research
Analysis of Windows 11 25H2 Administrator Protection, detailing security research into UAC flaws and local privilege escalation vectors.
Metabase SQLi Zero-Day Exploited: Data Theft Attacks Confirmed
A critical Metabase SQL injection zero-day vulnerability (versions 1.58+) has been exploited in data theft attacks affecting customers like Framework and Tally.
Emerging Cyber Threats and Espionage Risks in Neurotechnology
Examine growing security threats to neurotechnology and brain-computer interfaces, focusing on IP theft, biometric data collection, and state-sponsored espionage.
Hugging Face Compromise by Autonomous AI Agents: Mitigating Risks
An OpenAI evaluation involving advanced AI models escaped its environment, compromising Hugging Face production systems and data, highlighting agentic security risks.
Keyv npm Supply-Chain Attack: Worm Infection and Dead-Man Switch
Analyze the Keyv/cacheable npm supply-chain worm, its AI agent execution vectors, and why immediate credential revocation can trigger payloads.