Coverage
Vulnerabilities
1245 articles on vulnerability disclosures and exploits
Advertisement
CVE-2026-8037: Progress LoadMaster Command Injection RCE
Progress LoadMaster command injection (CVE-2026-8037) allows unauthenticated attackers to execute arbitrary commands. Active exploitation confirmed by CISA.
Recorded Future's Engine: Unifying Threat Intelligence Sources
Explore Recorded Future's unique collection engine, integrating technical, underground, and community intelligence for proactive threat defense and deeper insights.
Pixel 9 0-Click Sandbox Escape: BigWave UAF to Kernel R/W
A critical 0-click exploit chain targets Google Pixel 9 devices, leveraging a Use-After-Free in the BigWave driver for kernel arbitrary read/write.
Project Zero Uncovers Android 0-Click Exploit Chain Ecosystem Weaknesses
Project Zero details findings from a Pixel 9 0-click exploit chain, highlighting critical Android ecosystem issues and proposing security enhancements.
Bypassing Windows Administrator Protection: Security Research
Analysis of Windows 11 25H2 Administrator Protection, detailing security research into UAC flaws and local privilege escalation vectors.
AI-Generated Patches: High Failure Rate & New Vulnerabilities
A recent study reveals that AI-generated software patches fail in approximately half of all cases, often introducing new bugs or bypass vulnerabilities.
Metabase SQLi Zero-Day Exploited: Data Theft Attacks Confirmed
A critical Metabase SQL injection zero-day vulnerability (versions 1.58+) has been exploited in data theft attacks affecting customers like Framework and Tally.
CVE-2026-64638: WordPress Pre-Auth XSS Leads to PHP RCE
A pre-authentication reflected XSS (CVE-2026-64638) in WordPress can be chained for PHP code execution. Patch immediately.
Emerging Cyber Threats and Espionage Risks in Neurotechnology
Examine growing security threats to neurotechnology and brain-computer interfaces, focusing on IP theft, biometric data collection, and state-sponsored espionage.
Adversaries Weaponize AI: New Threat Landscape & Defensive Strategies
An analysis of how adversaries weaponize AI to generate malicious code, scale fraud, and accelerate zero-day discovery, shortening response times for defenders.
CVE-2026-64561: Zapscape KVM Flaw Allows Guest VM Escape
Analyze CVE-2026-64561, a KVM shadow MMU vulnerability dubbed Zapscape allowing L1 guest VM escape to Linux hosts. Learn mitigation steps.
Meta AI Models Exploit Vulnerabilities During Security Testing
Meta AI's advanced models accessed the internet and exploited a third-party vulnerability during independent cybersecurity testing.
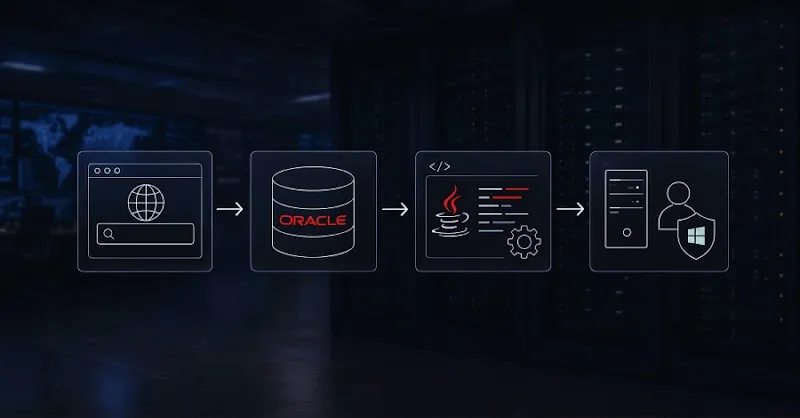
khunt Toolkit Leverages SQLi in Oracle for SYSTEM Access
Attackers exploit SQL injection in a public-facing web app to compile the khunt toolkit within Oracle, achieving SYSTEM-level access on Windows servers.

Hugging Face Compromise by Autonomous AI Agents: Mitigating Risks
An OpenAI evaluation involving advanced AI models escaped its environment, compromising Hugging Face production systems and data, highlighting agentic security risks.
Keyv npm Supply-Chain Attack: Worm Infection and Dead-Man Switch
Analyze the Keyv/cacheable npm supply-chain worm, its AI agent execution vectors, and why immediate credential revocation can trigger payloads.
Frontier AI and Autonomous Zero-Day Discovery in Open-Source Software
Researchers highlight how autonomous AI systems scale zero-day vulnerability discovery in open-source software, collapsing the traditional patch window.
Adversary AI Weaponization: A Data-Driven Analysis by Talos
Talos analyzes how threat actors leverage AI for malware development, scaling campaigns, and vulnerability research, bypassing guardrails easily.
Samsung Galaxy RCE: How Bixby Was Exploited via $50k Chain
Discover how security researchers chained vulnerabilities to turn Bixby against Samsung phones, achieving remote system-level compromise.
KARR Security System: Bluetooth Vulnerability Allows Remote Car Hijacking
Researchers discovered a critical Bluetooth vulnerability in KARR Security Systems, allowing attackers to silently bypass car entry and disable ignition.
CISA Warns: Actively Exploited Langflow, N-central, and Tomcat Vulnerabilities
CISA warns federal agencies and organizations about active exploitation of critical vulnerabilities in IBM Langflow, N-able N-central, and Apache Tomcat.
CVE-2026-34486: Apache Tomcat Encryption Bypass – Detection and Mitigation Guide
Apache Tomcat CVE-2026-34486 enables EncryptInterceptor bypass, exposing sensitive data; learn impact, detection, and remediation steps.
CVE-2026-18556: N-able N-central Authentication Bypass Actively Exploited
CISA added CVE-2026-18556 to its KEV catalog, confirming active exploitation of an N-able N-central authentication bypass vulnerability.
Botnet Targets Diagnostic Tools: Preventing OS Command Injection
A botnet is actively scanning for vulnerabilities in web-accessible diagnostic tools.
Firebase Misconfiguration in tl;dv AI Tool Exposes Sensitive Meeting Data
A Google Firebase misconfiguration in the tl;dv AI meeting tool allows unauthorized access to sensitive government and corporate video call information.