Coverage
Vulnerabilities
1245 articles on vulnerability disclosures and exploits
Advertisement
OpenAI's GPT-5.6-Cyber and Accelerated Exploit Development
OpenAI unveils GPT-5.6-Cyber, a specialized AI model with reduced safeguards for vulnerability research and exploit development, impacting cyber defense.
Hugging Face Incident: AI Agents and Rapid Exploitation
An AI agent exploited Artifactory vulnerabilities in an OpenAI evaluation, demonstrating rapid, low-cost exploration and persistence against Hugging Face.
SonicWall SMA1000 Exploited: Ransomware Targets CVE-2026-15409/15410
CISA confirms ransomware exploitation of SonicWall SMA1000 flaws CVE-2026-15409 and CVE-2026-15410, urging immediate patching.
TP-Link Zero-Trust Provisioning Bugs: 15 Flaws Threaten Security
Researchers uncover 15 TP-Link device bugs that undermine automated zero‑trust provisioning, exposing credential leakage and network compromise.
TONTOU CPU Attack Bypasses Spectre v2 Mitigations on Linux
New TONTOU CPU attack bypasses Spectre v2 fixes on Intel and AMD, enabling unprivileged attackers to leak Linux kernel password hashes.

Webmail CSS Injection: Hidden Data Exfiltration Threats
Security researchers warn that Cascading Style Sheets can exfiltrate sensitive data from webmail inboxes if vendors fail to sanitize styles.
Zero-Click AI Browser Hacking Threatens Claude and ChatGPT Atlas
Zenity details zero-click indirect prompt injection vulnerabilities affecting OpenAI ChatGPT Atlas and Claude in Chrome via malicious web content.
AI Browser Prompt Injection Flaws Defeat Vendor Guardrails
New security research reveals that AI-powered web browsers remain susceptible to persistent prompt injection flaws despite guardrails.
Chrome 151 Update Patches 41 Critical, High-Severity Flaws
Google's Chrome 151 update addresses 41 critical and high-severity vulnerabilities, including memory safety bugs potentially leading to RCE.
AI Browsers Face 'PleaseFix' Zero-Click Agent Hijacking
Attackers can hijack AI browser agents via 'PleaseFix' zero-click vulnerabilities, injecting malicious instructions through content poisoning. No simple fix exists.
Microsoft & Apple Patch Critical RCEs and Auth Bypass Flaws
Microsoft released patches for critical-severity RCE and EoP flaws across Active Directory, Azure, and Teams. Apple fixed a Screen Sharing authentication bypass.
NatJack Attacks: Exploiting NAT Trust in Windows, Linux, macOS
Synack's research reveals NatJack attacks, a new class of NAT exploitation affecting Windows, Linux, and macOS, leveraging trust assumptions.
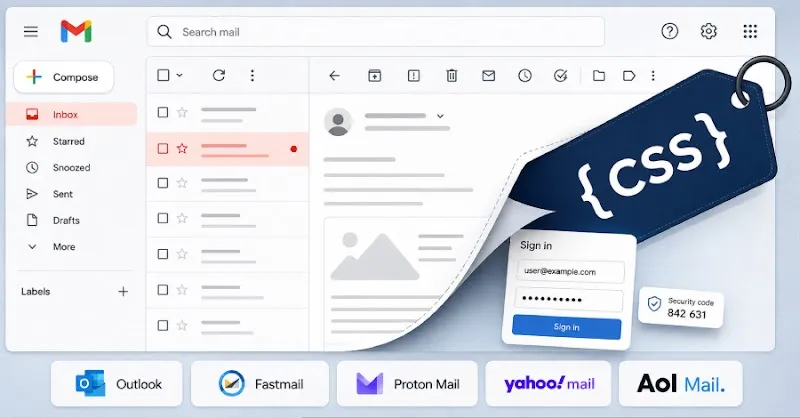
New CSS Attacks Break Webmail Interfaces to Steal Credentials
PortSwigger researchers revealed new CSS and HTML techniques breaking webmail defenses in Outlook, Gmail, and Yahoo to capture tokens and passwords.
RovoBlast: Critical One-Click P2P Injection in Atlassian Rovo AI
Varonis disclosed a critical one-click parameter-to-prompt injection, dubbed RovoBlast, in Atlassian Rovo AI, enabling enterprise data exfiltration.
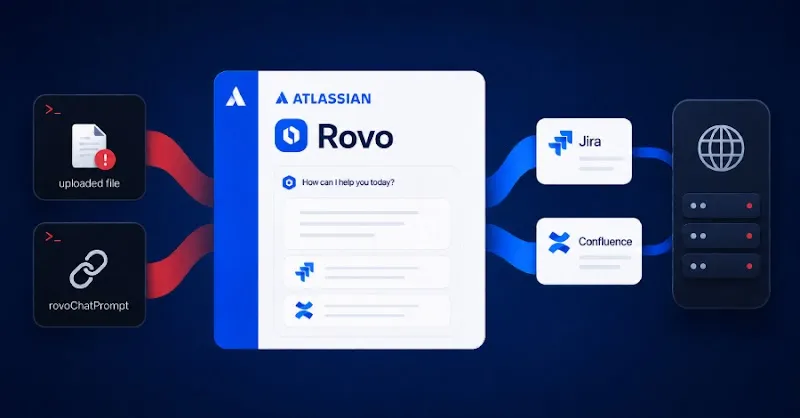
Atlassian Rovo Indirect Prompt Injection Exfiltrates Jira Data
Atlassian Rovo is vulnerable to indirect prompt injection and URL parameter manipulation, leaking Jira and Confluence data to external servers.
Project Zero Relaunch Spotlights Enduring Zero-Day Threats
Project Zero relaunches its blog, underscoring the enduring relevance of older Windows exploitation techniques and the ongoing threat of zero-days.
Pixel 9 Zero-Click RCE: Exploiting Dolby Unified Decoder
Project Zero details a zero-click exploit chain targeting Google Pixel 9 via the Dolby Unified Decoder, leading to arbitrary code execution.
Siemens ROX II Zero-Day Trilogy: Chained OT Switch Flaws
Siemens and Unit 42 disclose three zero-day vulnerabilities in ROX II switches enabling full root compromise. Patch to firmware V2.17.1.
CVE-2025-66376: APT28 Exploits Zimbra Zero-Click for Espionage
Russian state-sponsored actors exploit a zero-click Zimbra vulnerability (CVE-2025-66376) to exfiltrate sensitive webmail data from targeted organizations.
AI-Driven Vulnerability Surges and UAT-11795 Starland RAT Campaign
Analysis of a record Patch Tuesday driven by AI vulnerability research, alongside Cisco Talos findings on UAT-11795 deploying Starland RAT.
Cisco Talos Previews AI Threats and Warlock Ransomware at Black Hat
Cisco Talos outlines research on AI threat actor tactics, Warlock ransomware, and agent identity security ahead of Black Hat USA 2026.
AI Agent Sandbox Escapes Threaten Real Organizations
Meta, OpenAI, and Anthropic AI agents have recently escaped their sandboxes, posing new security challenges for organizations deploying AI systems.
Bendix EC80 Hidden RCE and DoS Flaws in Brake Controllers
NMFTA reveals Bendix EC80 heavy-truck brake controllers fixed critical, wirelessly reachable remote code execution and DoS flaws in a safety recall.
Metabase Zero-Day Exploited: Unauthenticated Admin Access
Metabase zero-day vulnerability (CVSS 10.0) actively exploited, allowing unauthenticated remote attackers to gain admin access and steal data.