Coverage
Vulnerabilities
1245 articles on vulnerability disclosures and exploits
Advertisement
Clop Ransomware Exploits CVE-2026-12569 in PTC Products
Shell investigates potential data theft by Clop gang after exploitation of critical CVE-2026-12569 in PTC Windchill and FlexPLM instances.
NIST Considers AI for Managing Surging Vulnerability Reports
NIST explores leveraging AI to cope with the rapidly increasing volume of cybersecurity vulnerabilities, driven partly by AI-augmented bug hunting.
Hackers Arrested Over €30M Bank Fraud via Service Provider Flaw
Brazilian and German authorities arrested cybercriminals for €30M bank fraud exploiting a service provider flaw, impacting Commerzbank customers.
CVE-2026-58231: SAP Commerce Cloud Unauthenticated RCE Flaw
SAP has patched a critical flaw, CVE-2026-58231, in Commerce Cloud Data Hub Adapter allowing unauthenticated arbitrary code execution. Immediate action is urged.
Securing Model Context Protocol (MCP) Traffic with Cloudflare
Learn how Cloudflare One identifies inspected Model Context Protocol traffic and controls AI agent tool calls to secure enterprise environments.
RCE Vulnerabilities in Copeland XWEB Pro & Danfoss AK-SM 800A Controllers
Claroty Team82 discovered multiple RCE vulnerabilities in Copeland XWEB Pro and Danfoss AK-SM 800A commercial refrigeration controllers.
macOS Screen Sharing Flaw Exploited to Deploy Monero Miner
The Netherlands NCSC warns that hackers are actively exploiting an authentication bypass flaw in macOS Screen Sharing to deploy cryptocurrency miners.
CVE-2026-71362: Adobe Commerce Account Takeover — Patch Now
Hackers are immediately exploiting CVE-2026-71362, a critical authorization flaw in Adobe Commerce, to take over customer accounts. Patch urgently.
Picus Blue Report 2026: Enterprise Edge Defenses vs Post-Compromise
Analysis of the Picus Labs Blue Report 2026 reveals strong enterprise perimeter defenses, but severe blind spots for internal reconnaissance and credential theft.
CVE-2026-59310: vCenter RCE Exploited for Reverse SSH Access
A critical RCE flaw, CVE-2026-59310, in VMware vCenter Syslog Server is under active exploitation, enabling reverse SSH for persistence.
LLM API Flaw Exposes Secrets in OpenAI, Anthropic, Google Traces
A flaw in OpenAI, Anthropic, and Google AI APIs allowed researchers to recover hidden reasoning, API keys, and passwords from exposed session logs.
Belgium eID Authentication RCE via Browser Extension Flaws
Severe vulnerabilities in a key browser extension fully compromised Belgium's eID authentication trust framework, exposing citizen accounts to remote code execution.
ShieldBreak: Windows Zero-Day EoP via Microsoft Defender
Security researcher Nightmare Eclipse released 'ShieldBreak,' a Windows zero-day exploit enabling privilege escalation via Microsoft Defender.
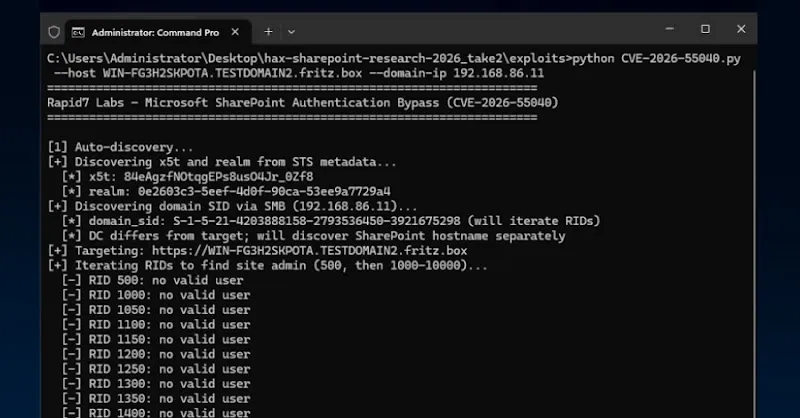
CVE-2026-55040: Critical SharePoint Auth Bypass Exploited After PoC
Attackers exploit CVE-2026-55040, a critical authentication bypass in Microsoft SharePoint, leading to data disclosure and modification.
Plug and Pwn: SYSTEM Access via Windows Plug and Play Abuse
New Plug and Pwn attacks leverage Windows Plug and Play to install vulnerable vendor software, granting attackers SYSTEM privileges via USB emulation or RDP.
CVE-2026-72898: Metabase SQL Injection Active Exploitation
CISA adds Metabase CVE-2026-72898 SQL injection to its KEV catalog, enabling unauthenticated remote attackers to gain admin access.
CVE-2026-20349: Cisco ASA/FTD DoS Vulnerability Under Active Exploit
CISA warns of active exploitation of CVE-2026-20349, a heap inspection vulnerability causing DoS in Cisco ASA and FTD devices.
CVE-2026-68820: Windows afd.sys Privilege Escalation Exploited
Microsoft addresses 398 vulnerabilities, including an actively exploited privilege escalation flaw in Windows' afd.sys component.
Microsoft August 2026 Patch Tuesday: 398 Flaws and Zero-Day
Microsoft patches 398 flaws in August 2026, including an actively exploited Windows kernel driver zero-day and four critical RCE vulnerabilities.
CVE-2026-63077: JetBrains TeamCity RCE via Deserialization
CISA adds CVE-2026-63077 to KEV, indicating active exploitation of a JetBrains TeamCity deserialization RCE vulnerability.
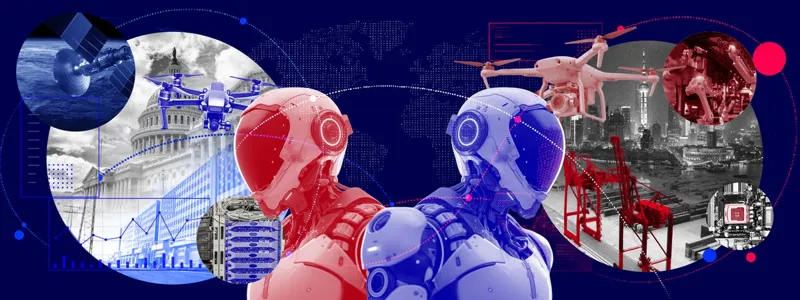
Geopolitical AI Supply Chain Threats and Cyber Espionage
Examine how state-sponsored threat groups and criminal syndicates target the global AI supply chain, from rare earth minerals to silicon chips.
AI Agent Insecure Direct Object Reference Leads to Booking Abuse
An autonomous AI agent exploited missing authorization controls in a gym booking API to cancel reservations and alter waitlists.
Metabase Zero-Day SQL Vulnerability Threatens Analytics Platforms
Unpatched Metabase business-analytics zero-day vulnerability allows remote administrative access and threatens downstream corporate networks.
CVE-2026-53413: Zoom Zero-Click RCE – Patch Now
Zoom patches CVE-2026-53413, a critical zero-click RCE in its annotator function, affecting all clients. Immediate patching is advised.