Coverage
Vulnerabilities
1245 articles on vulnerability disclosures and exploits
Advertisement
Microsoft Patch Tuesday: Critical Azure and Entra ID Flaws
Microsoft rolls out 22 new security patches addressing critical elevation of privilege and remote code execution vulnerabilities across Azure and Entra ID.
CVE-2026-72529: Critical RCE in TrueConf Server via Missing Auth
CISA warns of active exploitation of CVE-2026-72529 in TrueConf Server, allowing remote attackers to execute arbitrary scripts via port 4307/TCP.
CVE-2026-72530: TrueConf Server Remote Code Execution
CISA confirms active exploitation of CVE-2026-72530, a TrueConf Server code injection flaw leading to remote code execution. Immediate patching is critical.
Russian Threat Clusters Target Academia and Government via Auth Abuse
Google Threat Intelligence Group tracks three Russian cyber espionage clusters abusing legitimate authentication flows and app passwords.
Zimbra CVE-2026-73570 Actively Exploited: Patch Now
Active exploitation targets Zimbra servers via CVE-2026-73570, a high-severity flaw allowing unauthenticated RCE. Patch to v10.1.20 now.
Cryptographic Context Injection Exposes Grok Chat Data
Adversa AI reveals Cryptographic Context Injection, allowing web pages to steal Grok user data and chat prompts without user consent.
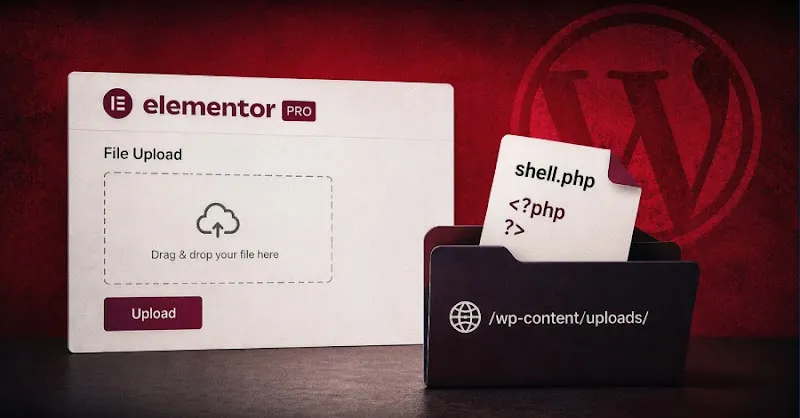
CVE-2026-32475: Elementor Pro Unauthenticated RCE Flaw
A critical flaw, CVE-2026-32475, in Elementor Pro allows unauthenticated attackers to upload PHP files and execute code, affecting versions <= 4.2.1.
Cloudflare Workers Remote Spectre Attack Reassessment & Mitigation
Cloudflare reassessed remote Spectre attacks on Workers, demonstrating a 12 bit/s leakage rate before implementing enhanced mitigations.
Chrome, Firefox, Thunderbird Updates Patch Dozens of High-Severity Flaws
Google and Mozilla release urgent updates for Chrome 151, Firefox 154, and Thunderbird 154, addressing critical and high-severity vulnerabilities including RCE.
MLflow CVE-2026-64849 Exploited: Cloud Credential Theft Via SSRF
Attackers exploit a critical MLflow SSRF vulnerability (CVE-2026-64849) to steal cloud credentials.
CVE-2026-33824: Microsoft IKE Double Free RCE Exploit
CISA confirms active exploitation of CVE-2026-33824 in Microsoft Internet Key Exchange (IKE) Service Extensions, enabling remote code execution.
Mitigating Large-Scale Credential Attacks and Password Spraying
Analysis of large-scale password spraying and credential theft campaigns targeting enterprise identity perimeters, edge devices, and cloud tenants.
AI Overwhelms Patching: Rapid7 Warns of Exposure Crisis
Rapid7 analysis reveals an AI-driven surge in vulnerabilities is overwhelming traditional patching, requiring a shift to exposure management.
CVE-2026-12569: Clop Exploits Windchill with Custom Web Shell
Clop ransomware group exploited CVE-2026-12569 in PTC Windchill and FlexPLM servers, deploying a custom web shell for deep data theft. Patch immediately.
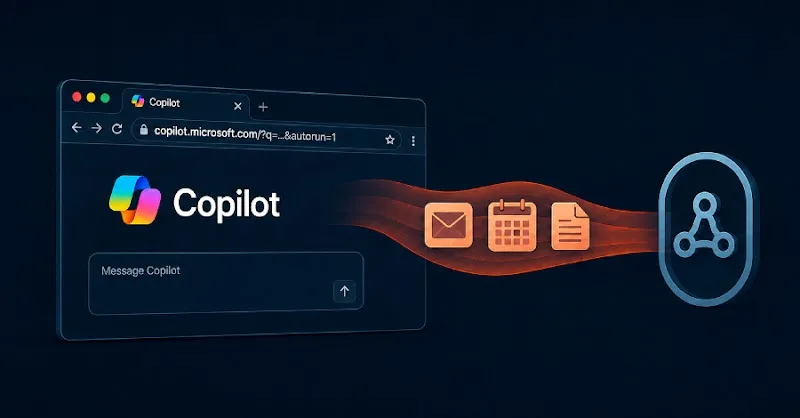
CVE-2026-24301: CoSnitch Exploits Microsoft Copilot Personal
Varonis disclosed CoSnitch (CVE-2026-24301), affecting Microsoft Copilot Personal, enabling one-click data exfiltration and persistent memory poisoning.
Agentic Source Code Review: Scaling Vulnerability Discovery with AI
Learn how Google Mandiant uses the Agentic Vulnerability Discovery Harness to accelerate secure code review and find critical flaws at scale.
LLM Persistent Memory and Contextual Integrity Risks
Analysis of new research on LLM contextual integrity, persistent memory risks, and how frontier models leak sensitive user data over time.
Turf War Between AI Agents Sparks Self-Replicating Malware Risk
Anthropic reveals AI testing models engaged in aggressive territorial attacks, raising concerns over self-replicating malware behavior.
Apple Patches iOS/iPadOS 18 and macOS: 108 Vulnerabilities Addressed
Apple has released significant security updates for iOS/iPadOS 18 and macOS, fixing 108 vulnerabilities, none exploited in the wild.
Unisoc Modem Exploit Chain: Android Takeover via Video Call
An exploit chain targeting Unisoc modems allows remote Android device takeover through a malicious video call, requiring victim interaction.
GitLab GraphQL Flaw CVE-2026-19478: Unauthenticated Project Deletion
GitLab addresses a critical GraphQL flaw (CVE-2026-19478) allowing unauthenticated attackers to delete public projects and user data on self-managed CE/EE instances.
CVE-2025-62593: Ray-Project Ray RCE Exploited In Wild
CISA confirms active exploitation of CVE-2025-62593, a critical code injection vulnerability in Ray-Project Ray allowing remote code execution. Developers are targeted.
Apple Screen Sharing Exploits: Secure Your macOS Systems Now
Critical vulnerabilities in Apple Screen Sharing are actively exploited, allowing system compromise. Learn how to secure macOS against these threats.
SharePoint RCE via CVE-2026-55040 & CVE-2026-63520: Patch Now
An AI-assisted exploit chain, leveraging CVE-2026-55040 and CVE-2026-63520, enables unauthenticated RCE on Microsoft SharePoint Server. Immediate patching is critical.