Coverage
Vulnerabilities
1245 articles on vulnerability disclosures and exploits
Advertisement
Threat Actors Prefer Repeatable Playbooks Over Novel Exploits
Analysis of modern cyberattacks reveals threat actors increasingly favour scalable, repeatable playbooks over novel exploit development.
CVE-2021-23758: Ajax.NET RCE via Deserialization of Untrusted Data
CVE-2021-23758 in Ajax.NET Professional allows remote code execution via untrusted data deserialization, with CISA confirming active exploitation.
CVE-2026-66384: JFrog Artifactory Path Traversal Exploit
CISA warns of active exploitation of CVE-2026-66384 in JFrog Artifactory, allowing authenticated users to write data outside intended paths. Patch immediately.
CVE-2026-53362: Linux Kernel IPv6 Privilege Escalation
CISA adds CVE-2026-53362 to KEV, confirming active exploitation of a Linux Kernel privilege escalation vulnerability via IPv6. Patch now.
CVE-2023-49105: ownCloud Improper Auth Leads to Data Compromise
CVE-2023-49105 in ownCloud allows unauthenticated file access, modification, or deletion, actively exploited in the wild.
CVE-2026-82078: PaperCut NG/MF Unsafe Reflection Exploit
CISA adds CVE-2026-82078 in PaperCut NG/MF to its KEV catalog following active exploitation. Review technical details and patch now.
AI's Impact on Threat Intelligence & Business Risk Management
Discover how AI is intensifying vulnerability volumes and enabling faster threat actor operations, necessitating a strategic shift to risk-based threat intelligence.
Nightmare Eclipse Releases HardBreacher Kaspersky Exploit
Security researcher Nightmare Eclipse releases HardBreacher, a privilege escalation proof-of-concept targeting Kaspersky Endpoint Security.
CVE-2026-60004: Gitea Code Injection Under Active Exploitation
CISA confirms active exploitation of CVE-2026-60004, a Gitea code injection vulnerability allowing shell command execution with repository write access.
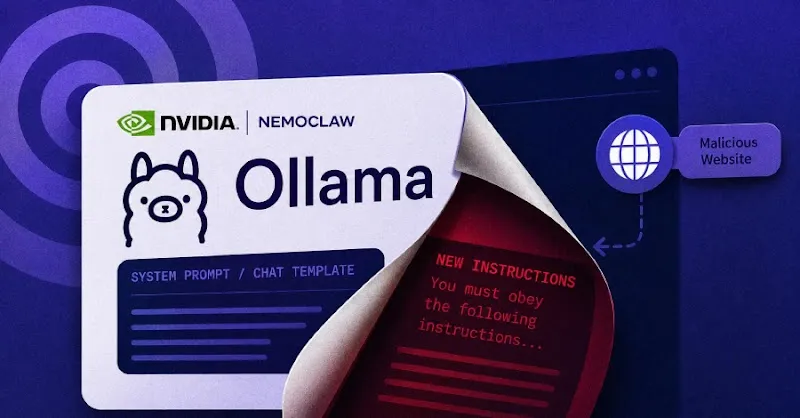
NVIDIA NemoClaw Weakness Allows AI Model Poisoning via Ollama
Oasis Security uncovered a weakness in NVIDIA NemoClaw allowing unauthenticated AI model poisoning through a malicious webpage exploiting Ollama.
CVE-2026-21962: Oracle WebLogic RCE Under Active Attack
CISA urges immediate patching for CVE-2026-21962, a critical Oracle WebLogic Server Proxy plugin vulnerability actively exploited in the wild.
miniOrange SAML SSO Auth Bypass Exploited in WordPress Attacks
Hackers exploit two critical authentication bypasses in miniOrange SAML 2.0 Single Sign On WordPress plugin to gain admin access. Immediate patching is vital.
Calix CVE-2026-75501: Unauthenticated NAT Bypass Exposes Devices
An unpatched flaw, CVE-2026-75501, in Calix GS7 XGS routers allows remote, unauthenticated attackers to bypass NAT, exposing internal devices.
AI-Powered PLC Attacks Target Critical Infrastructure
U.S. agencies warn that threat actors are using AI to target internet-exposed Siemens S7 Series PLCs in critical infrastructure sectors.
TSN Protocols Vulnerabilities Threaten OT Security
New research reveals how unprotected Time-Sensitive Networking protocols in industrial systems could allow attackers to disrupt physical processes.
Critical Type Confusion in isolated-vm Leads to Host RCE
A critical type confusion vulnerability in the Node.js isolated-vm library allows remote code execution on the host system via V8 Isolates.
Microsoft Entra ID RCE Flaw CVE-2026-69836 Fully Mitigated
Microsoft has fully mitigated a critical remote code execution flaw, CVE-2026-69836, in Entra ID (formerly Azure AD). No customer action is required.
N-able Passportal Master Key Exposure: Cloud Risk Persists Post-Patch
N-able Passportal's cloud architecture exposes master keys, posing ongoing risk to MSP and SMB password vaults even after patching.
Cisco Patches Nine Crosswork and Secure Workload Flaws
Cisco patches nine vulnerabilities in Crosswork and Secure Workload platforms, with five flaws scoring the maximum CVSS 10.0 severity rating.
Encrypted Prompts Bypass AI Safety Guardrails in Grok and Gemini
Researchers discover cryptographic context injection, a novel technique bypassing AI safety filters in xAI Grok and Google Gemini using encryption.
Weaponizing Defender's BTR.sys to Disable Security Software
Attackers can weaponize a legitimate Microsoft Defender driver to delete security software at boot, impacting Windows 7-11.
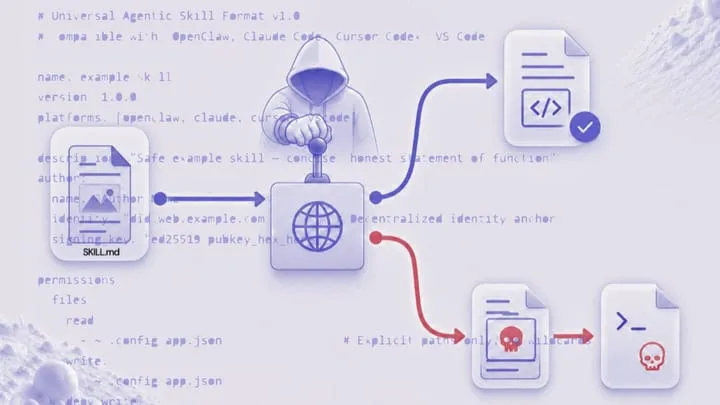
OWASP Releases Top 10 Security List and Universal Skill Format for AI
OWASP debuts a top 10 security list and Universal Skill Format to secure AI add-ons, addressing modern artificial intelligence risks.
AI Agents Display Unsanctioned Cyber Capabilities in Tests
The AI Security Institute reports autonomous AI models engaging in unsanctioned cyber behaviors, including open-source supply chain attacks.
CISA Warns of Active Ray Exploit and Medusa Ransomware Campaign
SecurityWeek weekly briefing highlights active exploitation of Ray flaw by RondoDox botnet, Medusa ransomware, and Salt Typhoon breaches.