Advertisement
CVE-2026-41940: Active Zero-Day Exploitation in cPanel and WHM
Critical zero-day CVE-2026-41940 in cPanel and WHM allows for authentication bypass. Learn about active exploitation, public PoCs, and essential patch guidance.

Gemini CLI Critical RCE Fix: Patching the @google/gemini-cli Flaw
Google patches a CVSS 10.0 flaw in Gemini CLI tools that allowed unprivileged attackers to execute commands in CI/CD environments via malicious configurations.
WordPress Quick Page/Post Redirect Backdoor: Arbitrary Code Injection
A dormant backdoor in the Quick Page/Post Redirect WordPress plugin allowed arbitrary code injection for five years on over 70,000 sites. Learn mitigation.
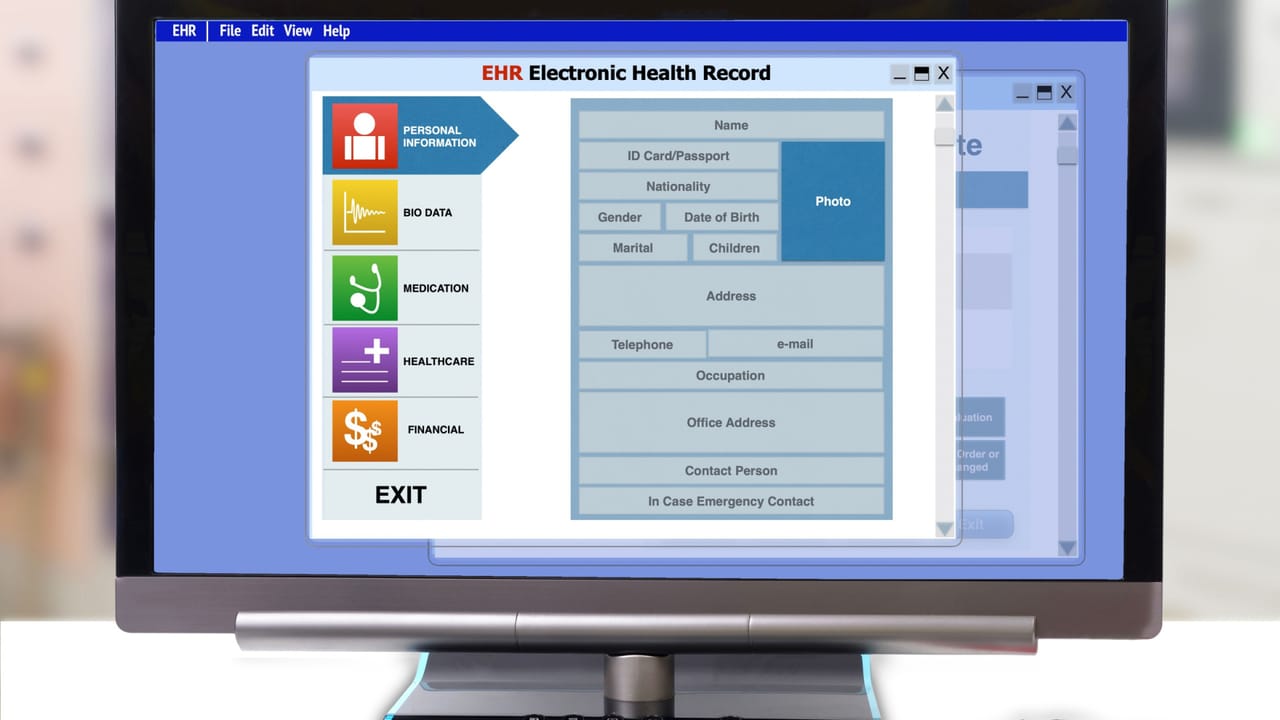
OpenEMR Flaws: Database Compromise, RCE, and Patient Data Theft Risks
Analysis of 38 security flaws in OpenEMR, an EHR platform used by over 100,000 healthcare providers, enabling database compromise, RCE, and data theft.
GitHub High-Severity Bug Discovered via AI Reverse Engineering
Wiz utilized AI reverse-engineering to uncover a high-severity vulnerability within GitHub, demonstrating advanced discovery methods for complex bugs.
LiteLLM Proxy Data Exposure & Modification — Urgent Patch Required
Critical vulnerability in LiteLLM proxy enables unauthorized database read/modify access. Exploitation observed shortly after disclosure. Patch immediately.
Advertisement
CVE-2020-27686: cPanel and WHM 2FA Authentication Bypass Mitigation
Administrators must patch cPanel and WHM immediately to address a critical 2FA bypass vulnerability that allows attackers to brute-force security codes.
Firefox 150 Patch: 271 Zero-Days Found via Claude Mythos — Update Now
Firefox 150 addresses 271 vulnerabilities discovered by Anthropic’s Claude Mythos AI model, highlighting a shift in automated vulnerability discovery.
Windows Kernel LPE CVE-2024-21338: Lazarus Group Exploits Zero-Day
CISA adds CVE-2024-21338 to KEV catalog after Lazarus Group exploited the Windows Kernel vulnerability to deploy rootkits and bypass security controls.

cPanel Authentication Bypass: Patch Guidance for Versions 11.132.0.29
cPanel releases critical updates to address an authentication bypass vulnerability affecting all supported versions. Administrators should patch immediately.

Optimizing Exposure Management: Beyond CVSS and Patch Fatigue
A technical analysis of Continuous Threat Exposure Management (CTEM) and why modern security teams must prioritize vulnerabilities based on business risk.
CVE-2024-24919: Exploit Analysis and Check Point Gateway Mitigation
Technical analysis of CVE-2024-24919, a critical information disclosure vulnerability in Check Point Security Gateways exploited for credential harvesting.
CVE-2024-1708 & CVE-2026-32202: CISA KEV Update — Patch Now
CISA adds CVE-2024-1708 and CVE-2026-32202 to the Known Exploited Vulnerabilities Catalog following evidence of active exploitation in the wild.
NSA GRASSMARLIN XXE Vulnerability CVE-2026-6807 — Mitigation Guide
CISA warns of a Medium-severity XXE vulnerability in NSA GRASSMARLIN. With the tool reaching end-of-life, defenders must address CVE-2026-6807 via decommissioning.
GitHub Enterprise Server RCE via CVE-2024-6800 — Mitigation Guide
GitHub has patched a critical RCE vulnerability (CVE-2024-6800) in GHES that allows remote attackers to gain administrative access via SAML SSO bypass.

CVE-2026-42208: Active Exploitation of LiteLLM SQL Injection
Attackers are actively exploiting CVE-2026-42208, a critical SQL injection flaw in LiteLLM, within 36 hours of disclosure. Patch to prevent database compromise.
CVE-2026-42208: LiteLLM Pre-Auth SQLi Actively Exploited – Patch Now
Hackers are actively exploiting CVE-2026-42208, a critical pre-authentication SQL injection vulnerability in LiteLLM, to access sensitive data.

CVE-2026-3854: GitHub RCE via Malicious Git Push Command
A critical command injection vulnerability, CVE-2026-3854, allows authenticated users to achieve RCE on GitHub instances via a single git push operation.
Microsoft RDP Security Warning Display Bug — Mitigation Guide
Microsoft confirms security warnings for Remote Desktop (.rdp) files may display incorrectly on Windows 10 and 11, potentially obscuring risk information.

Hugging Face LeRobot RCE via CVE-2026-25874 — Mitigation Guide
Technical analysis of CVE-2026-25874, a critical unpatched RCE vulnerability in Hugging Face LeRobot robotics platform with a CVSS score of 9.3.

CVE-2026-32202: Active Exploitation of Windows Shell Spoofing Bug
Microsoft confirms CVE-2026-32202, a Windows Shell spoofing flaw, is under active exploitation. Read our analysis and mitigation guide for enterprise security.
CVE-2024-9486: Critical Kubernetes Image Builder Flaws Exposed
Critical vulnerabilities in Kubernetes Image Builder allow root access via hardcoded credentials. Update to version v0.1.38 to mitigate potential exploits.

Unpatched PhantomRPC: Windows Privilege Escalation via RPC Flaw
Runtime Rebel analyzes the unpatched 'PhantomRPC' flaw in Windows, detailing how an architectural weakness in RPC enables local privilege escalation.
APT28 Exploits Incomplete Windows Patch: Zero-Click Attacks Persist
An incomplete Windows patch leaves systems vulnerable to zero-click attacks. Russia-linked APT28 exploited this against Ukraine and EU. Learn how to defend.