Advertisement
CVE-2026-104935: Ivanti Connect Secure RCE via Auth Bypass
CISA confirms active exploitation of CVE-2026-104935 in Ivanti Connect Secure, an auth bypass leading to remote code execution.
Dell CSM Critical Flaws: Unauthenticated Admin on Kubernetes Nodes
Dell Container Storage Modules (CSM) versions prior to 1.17.0 are critically vulnerable, enabling unauthenticated admin access and Kubernetes node compromise.
Fortra BoKS Patches Critical Vulnerabilities: RCE, Auth Bypass
Fortra patches critical flaws in BoKS Core Privileged Access Manager, including authentication bypass (CVE-2026-79901) and command injection (CVE-2026-79898).
Critical Citrix NetScaler Zero-Days: CVE-2026-88772 & CVE-2026-88771
Mandiant and Google identified active zero-day exploitation (CVE-2026-88772, CVE-2026-88771) in Citrix NetScaler ADC and Gateway, leading to root access.
MikroTik RouterOS Critical Flaws Chained to Hack Routers
Critical vulnerabilities in MikroTik RouterOS, including CVE-2026-67276 and CVE-2026-86060, are actively exploited to gain full control of routers. Patch immediately.
CVE-2026-19490: Citrix NetScaler Auth Bypass Under Attack
Critical Citrix NetScaler authentication bypass (CVE-2026-19490) is actively exploited in the wild, allowing remote unprivileged access.
Advertisement
CVE-2026-48710: Kludex Starlette HTTP Smuggling for Auth Bypass
CVE-2026-48710 impacts Kludex Starlette, enabling HTTP request smuggling and authentication bypass via path injection. Actively exploited.
CVE-2026-59822: BerriAI LiteLLM Authentication Bypass
BerriAI LiteLLM is vulnerable to an improper authentication flaw (CVE-2026-59822) actively exploited to bypass authentication.
CVE-2026-84115: Cleo Harmony Auth Bypass Exploit Published
An exploit is published for CVE-2026-84115, an authentication bypass in Cleo Harmony allowing remote privilege escalation. Immediate patching to v5.8.1.11 is urged.
CVE-2026-82329: JFrog Artifactory Auth Bypass to Admin Tokens
Threat actors are exploiting CVE-2026-82329 in JFrog Artifactory, an authentication bypass allowing unauthenticated admin access. Patch immediately.
CVE-2026-62911: Exchange Servers Vulnerable to Mailbox Hijack
Nearly 22,000 Microsoft Exchange Servers remain unpatched against CVE-2026-62911, an auth bypass allowing mailbox hijack attacks.
miniOrange SAML SSO Auth Bypass Exploited in WordPress Attacks
Hackers exploit two critical authentication bypasses in miniOrange SAML 2.0 Single Sign On WordPress plugin to gain admin access. Immediate patching is vital.
macOS Screen Sharing Flaw Exploited to Deploy Monero Miner
The Netherlands NCSC warns that hackers are actively exploiting an authentication bypass flaw in macOS Screen Sharing to deploy cryptocurrency miners.
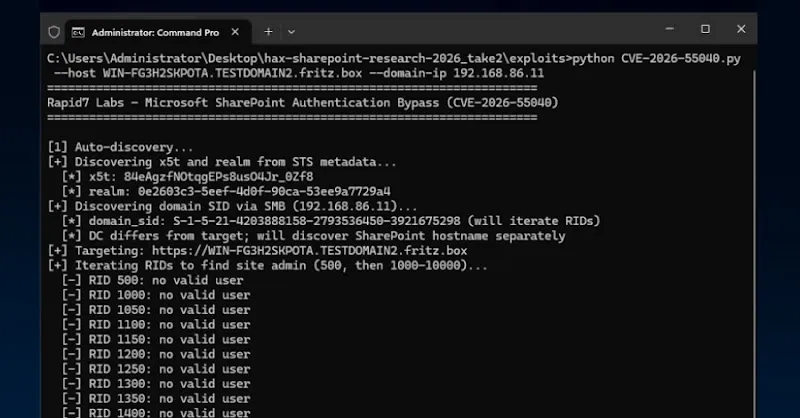
CVE-2026-55040: Critical SharePoint Auth Bypass Exploited After PoC
Attackers exploit CVE-2026-55040, a critical authentication bypass in Microsoft SharePoint, leading to data disclosure and modification.
Microsoft & Apple Patch Critical RCEs and Auth Bypass Flaws
Microsoft released patches for critical-severity RCE and EoP flaws across Active Directory, Azure, and Teams. Apple fixed a Screen Sharing authentication bypass.
CVE-2026-18556: N-able N-central Authentication Bypass Actively Exploited
CISA added CVE-2026-18556 to its KEV catalog, confirming active exploitation of an N-able N-central authentication bypass vulnerability.
CVE-2026-18577: Attackers Exploit N-able Patch Bypass
Security teams face active exploitation of CVE-2026-18577, an N-able authentication bypass vulnerability granting administrator access.
CVE-2026-20316: Cisco Secure FMC Hard-coded Password Vulnerability
CISA confirms active exploitation of CVE-2026-20316, a hard-coded password vulnerability in Cisco Secure Firewall Management Center.
VMware Critical Flaws: Auth Bypass, RCE, VM Escapes Patched
VMware has patched critical vulnerabilities across vCenter, ESX, Workstation, and Fusion, addressing authentication bypass, remote code execution, and VM escapes.
PAN-OS GlobalProtect Authentication Bypass Exploited by Qilin
The Qilin ransomware gang is actively exploiting a critical Palo Alto Networks PAN-OS GlobalProtect authentication bypass vulnerability to breach corporate networks.

n8n Token Exchange Flaw: Impersonation via `sub` Claim Bypass
A critical token exchange vulnerability in n8n Enterprise allows attackers to impersonate users by leveraging `sub` claim matching across multiple external issuers…
F5 BIG-IP and NGINX Vulnerabilities: CVE-2024-41730 and CVE-2024-39475
F5 releases critical security updates for BIG-IP and NGINX Plus, addressing authentication bypass, RCE, and memory corruption vulnerabilities.
VMware Avi Load Balancer: Severe Vulnerabilities Enable RCE, Bypass
VMware has patched 7 severe vulnerabilities in Avi Load Balancer, enabling authentication bypass, RCE, privilege escalation, and directory traversal.
Gitea CVE-2026-20896 Authentication Bypass Under Active Exploitation
Attackers are exploiting CVE-2026-20896 in Gitea to bypass authentication via HTTP headers, risking unauthorized access to private code and secrets.