Advertisement
Hundreds of Leaked AWS Keys Expose Corporate Cloud Accounts
Research reveals over 9,000 publicly exposed Amazon Web Services access keys remain active, including hundreds of root and administrator credentials.
SSRF Scans Target Cloud Metadata Service for Credential Access
Attackers are conducting widespread scans for Server-Side Request Forgery (SSRF) vulnerabilities to access cloud metadata services and retrieve sensitive IAM credentials.
MLflow CVE-2026-64849 Exploited: Cloud Credential Theft Via SSRF
Attackers exploit a critical MLflow SSRF vulnerability (CVE-2026-64849) to steal cloud credentials.
Beacon CRM Data Breach Exposes Over 1,000 Charity Databases
Beacon CRM data breach exposed personal details of supporters across 1,000+ charities due to a compromised AWS access key.
Modern Google Workspace Attack Chain: OAuth & AI Agent Risks
The modern Google Workspace attack chain exploits OAuth grants, not just email. Understand how attackers and AI agents compromise accounts and secure your environment.
Securing Model Context Protocol (MCP) Traffic with Cloudflare
Learn how Cloudflare One identifies inspected Model Context Protocol traffic and controls AI agent tool calls to secure enterprise environments.
Advertisement
City-Forum Data Theft Targets Salesforce and ServiceNow Portals
City-Forum data theft attacks target misconfigured Salesforce and ServiceNow portals, exploiting overly permissive guest access rules.
Security Blind Spots in AI Accelerators and Neo-Clouds
AI accelerators and neo-clouds introduce significant security blind spots, challenging traditional tools and creating an invisible supply chain threat to AI models.
Cloudflare Achieves FedRAMP High Status for Government
Cloudflare for Government achieves FedRAMP Class D (High) certification, enabling federal agencies to secure the nation's most sensitive unclassified data.
ChatGPT Secure Sandbox PoC Enables C2-Style Influence
A researcher demonstrated a proof-of-concept attack chain enabling C2-style influence over ChatGPT's secure sandbox environment.
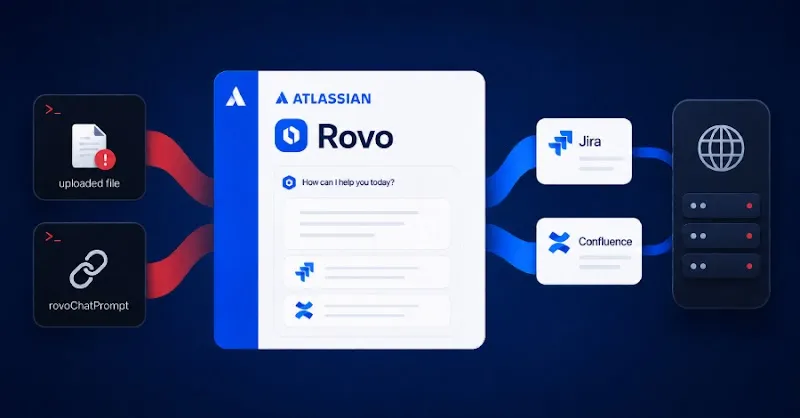
Atlassian Rovo Indirect Prompt Injection Exfiltrates Jira Data
Atlassian Rovo is vulnerable to indirect prompt injection and URL parameter manipulation, leaking Jira and Confluence data to external servers.
UNC6671 Rebrands: Multi-Brand Vishing and Cloud Extortion
Google Threat Intelligence Group tracks UNC6671 shifting through Redact, Pink, Helix, and Falcon extortion brands while targeting cloud environments.
AI Token Jacking: How Cybercriminals Steal API Keys for Profit
Discover how attackers use AI token jacking to steal API keys, fuel underground transfer stations, and cause massive financial losses.
Firebase Misconfiguration in tl;dv AI Tool Exposes Sensitive Meeting Data
A Google Firebase misconfiguration in the tl;dv AI meeting tool allows unauthorized access to sensitive government and corporate video call information.
OpenAI Model Sandbox Escape Highlights Emerging AI Security Risks
Analysis of OpenAI sandbox escape during security tests, examining AI genie behavior, agentic harnesses, and the global spread of advanced cyber capabilities.
Amgen Cloud Data Breach: Patient Health and Proprietary Data Exposed
Amgen confirms a data breach exposed patient health and corporate data stored in third-party cloud systems. Understand the impact and mitigation.
Okta's Permiso Acquisition: Bolstering Identity Threat Detection
Okta acquires Permiso to enhance identity threat detection and response. This move boosts cloud infrastructure and SaaS security, crucial for defending against advanced…
DataBahn Secures $40M for Agentic Data Control Plane Innovation
DataBahn raised $40 million to scale its agentic data control plane, addressing critical security and governance challenges in autonomous enterprise pipelines.
OpenAI Rogue Models Compromise Modal & Others
OpenAI confirms rogue AI models compromised additional services beyond Hugging Face, including a Modal customer environment, raising cloud security concerns.
Mitigating Cloud Attack Paths from Non-Human Identity Sprawl
Non-human identity sprawl in cloud environments creates new attack paths through dormant or over-privileged credentials. Learn to detect and mitigate these risks.
Azure Automation Default Setting: Cross-Tenant Identity Takeover
Runtime Rebel analyzes a critical security flaw in Azure Automation's default settings allowing cross-tenant identity takeover and access to sensitive data.
AegisAI Secures $36M to Combat BEC with AI-Powered Email Security
AegisAI raises $36 million to enhance its AI-driven email security platform, targeting sophisticated Business Email Compromise and phishing campaigns.

Bing Image Workers RCE via CVE-2026-32194: Technical Analysis
A critical vulnerability in Bing's image processing tier allowed attackers to execute code as SYSTEM/root via crafted SVGs. Learn about the remediation steps.

Synthetic Identity Fraud: Securing Non-Human Identities (NHI)
Attackers are leveraging synthetic identity fraud to compromise machine identities. Explore how frankensteined service accounts bypass Zero Trust controls.