Advertisement
FBI Arrests Ransomware Negotiator Linked to ShinyHunters
FBI agents arrested a Canadian ransomware negotiation executive in Pennsylvania over alleged ties to the ShinyHunters hacking group.
Venezuelan Cartel's Malware Honcho Nabbed for ATM Jackpotting
Cybercriminal linked to Venezuela's Tren de Aragua cartel arrested for ATM jackpotting operations, highlighting cyber-physical crime convergence.
Qilin Ransomware Suspect Extradited, Group Exploits Check Point VPN
A Qilin ransomware group member was extradited to Germany, highlighting the prolific RaaS operation's global reach and exploitation of critical vulnerabilities.
FBI Arrests Ploutus ATM Malware Developer, Disrupting TdA
FBI arrests Anibal Alexander Canelon Aguirre, primary developer of Ploutus ATM malware, disrupting Tren de Aragua's extensive jackpotting operations across 47 US states.
KillSec Ransomware Mastermind Arrested: 16-Year-Old Suspect
International law enforcement disrupts the KillSec ransomware operation, arresting an alleged 16-year-old mastermind behind attacks on 500 victims.
Warlock Ransomware Targets Spanish, Portuguese Orgs
Warlock ransomware campaign targets large organizations in Spain and Portugal, exhibiting characteristics of both cybercrime and state-associated APTs.
Advertisement
Operation KillSwitch Dismantles KillSec Ransomware Gang
International law enforcement operation "KillSwitch" dismantled the KillSec ransomware gang, arresting suspects and seizing 110TB of stolen data.
Ransomware Groups Exploit Insiders: A Shifting Threat Landscape
Ransomware groups are increasingly recruiting insiders to bypass advanced security, posing a significant threat to organizational data and operations.
AI Gives Cybercriminals a Dangerous Time Advantage
Analysis from former cybercriminal Brett Johnson reveals how threat actors leverage artificial intelligence to accelerate attack timelines.
ShinyHunters: Dark Reading on Potential ReliaQuest Breach
Dark Reading editors discuss the latest activities of the ShinyHunters threat group, including inquiries into a potential breach affecting ReliaQuest.
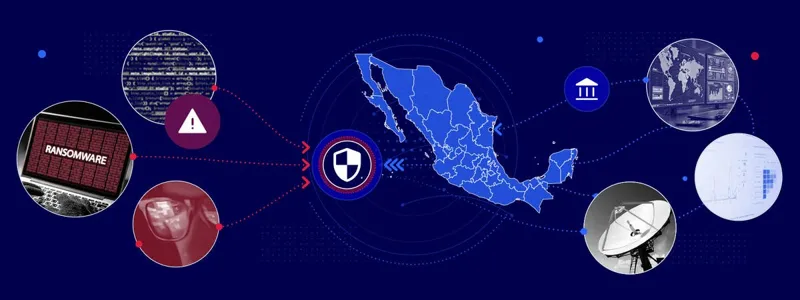
Mexico’s Cybersecurity Plan 2025-2030: Addressing Rising Threats
Mexico's National Cybersecurity Plan 2025-2030 aims to strengthen defenses against ransomware, state-sponsored espionage, and cybercrime.
Cybercrime Policing Roadblocks: Funding & Training Gaps
Law enforcement faces significant hurdles in combating cybercrime, primarily due to insufficient funding for training and a lack of strategic focus.
UAT-10147 Leverages Agentic AI for EDR-Evasive Cybercrime
Talos details UAT-10147, an AI-driven cybercrime group orchestrating sophisticated post-compromise operations and evading EDR with custom rootkits.
Kriminal AI Platform Fuels Cybercrime: OSINT & Social Engineering
The 'Kriminal' AI platform, offering guardrail-free social engineering and OSINT, raises significant concerns about its potential to fuel cybercrime.
Cybercrime's Coordination Gap: Attackers Outpace Law Enforcement
Analysis of the widening gap between agile cybercrime organizations and fragmented global law enforcement efforts, highlighting the impact on cybersecurity.
Snowflake Hacker Pleads Guilty: Analyzing the UNC5537 Data Breach
Hacker pleads guilty in UNC5537 Snowflake data breach, compromising 165 organizations and millions of records via stolen credentials.
Interpol's I-GRIP System Curtails Fraudulent Payments: A Threat Intel Brief
Explore Interpol's I-GRIP system, a global initiative enabling rapid freezing of fraudulent payments and enhancing international cooperation against cyber-enabled…
ShinyHunters Breaches Brinks Home, Threatens Data Leak
ShinyHunters claims a breach of Brinks Home systems, threatening to leak stolen data. This analysis covers the threat actor, potential impact, and mitigation.
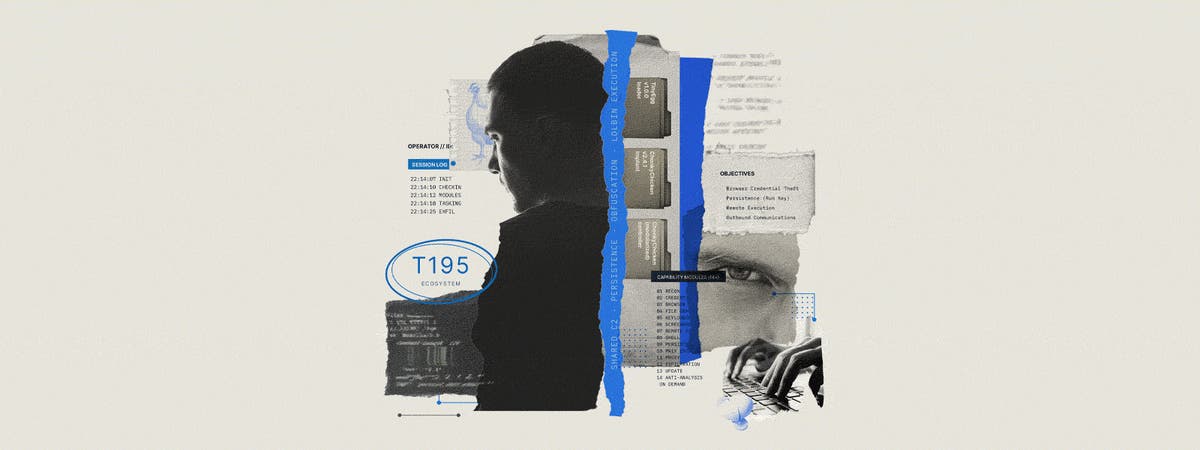
TAG-195 Evolves MaaS Ecosystem with Modular Malware
Insikt Group identifies TAG-195's new modular malware families, signalling a significant shift in the Malware-as-a-Service ecosystem and operator-driven tooling.
Evolving Carding Tactics: Residential Proxies & Fraud Detection Evasion
Cybercriminals leverage "clean" residential proxies, browser fingerprints, and device profiles to bypass modern fraud detection systems, enhancing carding success.
Spanish Police Dismantle €140M Cyber Fraud Ring: BEC & Investment Schemes
Spanish Police dismantle a sophisticated cybercrime organization responsible for €140 million in BEC and investment fraud, arresting four key individuals.
ScamBuster: AI-Driven Phishing Engagement for Threat Intel
Explore ScamBuster, an open-source, AI-driven tool that actively engages phishing attackers to gather intelligence on their TTPs, aiding threat detection and law…
Odido Data Breach Analysis: Dutch Police Suspect Local Hacker Involvement
Dutch National Police identify strong indications of local hacker involvement in the February data breach at telecommunications provider Odido.
Ryuk Ransomware Affiliate Pleads Guilty to US Hacking Charges
A 34-year-old Armenian national faces 15 years in prison for his role in the Ryuk ransomware operation, which targeted U.S. hospitals and businesses.