Advertisement
GreyVibe Actor Leverages AI Lures to Target Ukrainian Entities
Russian threat cluster GreyVibe uses ChatGPT and Gemini to automate highly targeted phishing lures and deploy custom malware against Ukrainian targets.

JINX-0164 Targets Crypto Firms with macOS Malware and Fake Lures
The JINX-0164 threat actor targets cryptocurrency firms via recruitment-themed social engineering, macOS-specific malware, and CI/CD infrastructure exploits.
Silent Ransom Group Targets Law Firms via Physical Social Engineering
FBI warns of Silent Ransom Group (Luna Moth) targeting law firms using physical social engineering and data theft for extortion. Learn how to defend.
SEO Poisoning and AI Chatbots Spread GPU Mining Malware
Threat actors are using SEO poisoning and manipulated AI chatbot recommendations to distribute persistent GPU mining malware to high-performance systems.

AI Chatbot Poisoning: Defending Against Malicious Cryptojacking Links
Microsoft warns of threat actors manipulating AI chatbot recommendations to deliver cryptojacking malware via poisoned web search results.
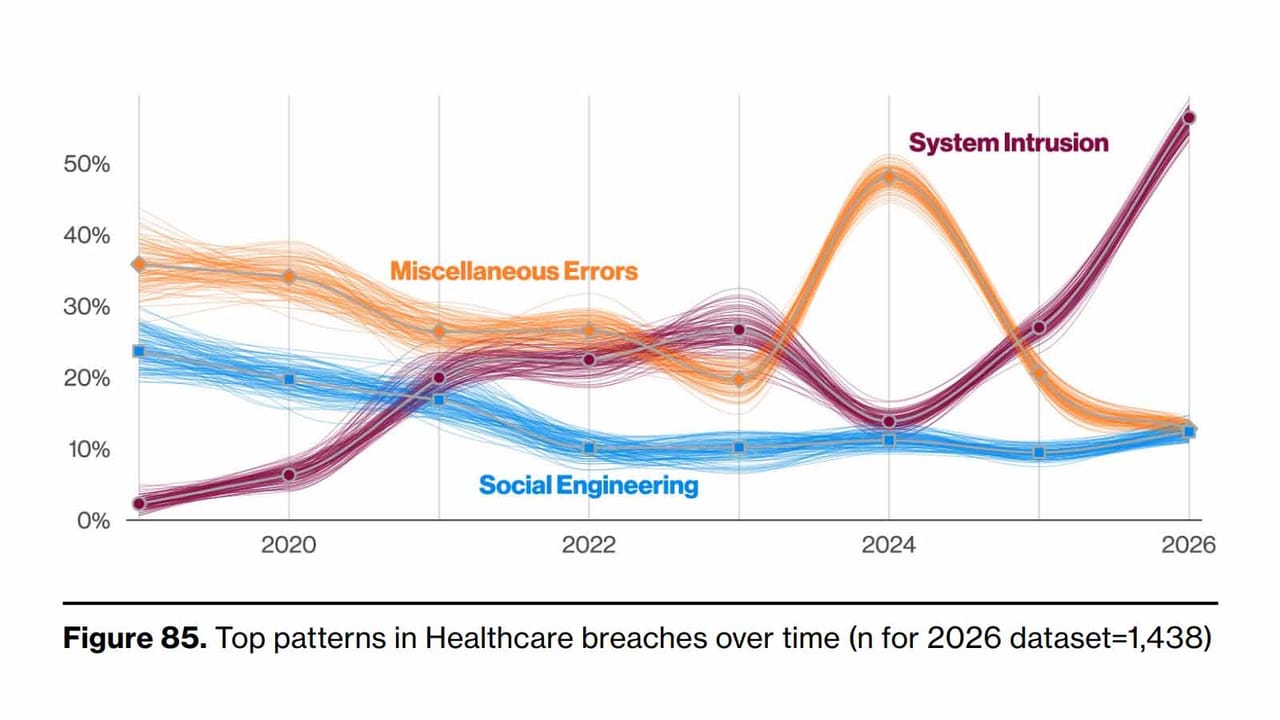
Verizon DBIR 2024: Healthcare Targeted by Social Engineering
An analysis of the 2024 Verizon DBIR healthcare findings, highlighting the surge in social engineering, ransomware, and supply chain vulnerabilities.
Advertisement
Tech Support Fraud: Executives Plead Guilty in Infrastructure Case
Former executives of CallerReady plead guilty to facilitating global tech support scams by providing call-tracking and CRM infrastructure to fraudsters.
FBI Warns: $388M Lost to Crypto ATM Scams in 2023 – Defense Guide
The FBI reports Americans lost over $388 million to crypto ATM scams in 2023, driven by social engineering. Learn how to protect against these financial frauds.
South Korea Deepfake Election Law: Testing AI Content Regulations
South Korea implements strict laws banning AI-generated deepfakes in elections. Explore the technical challenges of detection and legislative enforcement.
BlackFile: Analyzing UNC6671 Vishing & Cloud Data Extortion
Examines UNC6671's BlackFile vishing, AiTM, and cloud data exfiltration tactics against Microsoft 365 & Okta. Actionable mitigations included.
Anatomy of E-Commerce Fraud: Detecting and Mitigating Phishing Sites
A technical analysis of fraudulent retail infrastructure, exploring domain spoofing, CDN obfuscation, and credit card exfiltration techniques.
Empowering Human Defenses: Addressing Threats Unstoppable by Tech
Cybersecurity defenses often overlook the human element. This analysis details how employees are the critical first line against advanced social engineering and insider…
Fake OpenAI Hugging Face Repository Distributes Infostealer Malware
Attackers leveraged a fraudulent OpenAI repository on Hugging Face to distribute infostealers. Learn to detect and mitigate these AI supply chain threats.
ClickFix Attacks Distribute Vidar Stealer: ACSC Warning & Mitigation
The ACSC warns Australian organizations of active ClickFix social engineering attacks deploying Vidar Stealer malware, risking data theft. Learn detection and mitigation.

Neutralizing Patient Zero: Strategies to Prevent Stealth Breaches
Analyze how AI-driven social engineering creates a Patient Zero scenario and explore technical strategies to contain stealth breaches before total shutdown.
Crypto Gang Sentencing: Inside the $243M Greavys Group Heist
A 20-year-old gang member receives a 6.5-year sentence for his role in a $243 million crypto heist involving home invasion and social engineering.
MuddyWater Exploits Microsoft Teams via Chaos Ransomware Decoy
Iranian APT MuddyWater utilizes Microsoft Teams social engineering and Chaos ransomware decoys to mask state-sponsored espionage operations.

MuddyWater Exploits Microsoft Teams for False Flag Ransomware
Iranian APT MuddyWater is leveraging Microsoft Teams social engineering to deploy false flag ransomware, obscuring state-sponsored espionage activities.
Legacy of the USB Drop: Evolution of Social Engineering TTPs
An analysis of the historical 2006 USB penetration test that shaped modern social engineering defense and the evolution of hardware-based attack vectors.
DigiCert Revokes Certificates After Support Portal Compromise
DigiCert is revoking TLS/SSL certificates following a breach where attackers used support chat to compromise an internal analyst's workstation and portal.
Bluekit Phishing Kit: AI Integration and Automated Deployment
The Bluekit phishing kit uses an AI assistant and automated domain registration to simplify credential harvesting against financial and logistics sectors.
Hugging Face and ClawHub Abused for Malware Distribution
Threat actors are exploiting the trust of AI and code-hosting platforms like Hugging Face and ClawHub to distribute malware via social engineering lures.
European Police Dismantle €50 Million Crypto Investment Fraud Ring
Authorities in Austria and Albania shut down a massive crypto investment scam involving fraudulent call centers and over €50 million in victim losses.
UNC6692 Leverages Teams, AWS S3 for Malware & Cloud Abuse
Newly discovered threat actor UNC6692 combines social engineering via Microsoft Teams with custom 'Snow' malware and AWS S3 cloud abuse in multi-pronged attacks.