Advertisement
Mathspace Breach: Over 1 Million Impacted by Metabase Zero-Day
Mathspace disclosed a data breach affecting over 1 million students, staff, and parents due to a Metabase vulnerability.
CVE-2026-9586: Sangoma Switchvox RCE via SQL Injection
Sangoma Switchvox is affected by CVE-2026-9586, an unauthenticated remote SQL injection vulnerability enabling RCE, with active exploitation confirmed.
ShinyHunters Breaches ShipMonk: 14,000 Trezor Customers' Data Exposed
ShinyHunters group breached shipping provider ShipMonk, exposing personal data of 14,000 Trezor customers via a Metabase SQL injection vulnerability.
CVE-2026-72898: Metabase SQL Injection Active Exploitation
CISA adds Metabase CVE-2026-72898 SQL injection to its KEV catalog, enabling unauthenticated remote attackers to gain admin access.
Metabase Zero-Day SQL Vulnerability Threatens Analytics Platforms
Unpatched Metabase business-analytics zero-day vulnerability allows remote administrative access and threatens downstream corporate networks.
Metabase Zero-Day Exploited: Unauthenticated Admin Access
Metabase zero-day vulnerability (CVSS 10.0) actively exploited, allowing unauthenticated remote attackers to gain admin access and steal data.
Advertisement
Metabase SQLi Zero-Day Exploited: Data Theft Attacks Confirmed
A critical Metabase SQL injection zero-day vulnerability (versions 1.58+) has been exploited in data theft attacks affecting customers like Framework and Tally.
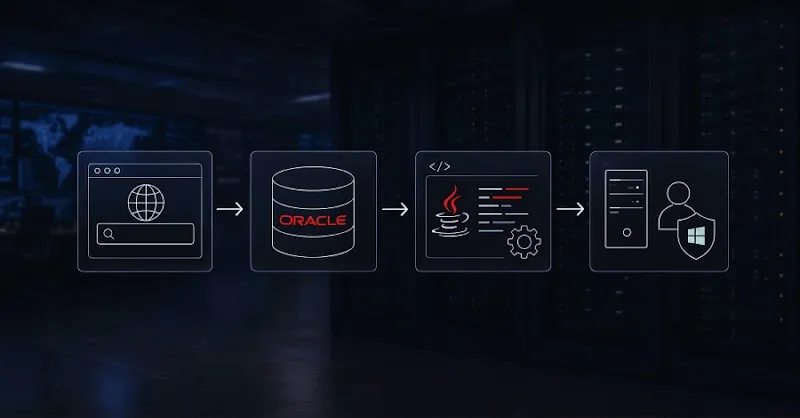
khunt Toolkit Leverages SQLi in Oracle for SYSTEM Access
Attackers exploit SQL injection in a public-facing web app to compile the khunt toolkit within Oracle, achieving SYSTEM-level access on Windows servers.
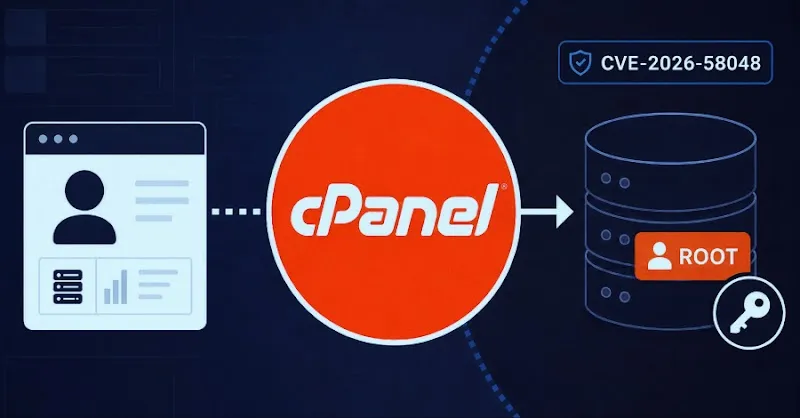
CVE-2026-58048: cPanel & WHM Critical SQL Privilege Escalation
A critical flaw in cPanel & WHM (CVE-2026-58048) allows authenticated users to execute SQL as database root, potentially leading to OS-level compromise.
CVE-2026-60137: WordPress Core SQL Injection to RCE — Patch Now
CISA warns of active exploitation for CVE-2026-60137, a WordPress Core SQL Injection vulnerability chaining to RCE for unauthenticated attackers.
CVE-2026-63030: WordPress Core SQLi Leads to Unauth RCE
Critical SQL injection vulnerability (CVE-2026-63030) in WordPress Core enables unauthenticated remote code execution. Active exploitation confirmed.
Critical RCEs: FortiNAC CVE-2023-33300 & SonicWall SMA Zero-Day
Two critical vulnerabilities, FortiNAC RCEs (CVE-2023-33300, CVE-2023-33299) and a SonicWall SMA zero-day SQLi, require immediate patching and mitigation.
Siemens KACO Blueplanet Inverter Vulnerabilities: CVE-2025-40946 & CVE-2026-41125
Critical Siemens KACO Blueplanet Inverters are vulnerable to credential derivation (CVE-2025-40946) and SQL injection (CVE-2026-41125).
Hardening Automatic Tank Gauge Systems Against Cyber Threats
CISA and partners warn of active cyber threats targeting Automatic Tank Gauge (ATG) systems. Learn to secure critical infrastructure assets now.
CVE-2023-48788: Critical FortiClient EMS RCE Under Active Exploitation
Exploitation of CVE-2023-48788 in FortiClient EMS allows unauthenticated remote code execution. Administrators must patch to version 7.2.3 or 7.0.11 immediately.
Drupal 7.x SQL Injection CVE-2014-3704 — Active Exploitation Alert
CISA adds Drupalgeddon SQL injection (CVE-2014-3704) to KEV catalog, mandating federal agencies to patch critical legacy systems against active exploits.

CVE-2026-26980: Ghost CMS SQL Injection Leads to ClickFix Attacks
Attackers exploit CVE-2026-26980 in Ghost CMS to compromise 700+ websites, deploying ClickFix malware that tricks users into executing malicious scripts.
CVE-2025-26980: Ghost CMS SQL Injection Exploited in ClickFix Campaign
A critical SQL injection vulnerability in Ghost CMS (CVE-2025-26980) is being exploited to deliver ClickFix malware through malicious JavaScript injections.

CVE-2026-9082: Drupal Core SQL Injection Added to CISA KEV Catalog
CISA warns of active exploitation of CVE-2026-9082, a critical SQL injection vulnerability in Drupal Core. Organizations must patch to prevent data exposure.
CVE-2026-9082: Drupal Core SQL Injection Under Active Exploitation
CISA adds CVE-2026-9082, a critical Drupal Core SQL Injection vulnerability, to KEV Catalog due to active exploitation. Immediate patching required for all organizations.
CVE-2024-2123 & CVE-2024-2510: Avada Builder Patch Guidance
Critical flaws in Avada Builder WordPress plugin (CVE-2024-2123, CVE-2024-2510) allow for credential theft and LFI. Immediate update to version 3.11.7 required.
CVE-2026-42208: BerriAI LiteLLM SQLi Exploitation — Patch Now
CISA adds CVE-2026-42208, a critical SQL injection vulnerability in BerriAI LiteLLM, to KEV catalog. Active exploitation confirmed.

CVE-2026-42208: Active Exploitation of LiteLLM SQL Injection
Attackers are actively exploiting CVE-2026-42208, a critical SQL injection flaw in LiteLLM, within 36 hours of disclosure. Patch to prevent database compromise.
CVE-2026-42208: LiteLLM Pre-Auth SQLi Actively Exploited – Patch Now
Hackers are actively exploiting CVE-2026-42208, a critical pre-authentication SQL injection vulnerability in LiteLLM, to access sensitive data.