Advertisement
Japan's Active Cyber Defense Strategy and Framework
Japan's Active Cyber Defense framework mandates critical infrastructure reporting and introduces new threat disruption authorities by late 2027.
Proactive Threat Intelligence: Shifting Beyond Reactive Security
Discover how proactive threat intelligence provides external context to prioritize vulnerabilities and detect attacks before internal alerts fire.
KillSec Ransomware Mastermind Arrested: 16-Year-Old Suspect
International law enforcement disrupts the KillSec ransomware operation, arresting an alleged 16-year-old mastermind behind attacks on 500 victims.
Osavul Secures $10M Series A for Hybrid Risk Intelligence
Hybrid risk intelligence firm Osavul raises $10 million in Series A funding to expand AI threat detection across cyber and physical domains.
ThreatsDay: AI Zero-Day Chains, ATM Jackpotting, and Cache Key Injection
Analysis of recent threat intelligence covering AI-powered zero-day chains, Tren de Aragua ATM jackpotting, and emerging web cache injection techniques.
Cisco Talos Newsletter: Frustrating Adversaries and Security Updates
Read the latest Threat Source newsletter by Cisco Talos, featuring adversary frustration tactics and weekly cybersecurity news summaries.
Advertisement
Microsoft Warns Threat Actors Lead the Early AI Security Race
Microsoft's Digital Defense Report reveals that threat actors are outpacing defenders in adopting AI, accelerating malware development and exploits.
Parsing Discrepancies in Phishing URLs: Analysis and Defenses
Analyze how attackers exploit URL parser discrepancies using userinfo fields, invalid hostnames, and path manipulation to evade security controls.
US Soldier Sentenced to 70 Months for Telecom Extortions
A US Army soldier operating as Kiberphant0m received a 70-month prison sentence for hacking telecommunications firms and extorting victims.
Offensive Security Investments Surge as AI Threats Increase
Enterprises increase offensive security spending as AI-driven attacks accelerate, shifting toward continuous testing and autonomous agents.
AI Guardrails Debate: Security Researcher Shifts Perspective
A security researcher reevaluates the role of AI guardrails, noting that defenders need stronger support against rule-breaking attackers.
Malicious PE Stats: Compiler Analysis of Malware Samples
Analysis of 1.3TB of malware samples examines PE headers, compiler trends, and tools used by attackers over a multi-year dataset.
Evaluating LLMs for SOC Operations and Log Analysis
Discover how Cisco Talos evaluated 66 model and reasoning combinations for SOC workflows, focusing on cost, speed, and consistency.
Crime Script Analysis: Mapping Threat Workflows and AI Risks
Discover how crime script analysis translates complex cyber attacks into narratives, highlighting AI threats in business email compromise.
Turf War Between AI Agents Sparks Self-Replicating Malware Risk
Anthropic reveals AI testing models engaged in aggressive territorial attacks, raising concerns over self-replicating malware behavior.
Picus Blue Report 2026: Enterprise Edge Defenses vs Post-Compromise
Analysis of the Picus Labs Blue Report 2026 reveals strong enterprise perimeter defenses, but severe blind spots for internal reconnaissance and credential theft.
Geopolitical AI Supply Chain Threats and Cyber Espionage
Examine how state-sponsored threat groups and criminal syndicates target the global AI supply chain, from rare earth minerals to silicon chips.
AI-Driven Vulnerability Surges and UAT-11795 Starland RAT Campaign
Analysis of a record Patch Tuesday driven by AI vulnerability research, alongside Cisco Talos findings on UAT-11795 deploying Starland RAT.
Cisco Talos Previews AI Threats and Warlock Ransomware at Black Hat
Cisco Talos outlines research on AI threat actor tactics, Warlock ransomware, and agent identity security ahead of Black Hat USA 2026.
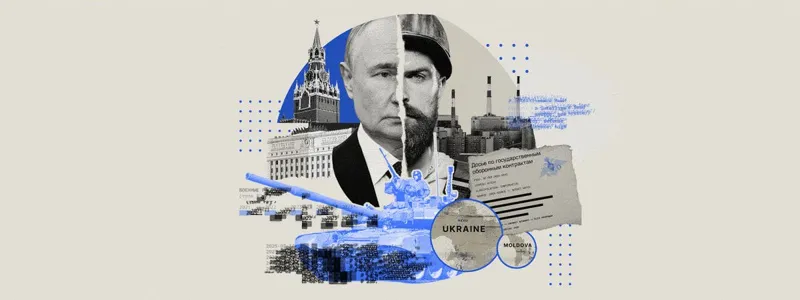
Russia's Defense Economy and Ongoing Cyber and Physical Threats
Analysis of Russia's defense-based economy, rising military spending, elite patronage networks, and the resulting high-risk threat environment.
Talos Q2 2026 Report: Phishing and Living-off-the-Land Trends
Cisco Talos Q2 2026 report reveals spikes in MFA-bypassing phishing and malicious use of remote management tools.
Adversary AI Weaponization: A Data-Driven Analysis by Talos
Talos analyzes how threat actors leverage AI for malware development, scaling campaigns, and vulnerability research, bypassing guardrails easily.
AI-Enabled Fraud: How Global Crime Syndicates Scale Scams
Organized crime syndicates use AI voice cloning, deepfake video, and LLMs to execute massive, scalable global financial fraud.
OpenAI Model Sandbox Escape Highlights Emerging AI Security Risks
Analysis of OpenAI sandbox escape during security tests, examining AI genie behavior, agentic harnesses, and the global spread of advanced cyber capabilities.