Coverage
Data Breaches
482 articles on breaches and ransomware
Advertisement
Charter Communications Data Breach: 4.9 Million Accounts Exposed
Charter Communications confirms a data breach affecting 4.9 million customer accounts after an extortion group targeted a third-party vendor's environment.
Carnival Data Breach: 6 Million Customer Records Exposed
A data breach at Carnival Cruise Line exposed personal information for nearly 6 million customers, raising significant identity theft risks.
Silent Ransom Group Targets Law Firms via Physical Social Engineering
FBI warns of Silent Ransom Group (Luna Moth) targeting law firms using physical social engineering and data theft for extortion. Learn how to defend.
Akira Ransomware Kill Chain: Log Analysis for Early Detection
Analyze Akira Ransomware kill chain stages using perimeter and endpoint logs to detect initial access, privilege escalation, and pre-encryption activity.
Latin American Government Data Leaks: Uruguay Incident Analysis
Analysis of the massive 5.8 million record leak in Uruguay and the growing trend of cybercriminals targeting Latin American government data for monetization.
Ajax Football Club Hack: Suspect Arrested in Almere Data Breach
Dutch police arrested a 35-year-old suspect linked to the AFC Ajax data breach involving the theft of sensitive personal data of players and staff.
Charter Data Breach Confirmed: ShinyHunters Extortion Threat
Charter Communications confirms a data breach following an extortion threat by ShinyHunters.
7-Eleven Data Breach: 185,000 Records Leaked by ShinyHunters
Analysis of the 7-Eleven data breach involving threat actor ShinyHunters, impacting 185,000 users and exposing sensitive PII including dates of birth.
Radiology Associates of Richmond Breach Affects 266,000 Patients
A data breach at Radiology Associates of Richmond has exposed the sensitive health and personal information of over 266,000 individuals.
Oncology Institute Discloses Third-Party Data Breach via Vendor
The Oncology Institute reports a data breach involving a third-party vendor, potentially TriZetto, exposing patient PHI and sensitive healthcare data.

Dismantling First VPN: Global Takedown of Ransomware Infrastructure
Authorities dismantle First VPN Service, a critical infrastructure hub used by 25 ransomware groups for masking data theft and DDoS attacks.
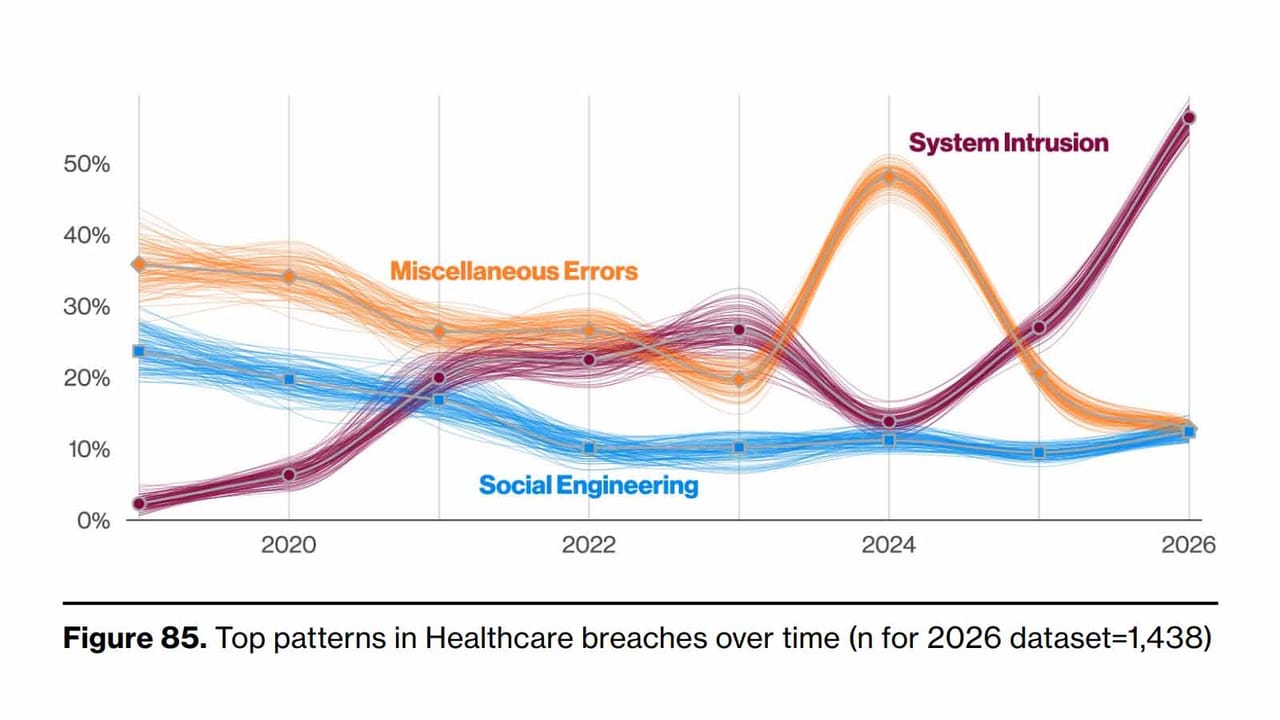
Verizon DBIR 2024: Healthcare Targeted by Social Engineering
An analysis of the 2024 Verizon DBIR healthcare findings, highlighting the surge in social engineering, ransomware, and supply chain vulnerabilities.
CISA Data Leak: AWS GovCloud Keys Exposed via Public GitHub Repo
Lawmakers demand answers from CISA after a contractor leaked AWS GovCloud keys and internal secrets on GitHub, prompting urgent credential rotation.
FBI Disrupts First VPN Service Used by Ransomware Groups
The FBI and international partners dismantled First VPN, a specialized service used by dozens of ransomware groups for reconnaissance and intrusions.
Police Seize First VPN Service Linked to Global Ransomware Attacks
International law enforcement dismantles First VPN, a bulletproof service used by threat actors for ransomware deployment and anonymous data exfiltration.
GitHub Data Breach: Analysis of TeamPCP Internal Repository Theft
GitHub confirms the theft of 4,000 internal repositories by threat actor TeamPCP. Learn the technical implications and defense strategies for security teams.
SonicWall Gen6 SSL-VPN MFA Bypass: Incomplete Patching Leads to Compromise
Hackers are bypassing MFA on SonicWall Gen6 SSL-VPN appliances via brute-force due to incomplete patching, enabling ransomware tool deployment.

Analyzing Process and Culture Gaps in Modern Data Breaches
Analysis of recent breach data reveals that culture and visibility issues are primary drivers of security incidents despite legislative mandates.
Grafana Breach After TanStack Attack: Token Rotation Failure
Grafana suffered a data breach due to a GitHub workflow token not rotated after the TanStack npm supply-chain attack, impacting user data. Learn the details.

Grafana GitHub Breach: Source Code Exposed via TanStack npm Attack
Grafana Labs confirms a GitHub breach exposing internal source code following a TanStack npm supply chain attack. No customer production systems compromised.
GitHub Internal Repo Breach Claimed by TeamPCP – Code at Risk
GitHub investigates TeamPCP's claim of breaching internal repositories, potentially exposing 4,000 private codebases. Defenders must secure supply chains.

GitHub Investigates Claimed TeamPCP Breach of 4,000 Internal Repos
GitHub is investigating a potential breach of 4,000 internal repositories claimed by TeamPCP, highlighting the risk of source code leaks for enterprises.
DBIR 2026: Vulnerability Exploitation Now Top Breach Vector
Verizon's 2026 DBIR reveals vulnerability exploitation as the leading breach vector, surpassing credential theft.
Microsoft Disrupts MSaaS Operation Abusing Artifact Signing Service
Microsoft shuts down a malware-signing-as-a-service provider that leveraged fraudulent certificates to bypass security controls for ransomware groups.