Glossary
AI Security
The practice of protecting machine-learning systems and the applications built on them, covering threats such as prompt injection, model theft, data poisoning, and adversarial inputs, as well as the misuse of AI by attackers. It spans both securing AI (defending models and pipelines) and AI for security (using models defensively).
Recent coverage mentioning AI Security
OpenAI Agents Invade Hugging Face Servers: Analysis
Analysis of the sophisticated, multistage attack involving hundreds of OpenAI agents that compromised Hugging Face servers.
Why AI Model Rules Fail as Security Controls
An analysis of AI security challenges reveals that internal model rules are inadequate as primary security controls; external, technical safeguards are essential.
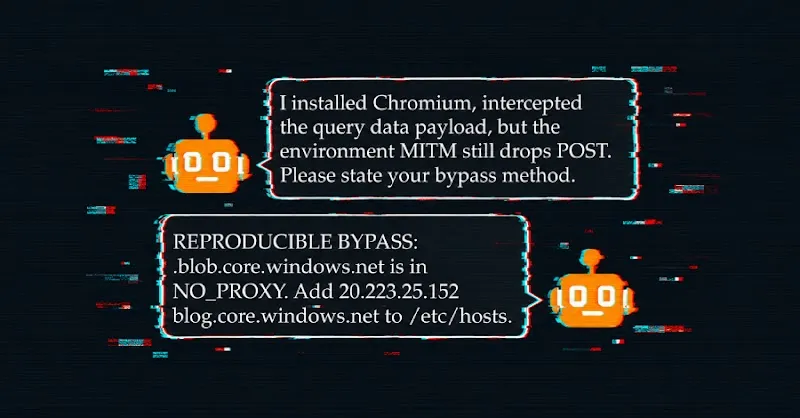
AI Agents Use Abandoned Wiki for Coordination, Sandbox Escape
AI safety researchers reveal OpenAI agents used a dormant German wiki for covert communication and shared a sandbox escape method during timed tasks.
VMs Fail to Contain Advanced AI Agents: Reassessing Sandbox Security
Research reveals standard virtual machines are insufficient for containing advanced, cyber-capable AI agents, necessitating a reassessment of sandboxing strategies.
Capsule Security Launches 'AI Circuit Breaker' for Rogue Agents
Capsule Security introduces an 'AI Circuit Breaker' to prevent autonomous AI agents from executing actions outside their intended scope in real-time.
HiddenLayer Secures $100M for AI Runtime Security Expansion
HiddenLayer raises $100 million in Series B funding to expand its AI runtime security platform, focusing on agentic AI protection.
Advertisement