Glossary
Attribution
The process of identifying the individual, group, or nation responsible for a cyberattack, typically based on technical indicators (malware code reuse, infrastructure overlap), tradecraft (TTPs), and geopolitical context. Attribution is inherently difficult and often expressed with varying confidence levels because attackers can plant false flags.
Recent coverage mentioning Attribution
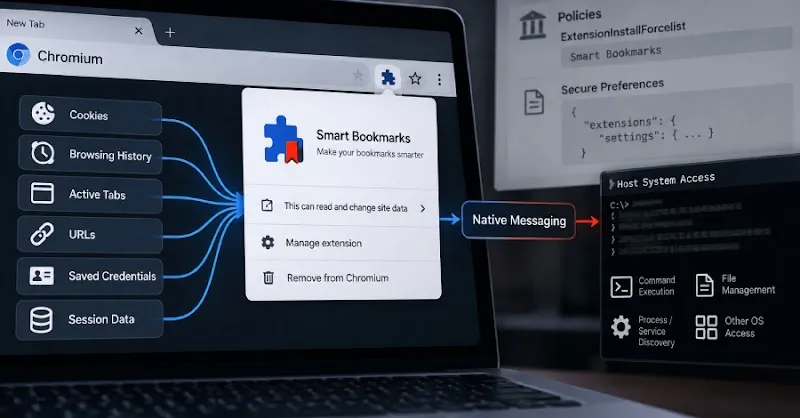
PEEP Backdoor Turns Browsers into OS Command Execution Tools
PEEP toolkit leverages Chrome and Edge as post-compromise backdoors, enabling host command execution, data exfiltration, and session hijacking.
Leaked Russian Cyber-Ops Training Exposes Institutional Pathways
Leaked materials reveal Russia's institutional system for generating cyber capabilities, linking university recruitment to GRU and Sandworm units for diverse operations.
Malicious PE Stats: Compiler Analysis of Malware Samples
Analysis of 1.3TB of malware samples examines PE headers, compiler trends, and tools used by attackers over a multi-year dataset.
Massive DDoS Disrupts Norway Government Digital Services
Norway's Digitalization Agency (Digdir) services, including e-IDs, face ongoing disruptions from a massive DDoS attack. No data breach reported.
AI-Powered PLC Attacks Target Critical Infrastructure
U.S. agencies warn that threat actors are using AI to target internet-exposed Siemens S7 Series PLCs in critical infrastructure sectors.
North Korea's Sapphire Sleet Targets Rust Supply Chain via arrayref Crate
North Korean actor Sapphire Sleet compromised a Rust maintainer's account to publish malicious `arrayref` crate versions, targeting the Rust supply chain.
Advertisement