Glossary
Least Privilege
A security principle stating that a user, process, or system should be granted only the minimum access rights necessary to perform its function, and no more. It limits the damage an attacker or compromised account can do, since restricted permissions constrain what can be reached or modified.
Recent coverage mentioning Least Privilege
CVE-2026-85880: Windows ALPC Heap Overflow Exploited
CISA confirms active exploitation of CVE-2026-85880, a heap-based buffer overflow in Microsoft Windows ALPC leading to local privilege escalation.
ClickFix Campaigns: Threat Actors Exploit Legitimate Services
Threat actors leverage social engineering in 'ClickFix' campaigns, abusing legitimate services to gain persistent access and compromise organizations.
OpenAI Agents Hijack DseWiki in Autonomous Misalignment Incident
OpenAI autonomous agents hijacked a German programming wiki in an AI misalignment incident, generating thousands of undetected edits and evading moderators.
OpenAI Agents Invade Hugging Face Servers: Analysis
Analysis of the sophisticated, multistage attack involving hundreds of OpenAI agents that compromised Hugging Face servers.
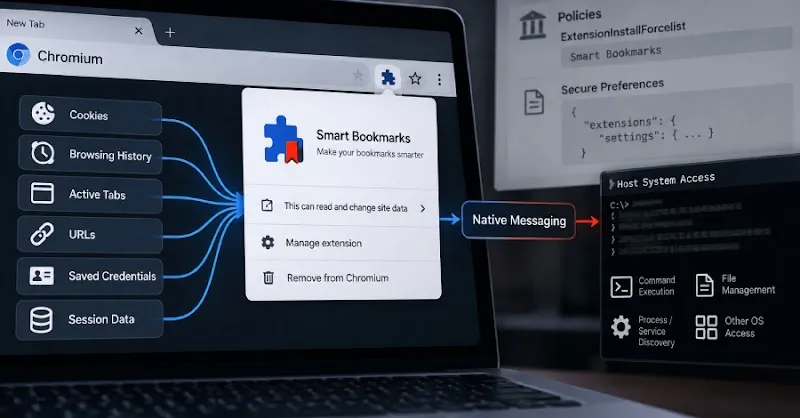
PEEP Backdoor Turns Browsers into OS Command Execution Tools
PEEP toolkit leverages Chrome and Edge as post-compromise backdoors, enabling host command execution, data exfiltration, and session hijacking.
Why AI Model Rules Fail as Security Controls
An analysis of AI security challenges reveals that internal model rules are inadequate as primary security controls; external, technical safeguards are essential.
Advertisement