Glossary
Patch Tuesday
The unofficial term for the second Tuesday of each month, when Microsoft, and several other vendors that align with it, routinely release security patches. It gives IT teams a predictable schedule for testing and deploying updates, though critical vulnerabilities are sometimes patched out-of-band before the next scheduled release.
Recent coverage mentioning Patch Tuesday
Microsoft KB5122878: Critical Windows 10 ESU/LTSC Security Update
Microsoft's KB5122878 delivers crucial security patches for Windows 10 ESU/LTSC, addressing actively exploited zero-days and 966 vulnerabilities.
CVE-2026-62911: Exchange Servers Vulnerable to Mailbox Hijack
Nearly 22,000 Microsoft Exchange Servers remain unpatched against CVE-2026-62911, an auth bypass allowing mailbox hijack attacks.
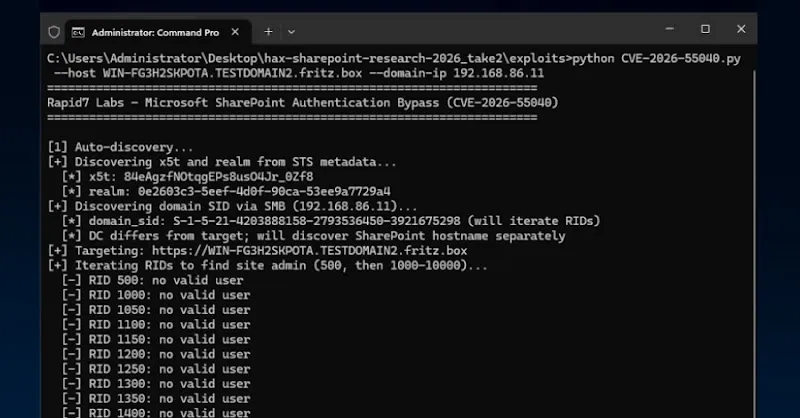
CVE-2026-55040: Critical SharePoint Auth Bypass Exploited After PoC
Attackers exploit CVE-2026-55040, a critical authentication bypass in Microsoft SharePoint, leading to data disclosure and modification.
CVE-2026-68820: Windows afd.sys Privilege Escalation Exploited
Microsoft addresses 398 vulnerabilities, including an actively exploited privilege escalation flaw in Windows' afd.sys component.
Swiss Government SharePoint Breach: 200 Accounts Compromised
Switzerland's federal IT office confirms a Microsoft SharePoint breach compromised approximately 200 accounts, leading to a swift remediation.
Microsoft & Apple Patch Critical RCEs and Auth Bypass Flaws
Microsoft released patches for critical-severity RCE and EoP flaws across Active Directory, Azure, and Teams. Apple fixed a Screen Sharing authentication bypass.
Advertisement