Glossary
Typosquatting
Registering domain names that are deliberate misspellings or close variations of legitimate, popular domains to capture traffic from users who mistype a URL, often to deliver phishing pages or malware. It is also used against software package names in dependency confusion-style supply chain attacks.
Recent coverage mentioning Typosquatting
GTIG AI Threat Tracker: Evolution of Adversarial Agentic AI
Google Threat Intelligence Group tracks threat actors shifting to agentic AI, targeting proprietary models, and abusing open source software.
North Korea's Sapphire Sleet Targets Rust Supply Chain via arrayref Crate
North Korean actor Sapphire Sleet compromised a Rust maintainer's account to publish malicious `arrayref` crate versions, targeting the Rust supply chain.
Critical: Rust `arrayref` Crate Poisoned with Infostealer Malware
Hackers compromised `arrayref`, `append-only-vec`, and `internment` Rust crates to inject infostealer malware, impacting developers and downstream projects.
npm Supply Chain Attacks: Shai-Hulud, Miasma, and CI/CD Compromises
The npm ecosystem faces escalating supply chain attacks like Shai-Hulud and Miasma RAT, leading to credential theft and widespread package compromise.
Keyv npm Supply-Chain Attack: Worm Infection and Dead-Man Switch
Analyze the Keyv/cacheable npm supply-chain worm, its AI agent execution vectors, and why immediate credential revocation can trigger payloads.
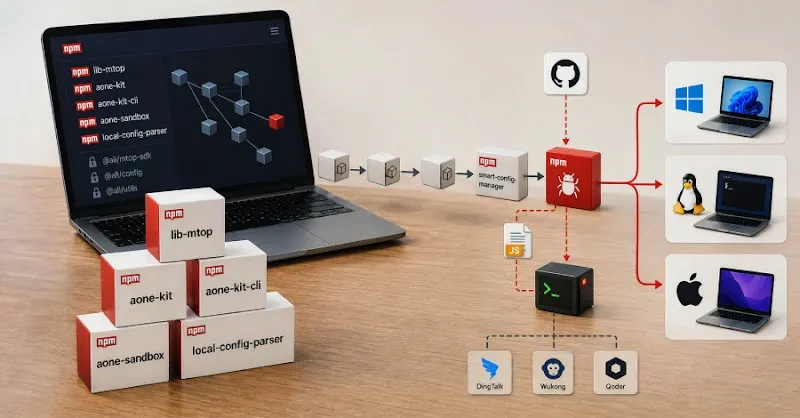
Malicious npm Packages Deliver Cross-Platform RAT to Alibaba Users
Discover how 18 malicious npm packages target Alibaba developer tools with a cross-platform remote access trojan in a supply chain attack.
Advertisement